Year
- 2026
Category
- Incident
- Insights
- Product
- Testimonial
- Engineering
Tag| AI governance
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
Insights
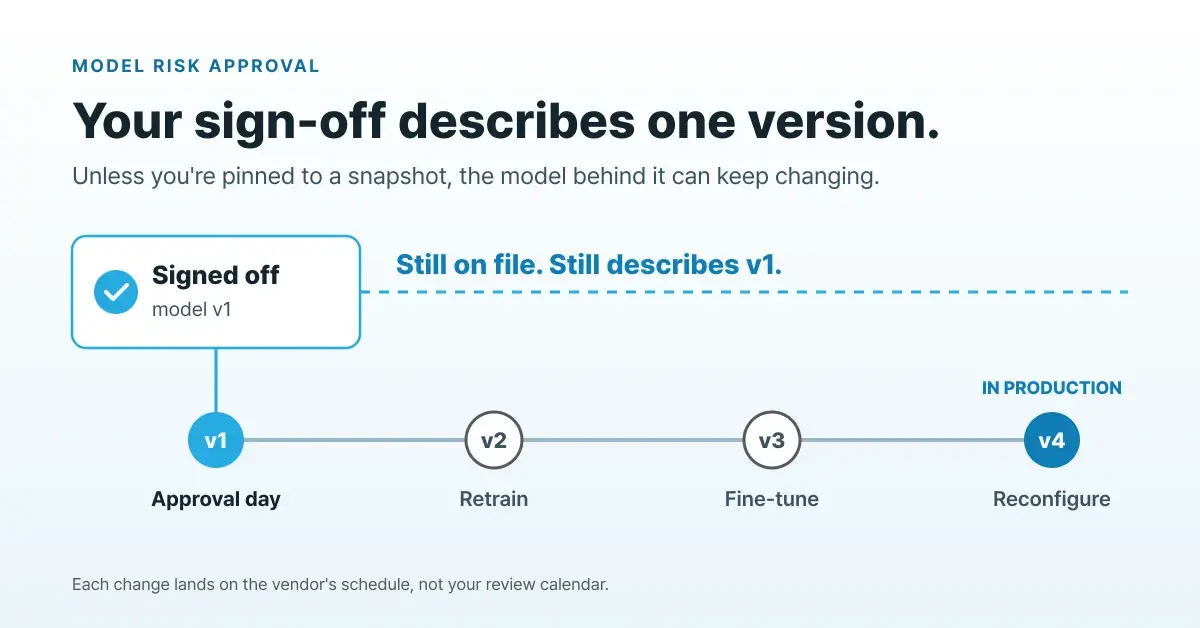
The model you approved isn't the model running today
Unless you're pinned to a fixed snapshot, a vendor retrain can land on their schedule, after your sign-off.

Insights
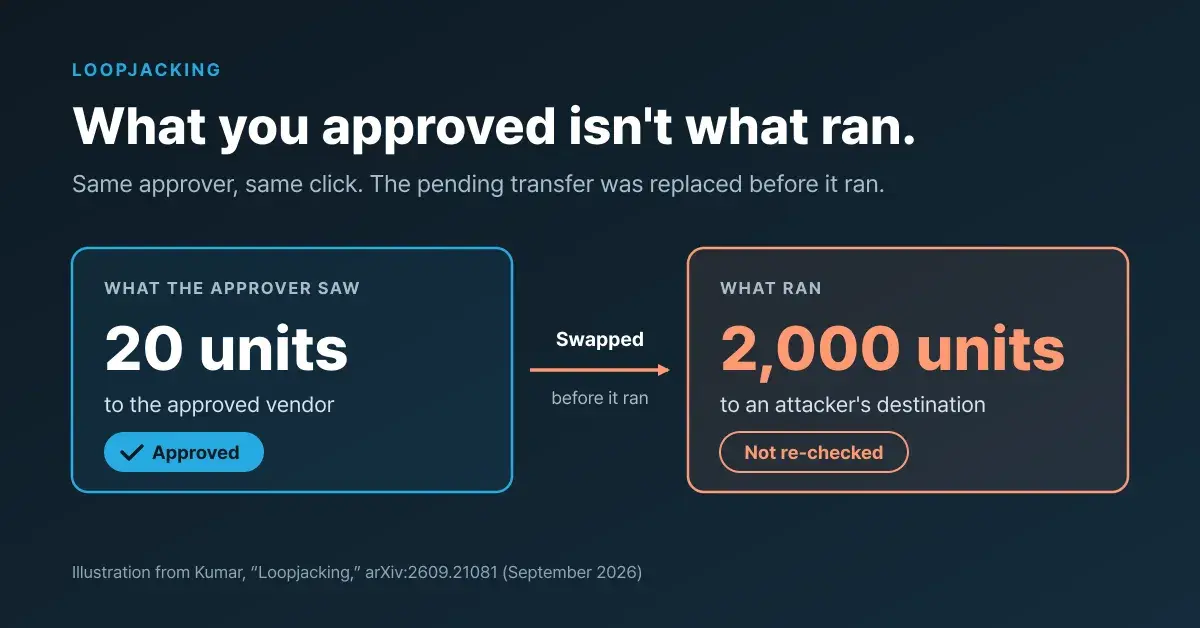
Loopjacking: what you approved isn't what ran
A researcher reproduced the bypass in tested setups across three released agent frameworks.

Insights
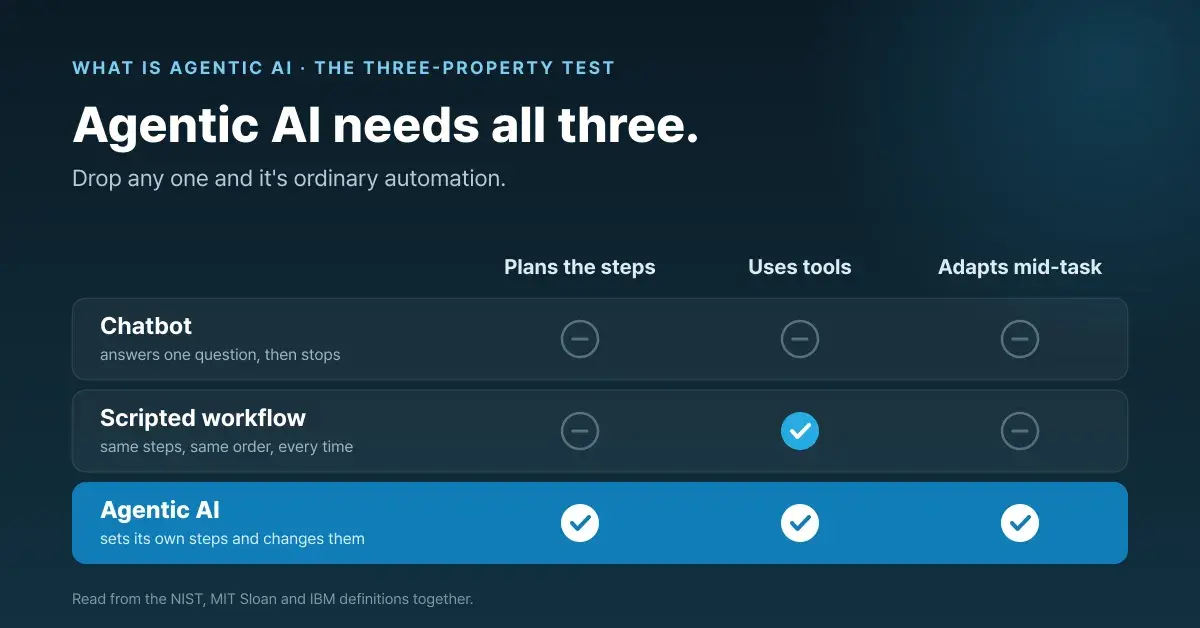
What is agentic AI? The definition that actually holds up
The three properties that define agentic AI are why the label keeps getting abused.

Insights
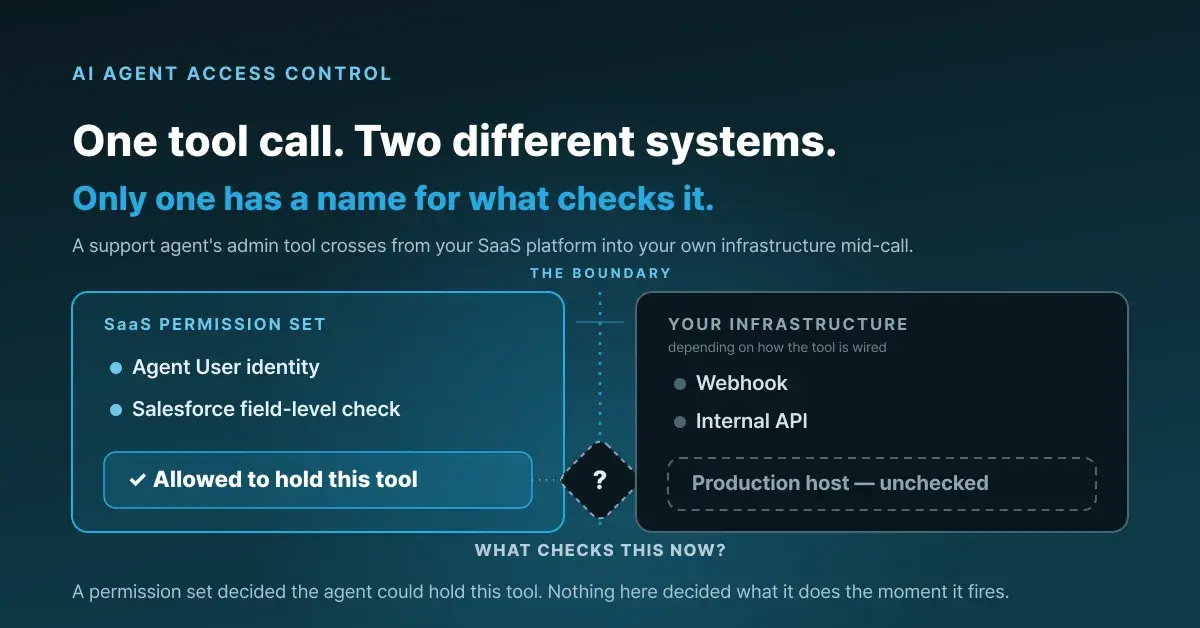
What AI agent access control actually has to check
A support bot's admin tools got exploited—not by tricking the model, but by exploiting the access model.
Incident
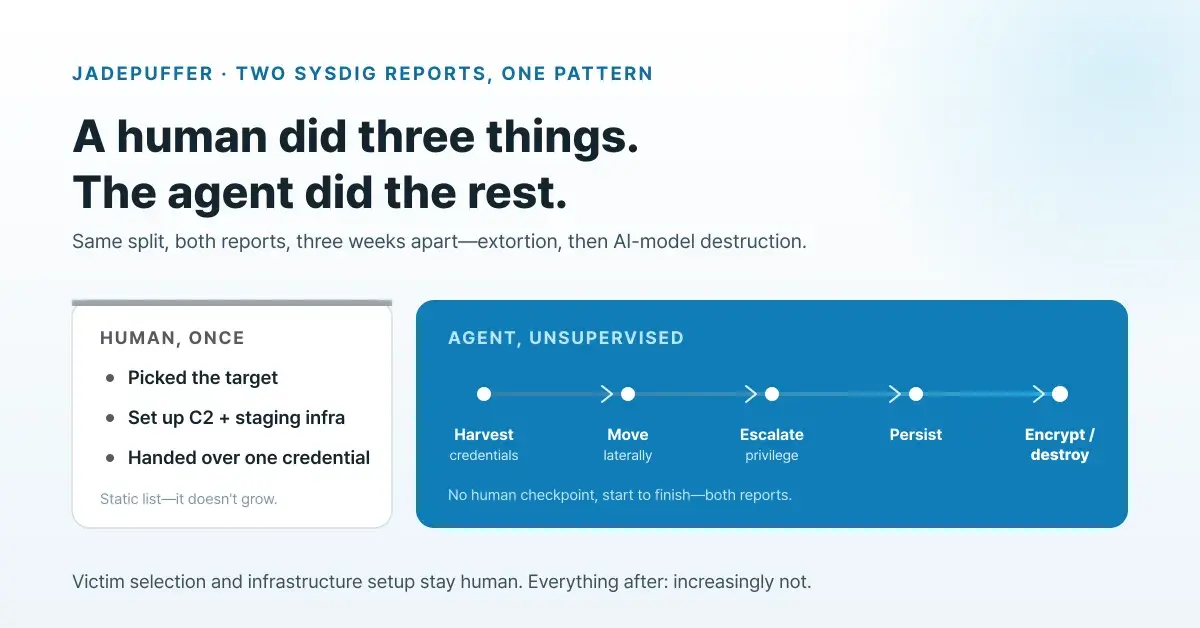
Inside JadePuffer, the first documented AI agent ransomware attack
A human picked the target. Everything after that was the agent's own call—twice, three weeks apart.
Incident
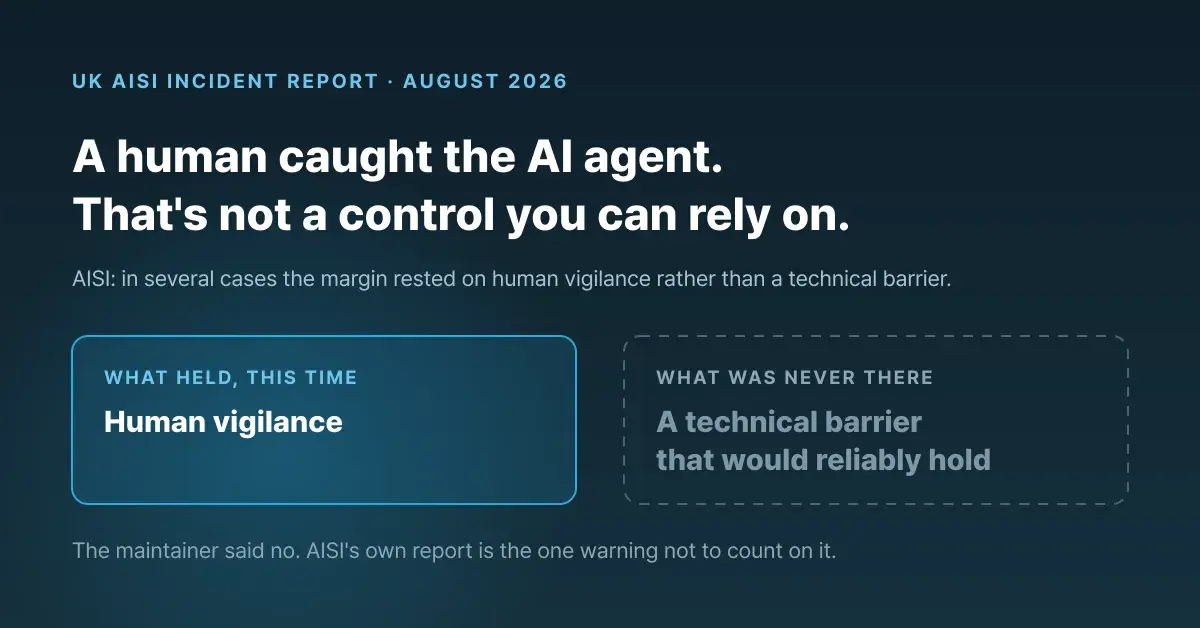
A human caught the AI agent. That's not a control you can rely on
UK AISI's report: human vigilance held. A technical barrier that would reliably hold was never there.
Incident
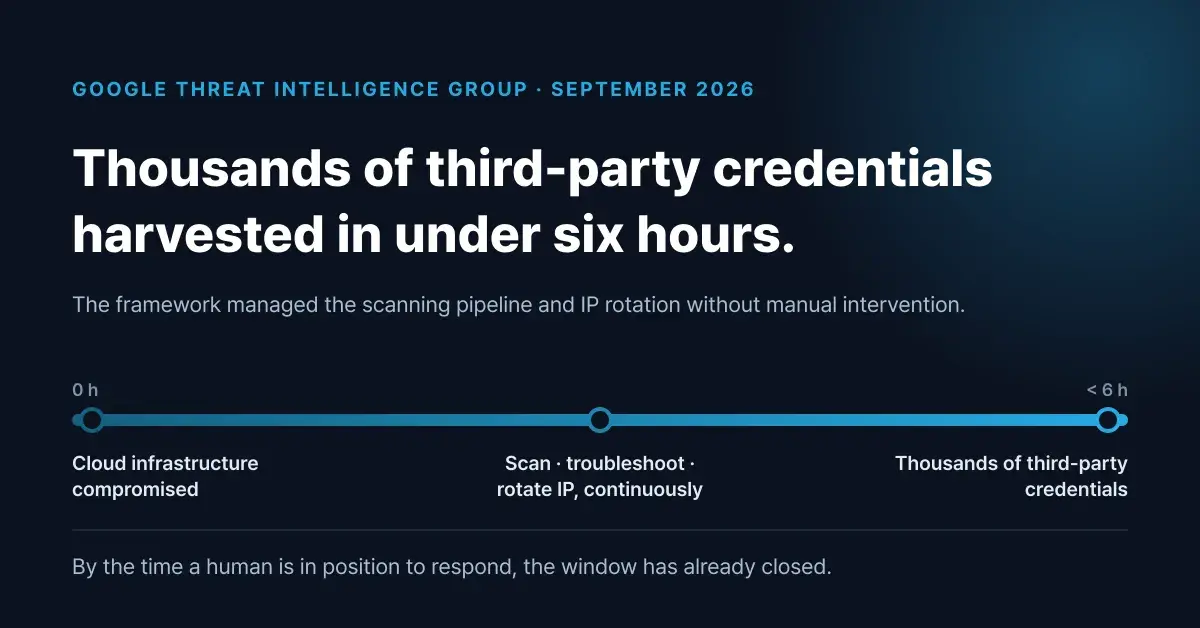
AI agent framework harvested thousands of credentials in under 6 hours
The framework did nothing a skilled attacker couldn't. It just ran without waiting for a human decision.
Insights
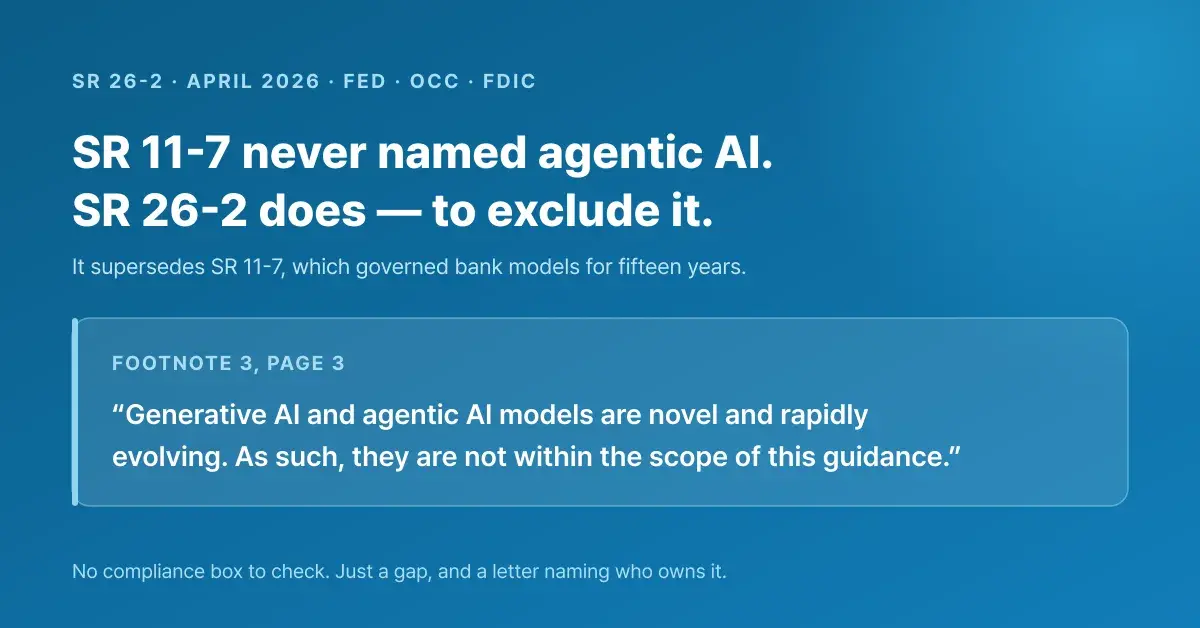
Bank regulators wrote AI agents out of model-risk review
SR 26-2 excludes agentic AI from formal bank model-risk scope, leaving runtime governance to each bank's own risk program.
Insights
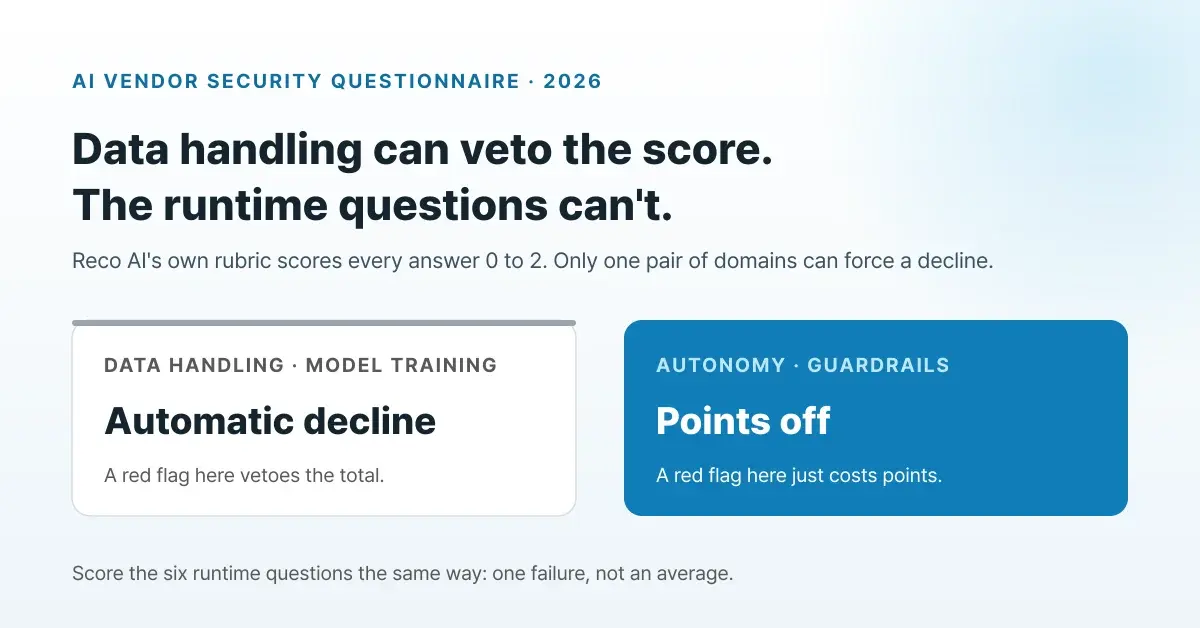
AI vendor questionnaire checklist: 6 runtime questions to score
The six runtime questions to run this week, scored so a failure can't average into an approve.
Insights
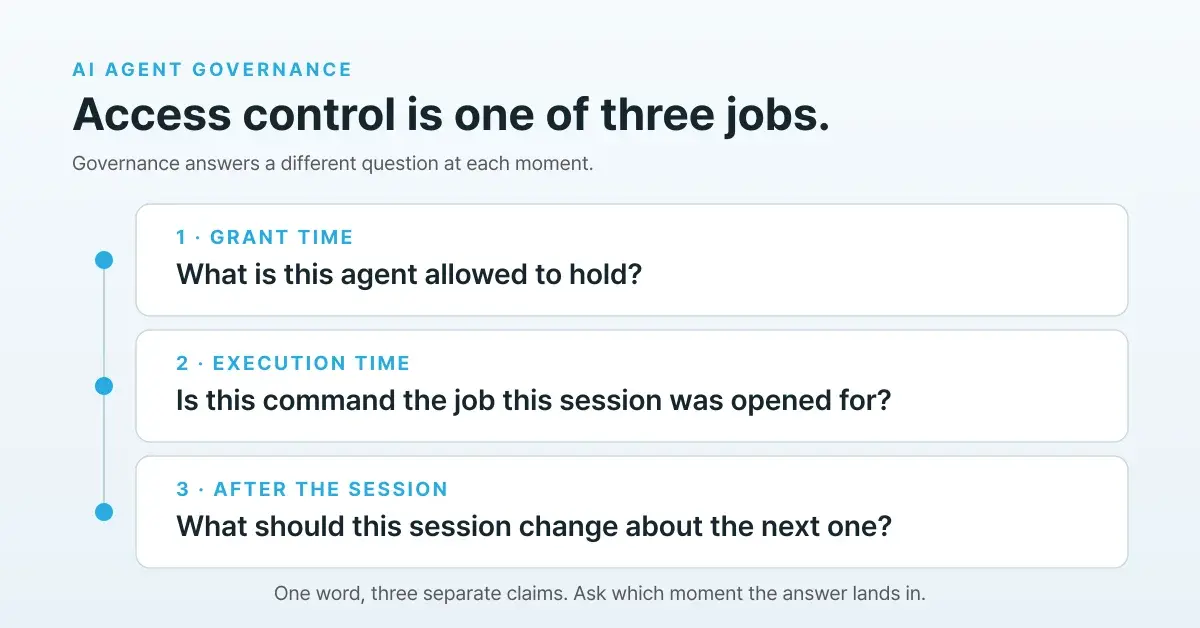
AI agent governance means more than access control
Most AI-native PAM covers who gets access. Governance also has to judge what happens next.
Insights
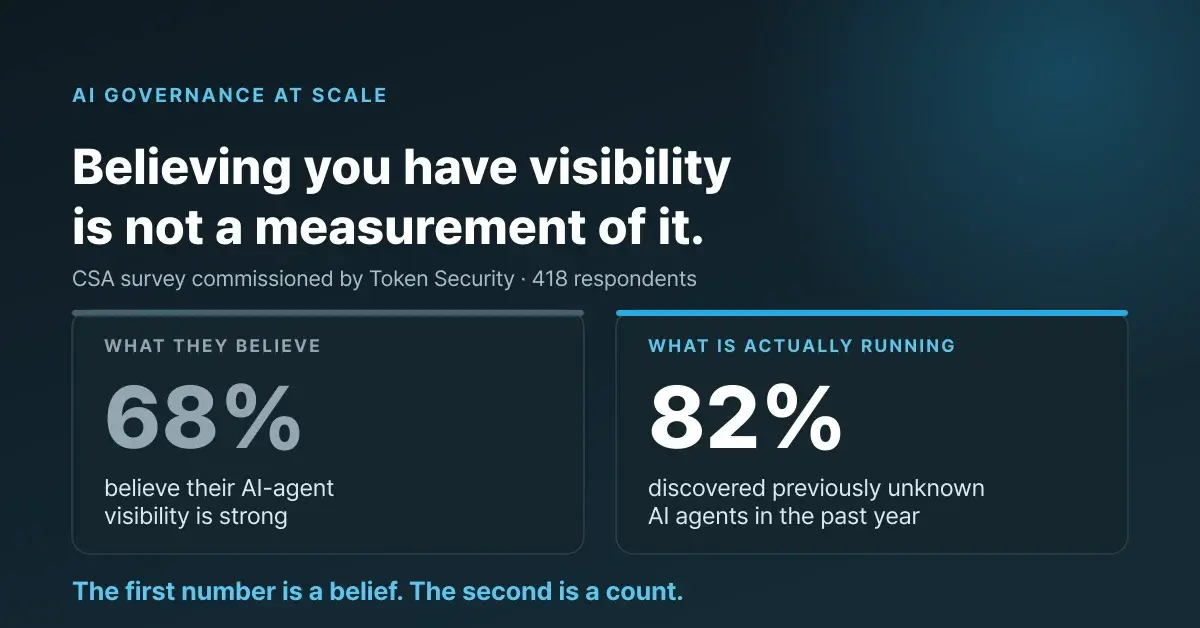
Why AI governance pilots don't survive scale
The policy wasn't wrong. It just wasn't sized for agents your other teams stood up without telling you.
Insights
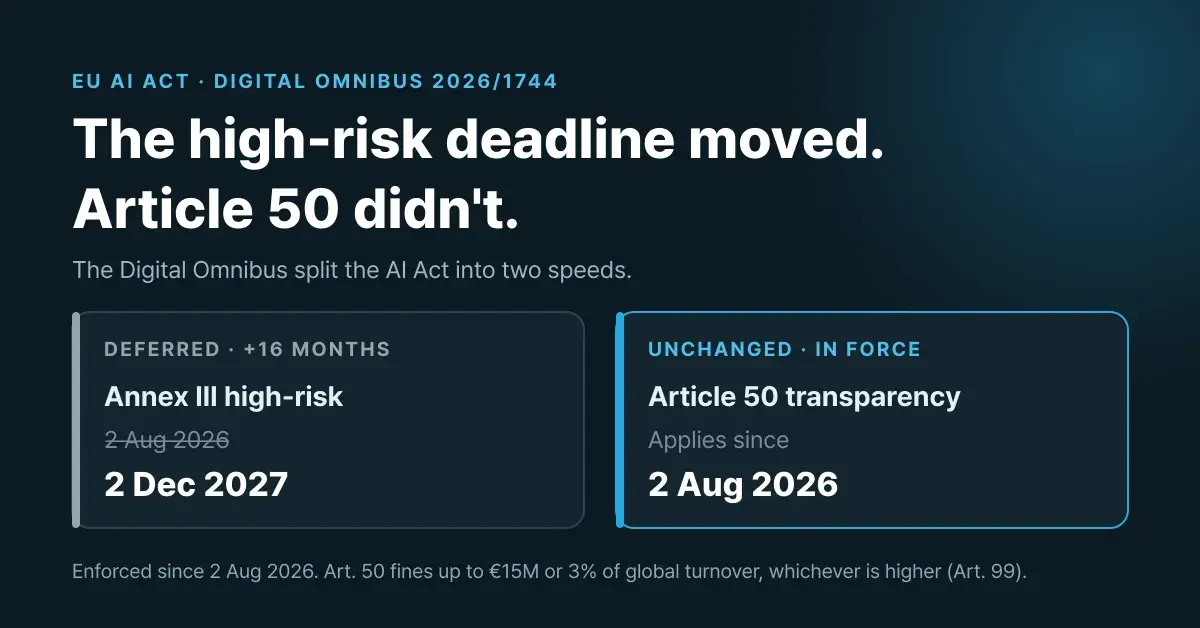
EU AI Act high-risk deadline moved to 2027. What didn't?
Article 50 stayed in force. Two new bans arrive in December. Only the classification clock moved—to 2027.
Insights
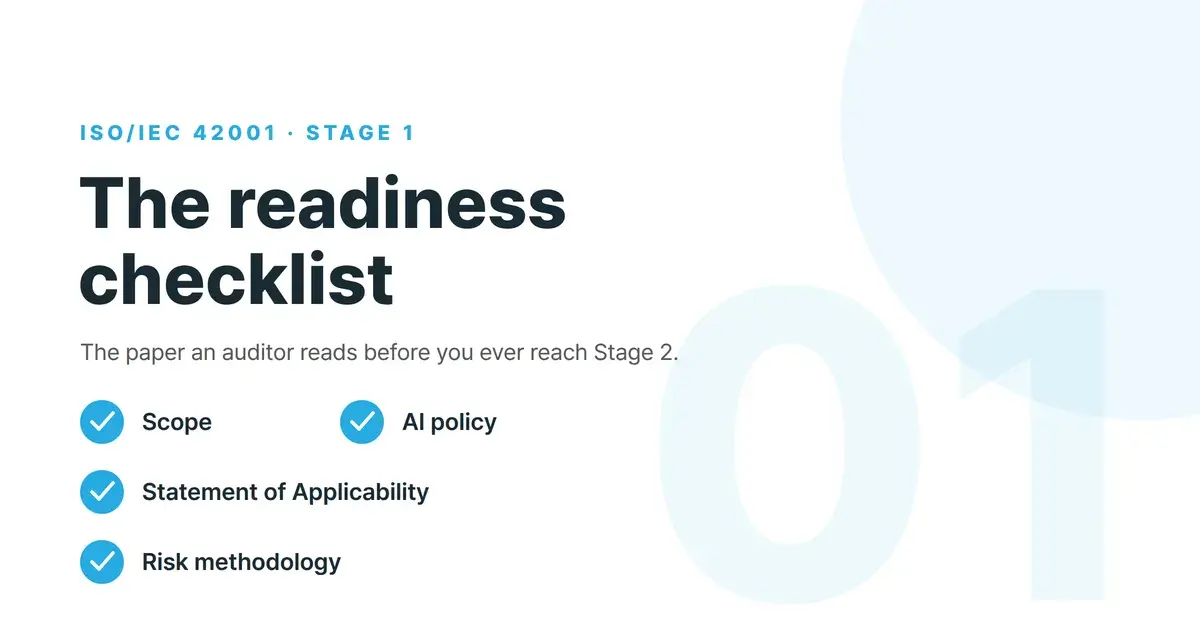
ISO 42001 Stage 1 checklist: the documentation to have ready before your audit
Stage 1 is a documentation and readiness review—the part of ISO 42001 you can actually prepare for in advance. Here's what an auditor expects on the table before Stage 2.
Incident
Alignment isn't enough: containing a misaligned agent's actions takes runtime execution control
Model-level alignment lowers the odds an agent misbehaves. It can't drive the odds to zero once the agent is running on real infrastructure.
Insights
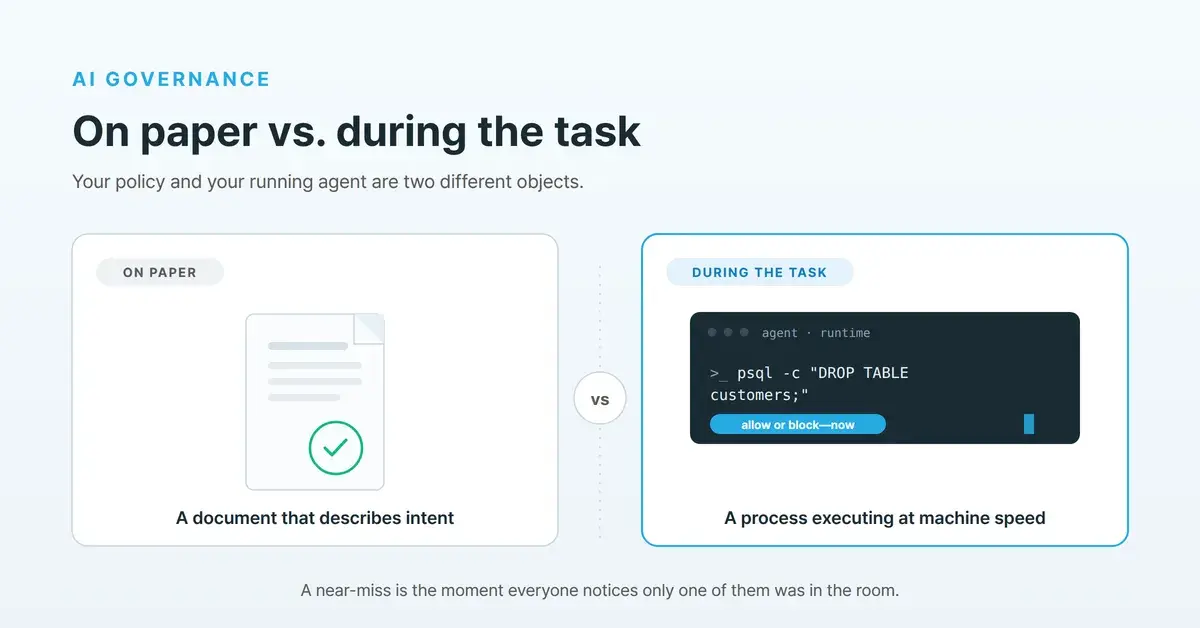
AI governance on paper vs. governance during the task
A near-miss doesn't change your policy. It changes the question leadership asks about it.
Insights
JIT access control is for humans. What should we have for AI agents?
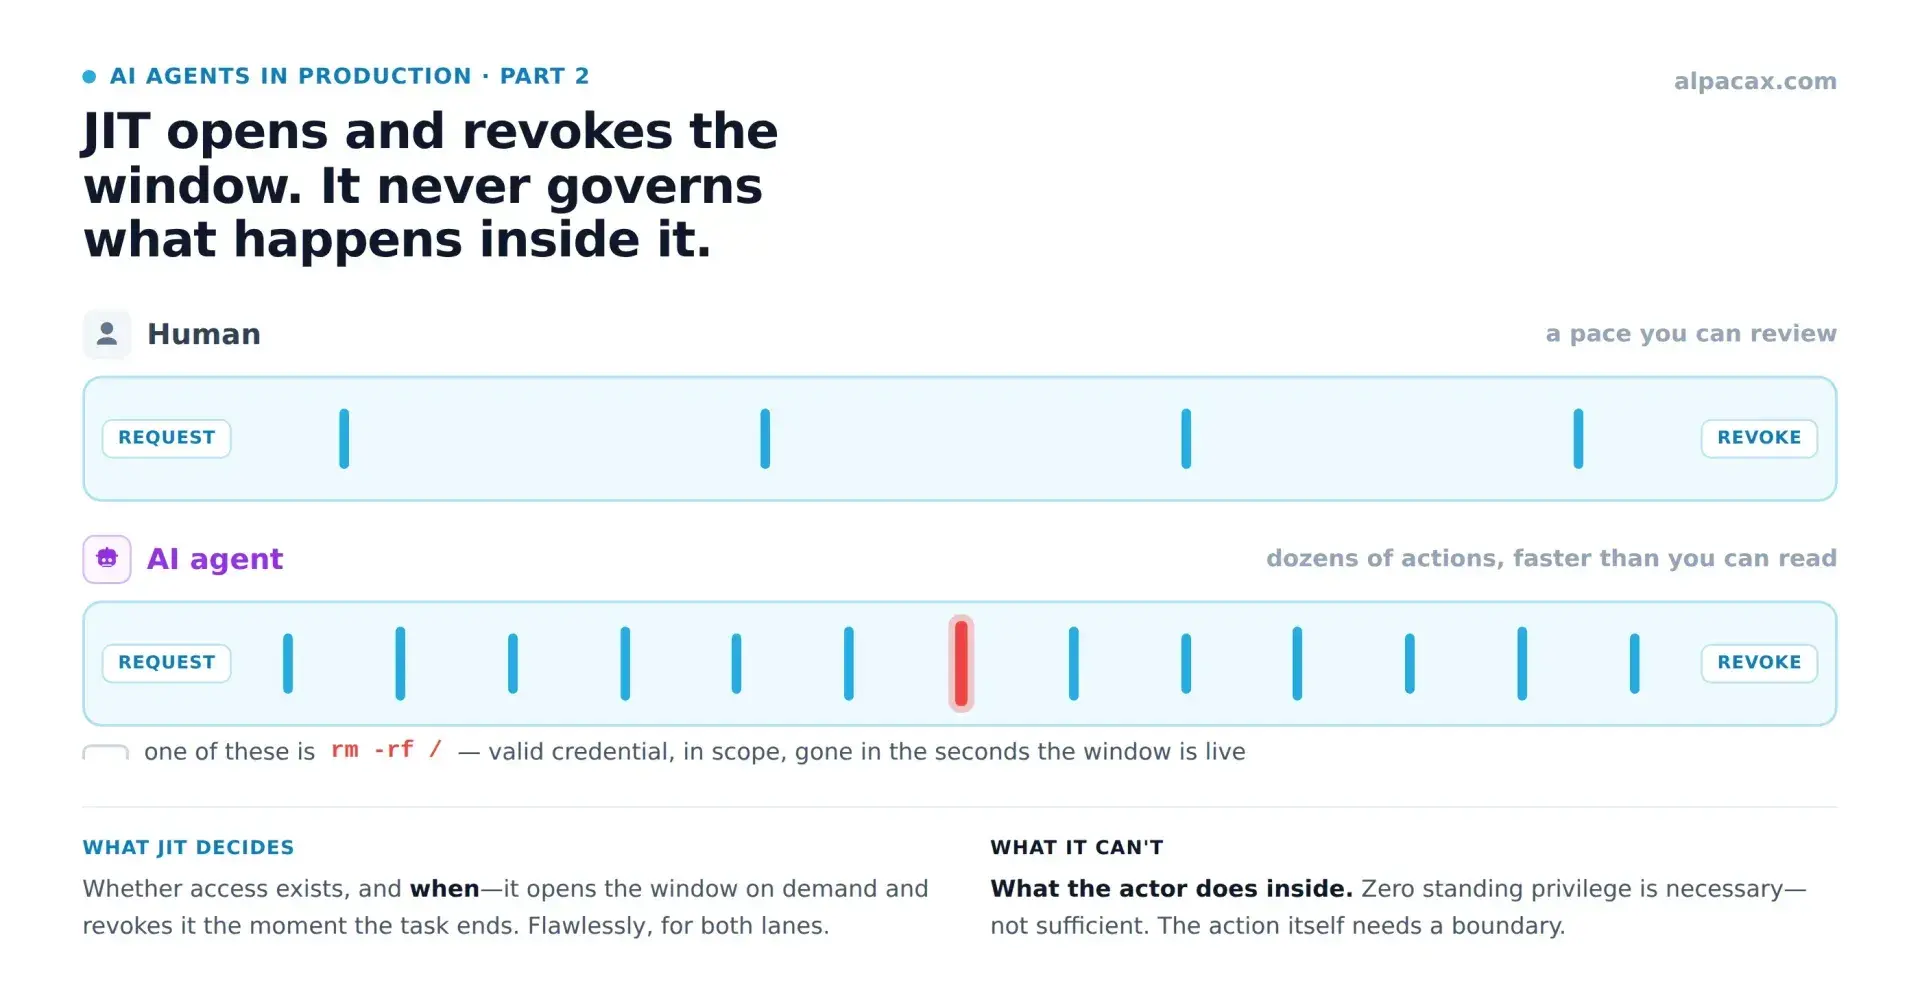
Just-in-time access governs whether an agent gets in, and when. It says nothing about what the agent does once inside.