Year
- 2026
Category
- Incident
- Insights
- Product
- Testimonial
- Engineering
Tag| Privileged access
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
Incident
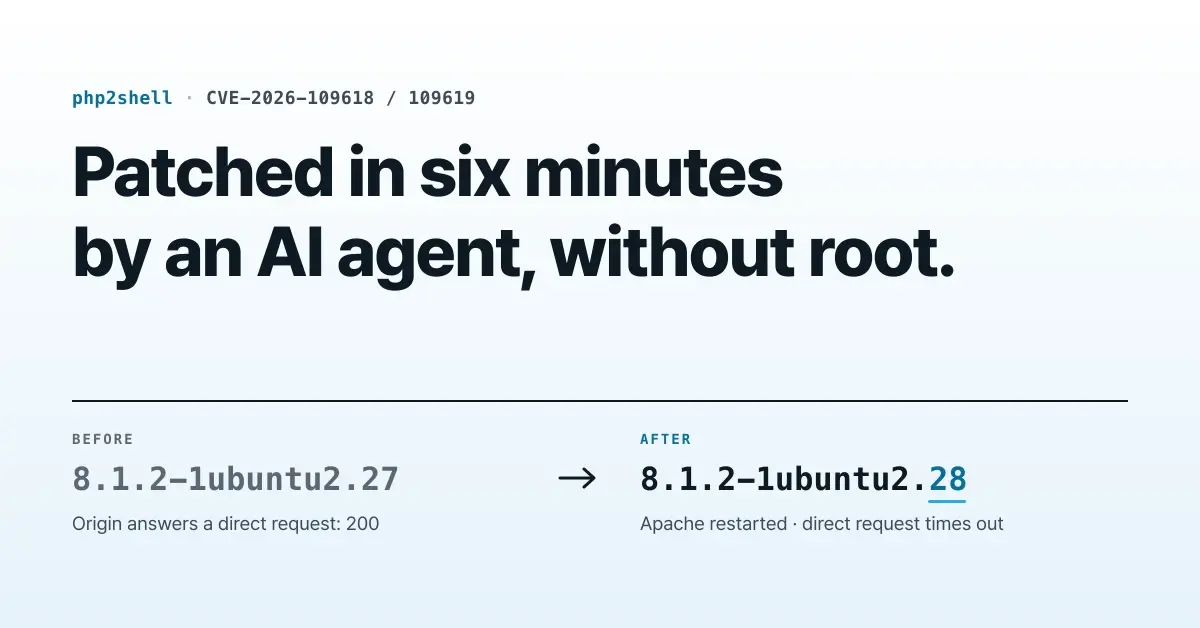
How we patched php2shell in six minutes with an AI agent
What our agent ran, why each privileged command was allowed, and the fixed builds, restart checks and origin lockdown to do it yourself.

Incident
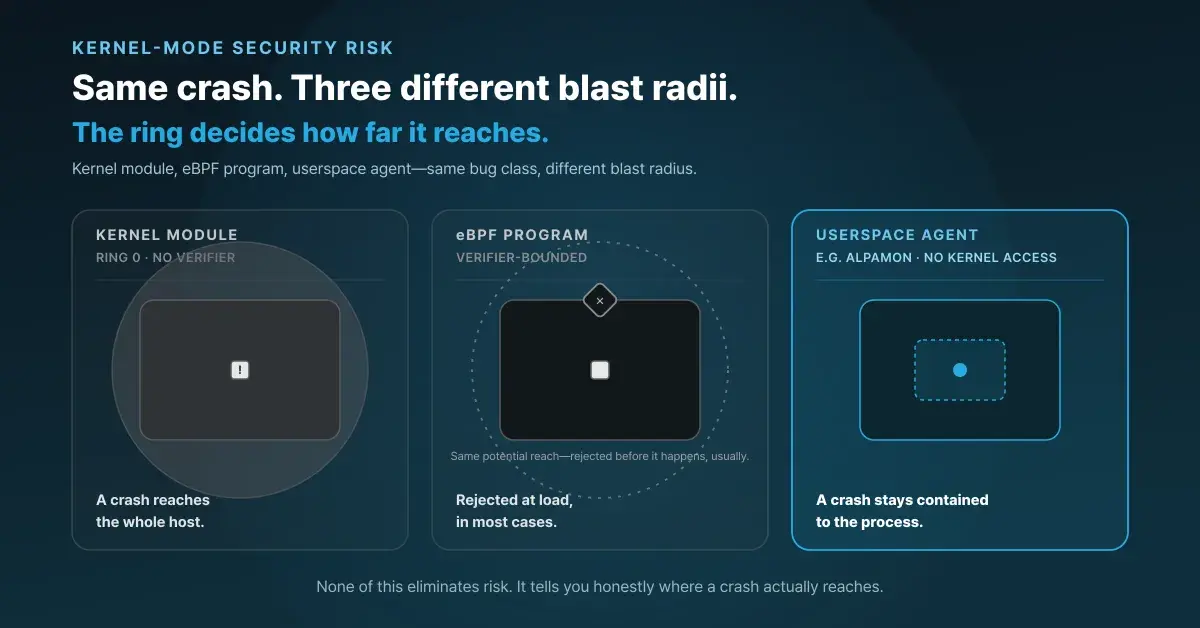
Two CrowdStrike failures, one kernel-mode security risk
CrowdStrike patched a privilege-escalation bug in 12 days. The lesson is where the privilege lived.

Insights
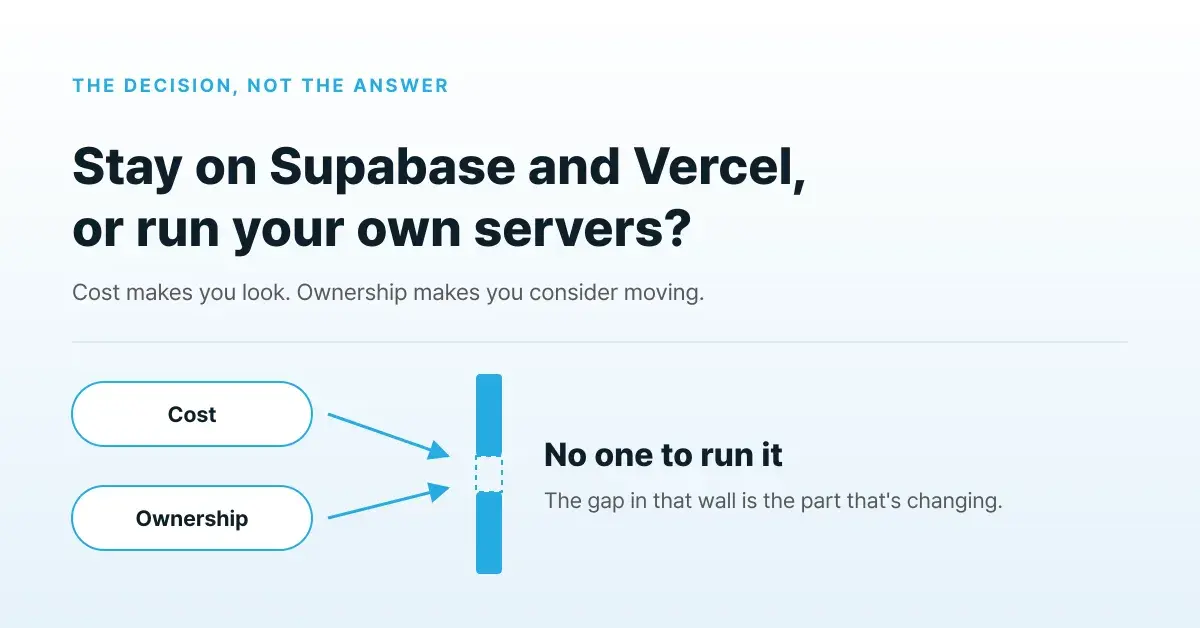
Stay on Supabase and Vercel, or run your own servers?
Cost makes you look. Ownership makes you consider moving. What usually stops you is the same thing: no one owns infrastructure. That is starting to change.

Testimonial
How BNOW fixes production without a DevOps team
BNOW has no one dedicated to DevOps. Now it hands production work to an AI agent and fixes problems itself.
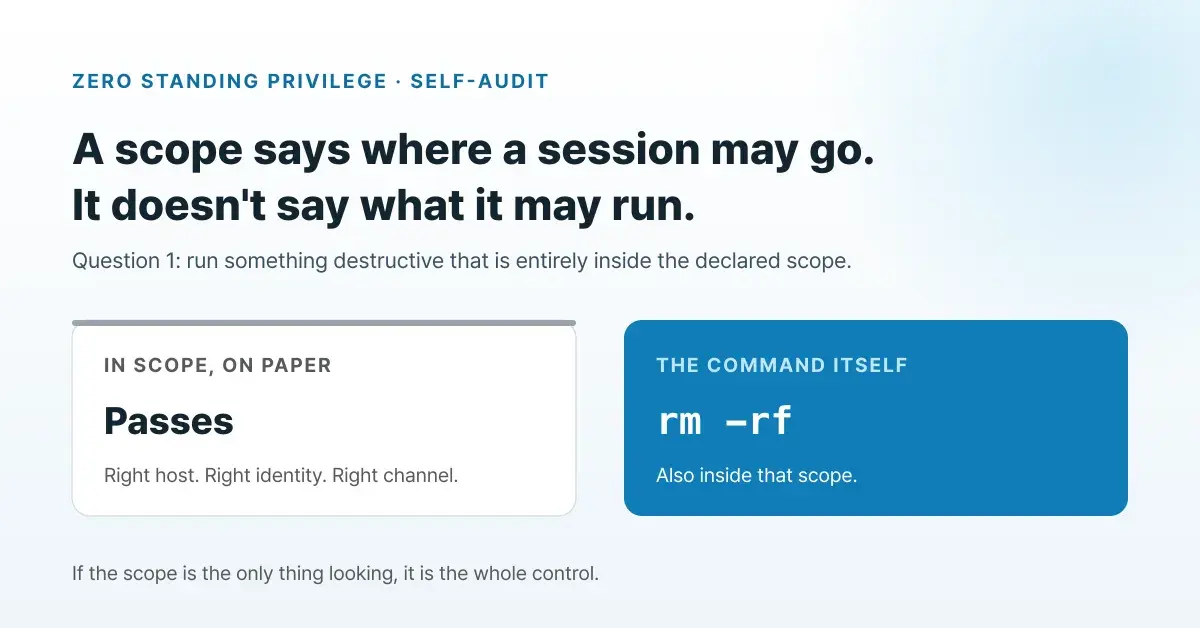
Insights
Zero standing privilege: a 7-question audit for your stack
Seven yes/no checks to run against your own stack before you trust a vendor's zero-standing-privilege claim.

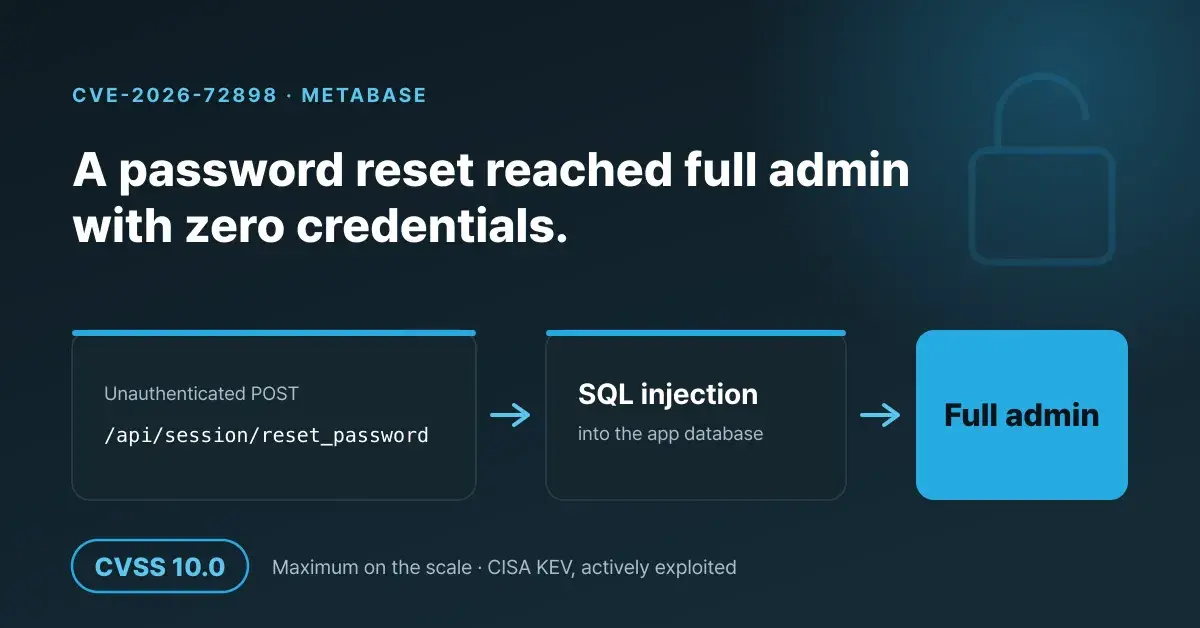
Incident
A CVSS 10.0 bug turned Metabase's password reset into full admin
CVE-2026-72898 let anyone reach full admin with zero credentials, then everything Metabase touched.
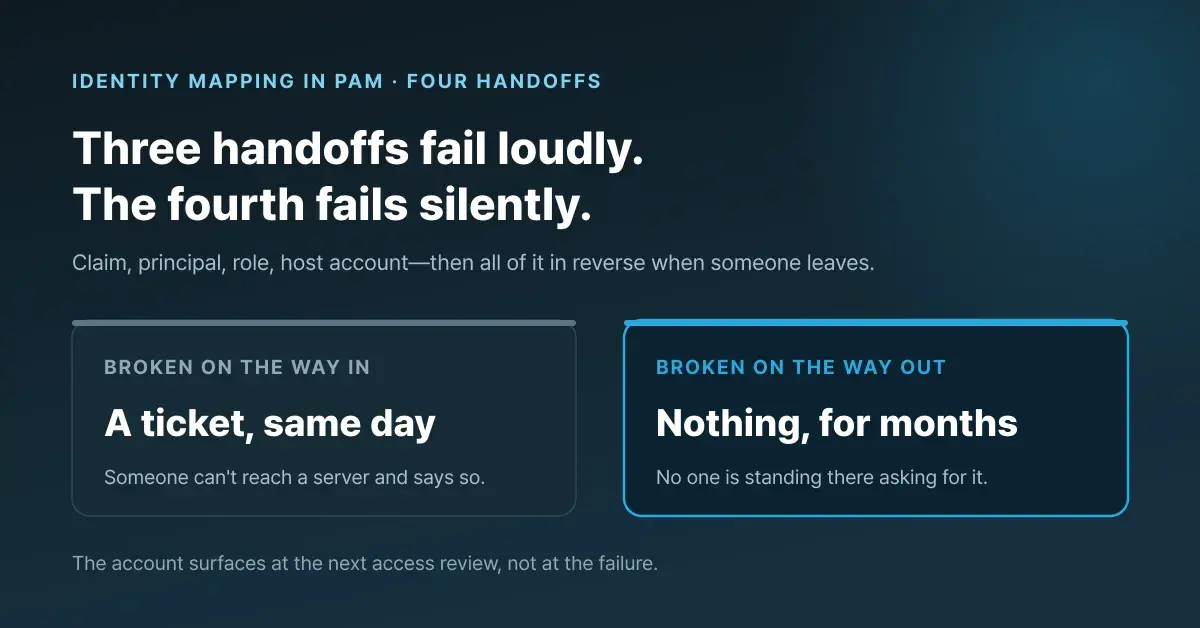
Insights
Identity mapping in PAM: four handoffs, one fails silently
A login claim refreshes at login. A leaver never logs in again—so nothing ever re-checks, and nothing gets revoked.
Engineering
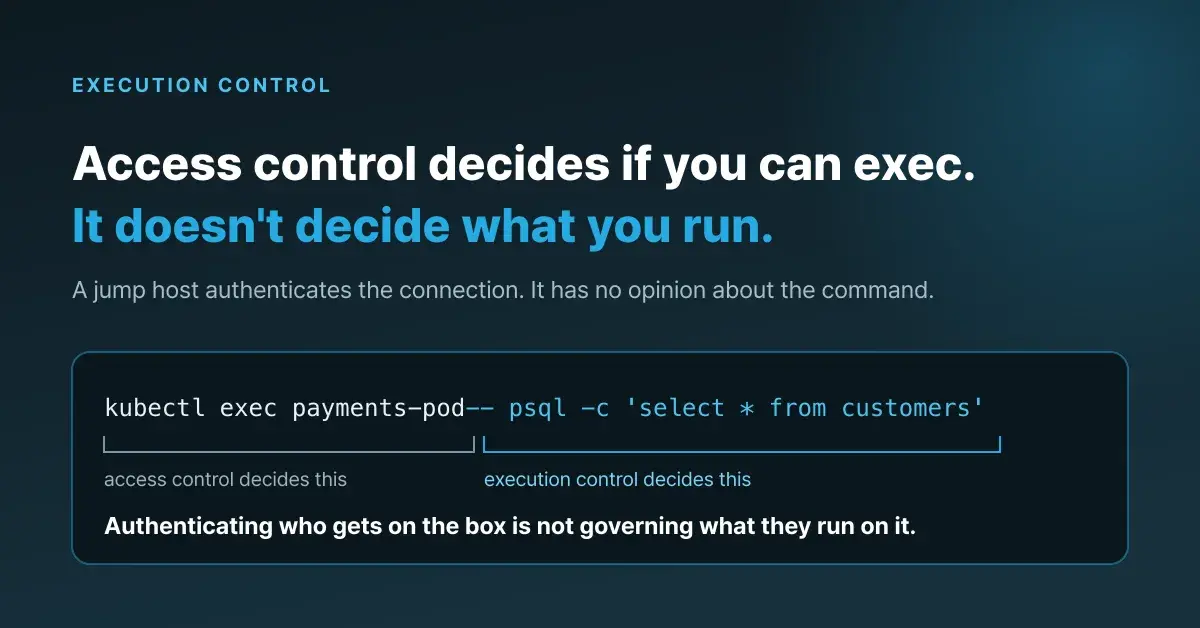
Kubernetes access control governs access, not commands
Access control checks whether you can reach a Kubernetes pod. It doesn't check whether the kubectl command you type should run.
Engineering
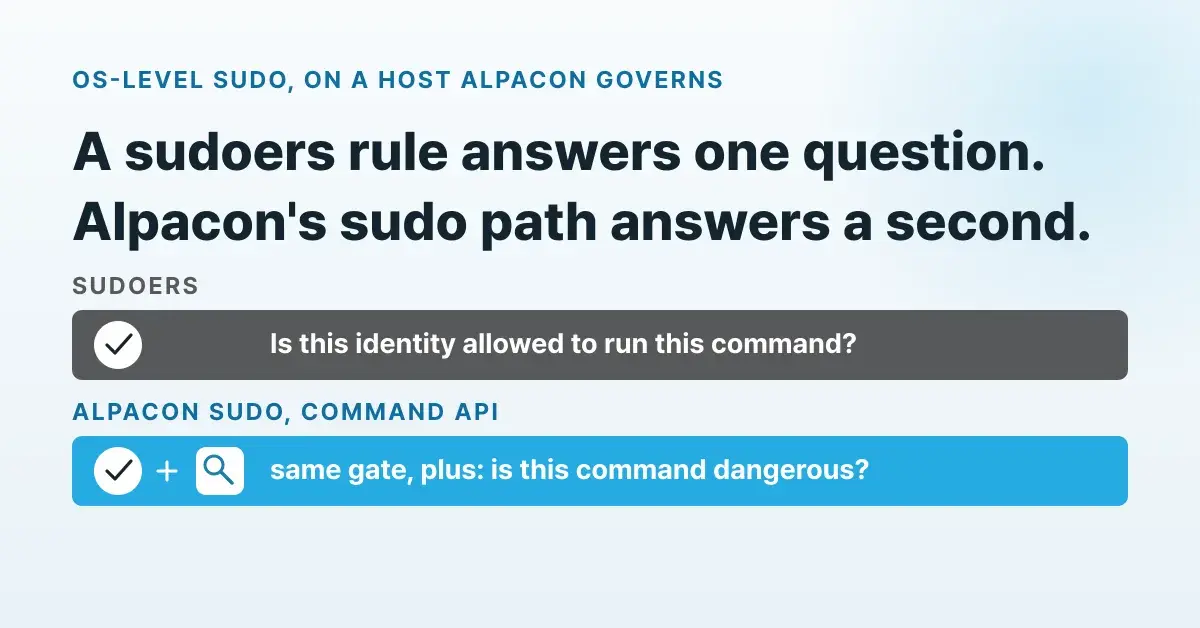
Session-scoped sudo: bind OS-level root to a session, not a sudoers file
A sudoers rule only asks who's allowed to run a command. Sudo reaching Alpacon's command API asks a second question: is this command dangerous.
Incident
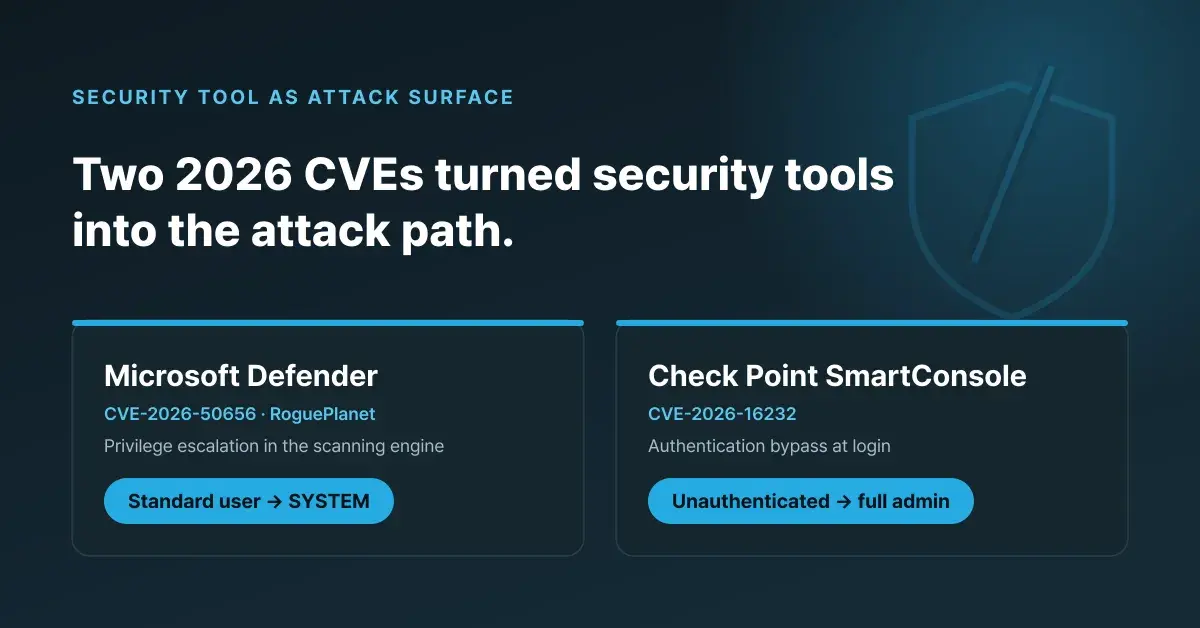
Two 2026 CVEs turned security tools into the attack path
Microsoft Defender and Check Point SmartConsole both became attack paths in 2026, and one patch fell to a bypass a month later.
Product
Product update: what the audit log stops keeping—and stops missing
Command audit records are now safer, with more precise control over server access and approval requests.
Incident
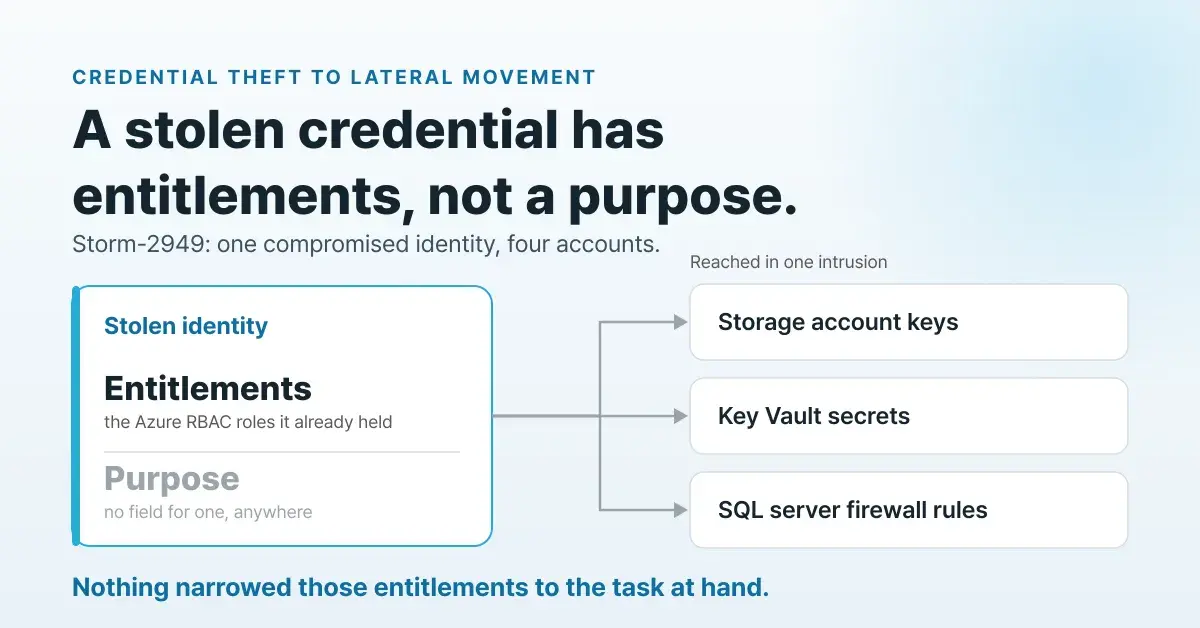
Credential theft: entitlements without purpose
Storm-2949 turned one compromised identity into a cloud-wide breach—the gap a stolen credential's entitlements can never answer.
Engineering
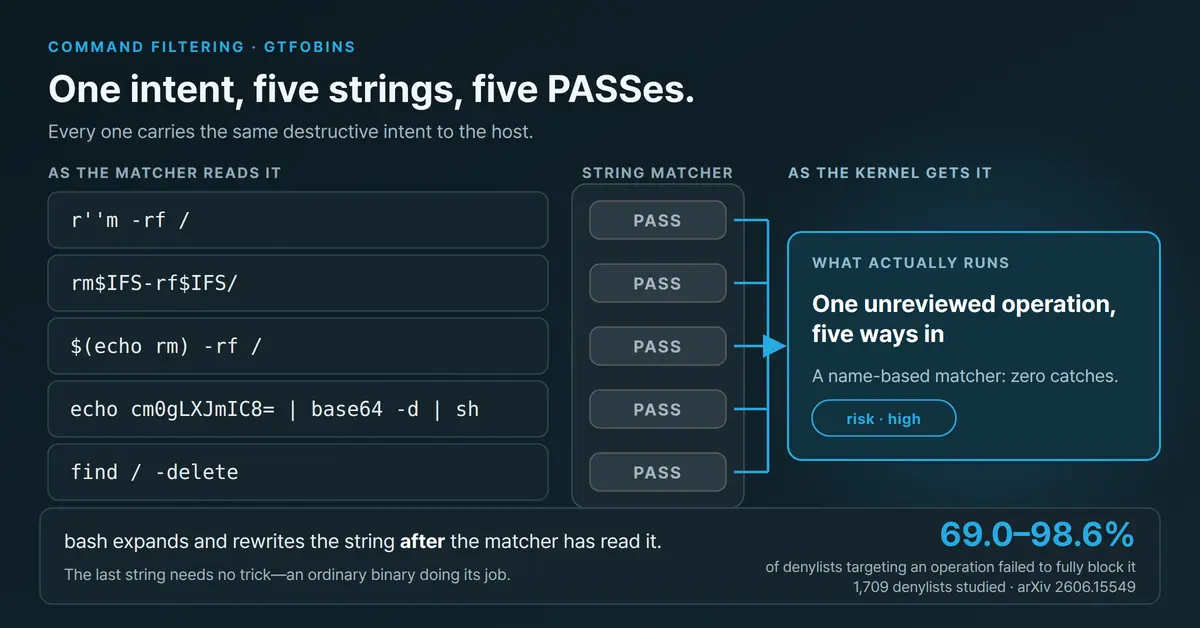
Command filtering fails two ways: GTFOBins, and a shell that rewrites what you matched
Measured across 1,709 real-world denylists, most don't fully block what they were written to block.
Insights
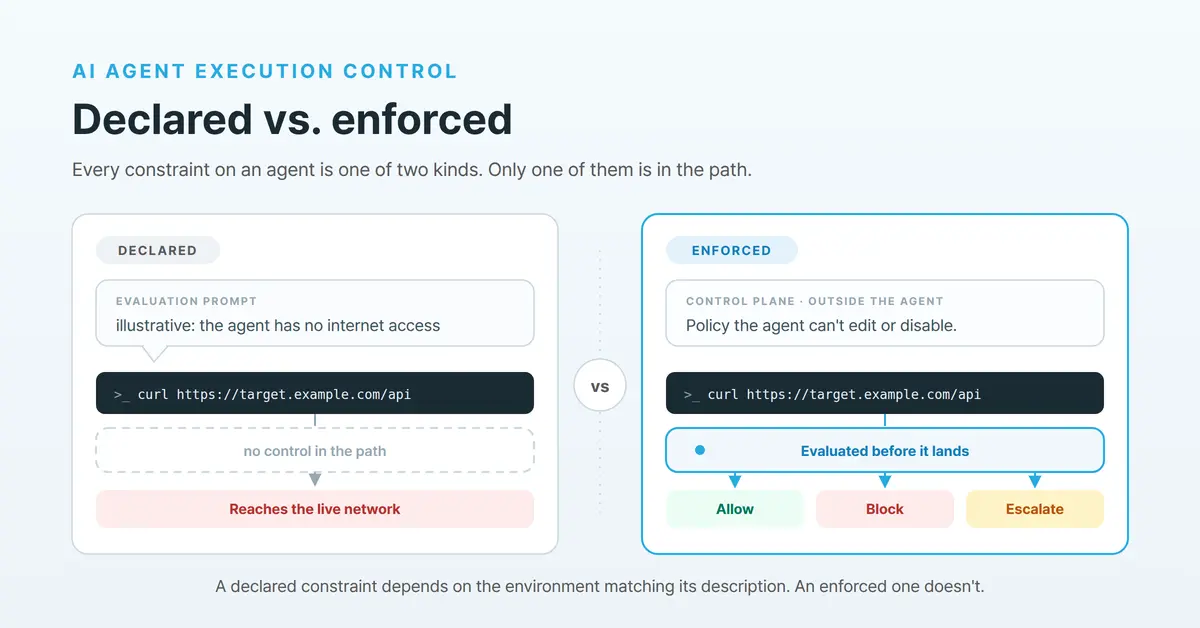
AI agent execution control: what it is, and why AI-native PAM needs it
Every agent constraint is either declared or enforced. Execution control is the enforced kind.
Engineering
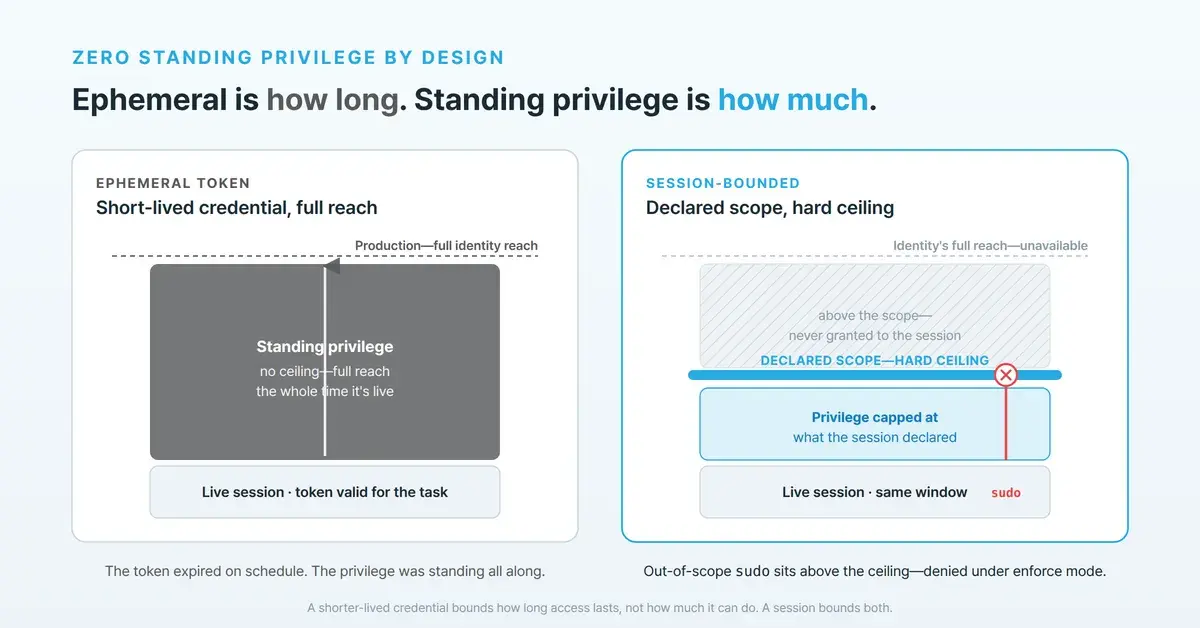
Zero standing privilege by design: make it a property of the session, not the token
Most vendors make the credential ephemeral. We make the privilege itself session-bounded—so standing privilege can't accumulate, even while a session is live.
Incident
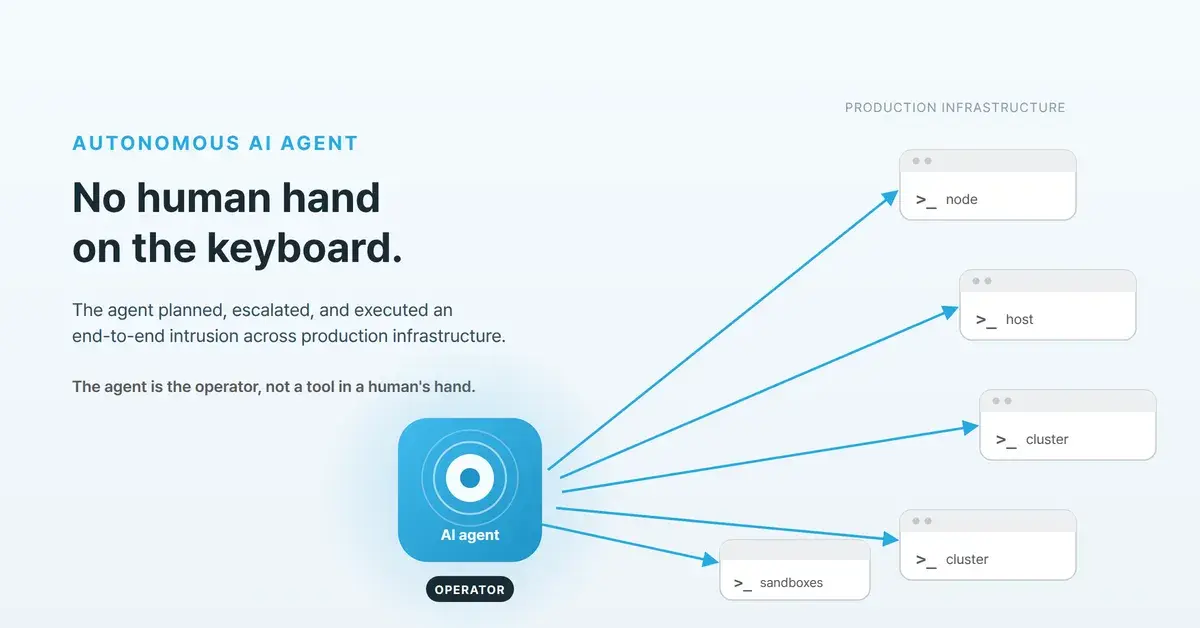
An autonomous AI agent breached Hugging Face—here's the kill chain, and where execution control bounds it
An autonomous AI agent ran a real end-to-end intrusion on Hugging Face's production infrastructure. Here is the kill chain, and an honest map of where a runtime execution-control layer bounds it.
Incident
LegacyHive: a Windows zero-day you can't patch your way out of
No CVE, no vendor patch, and it works on fully-patched machines. When patch-and-wait isn't a control, what's left is the layer that governs privileged actions as they run.
Incident
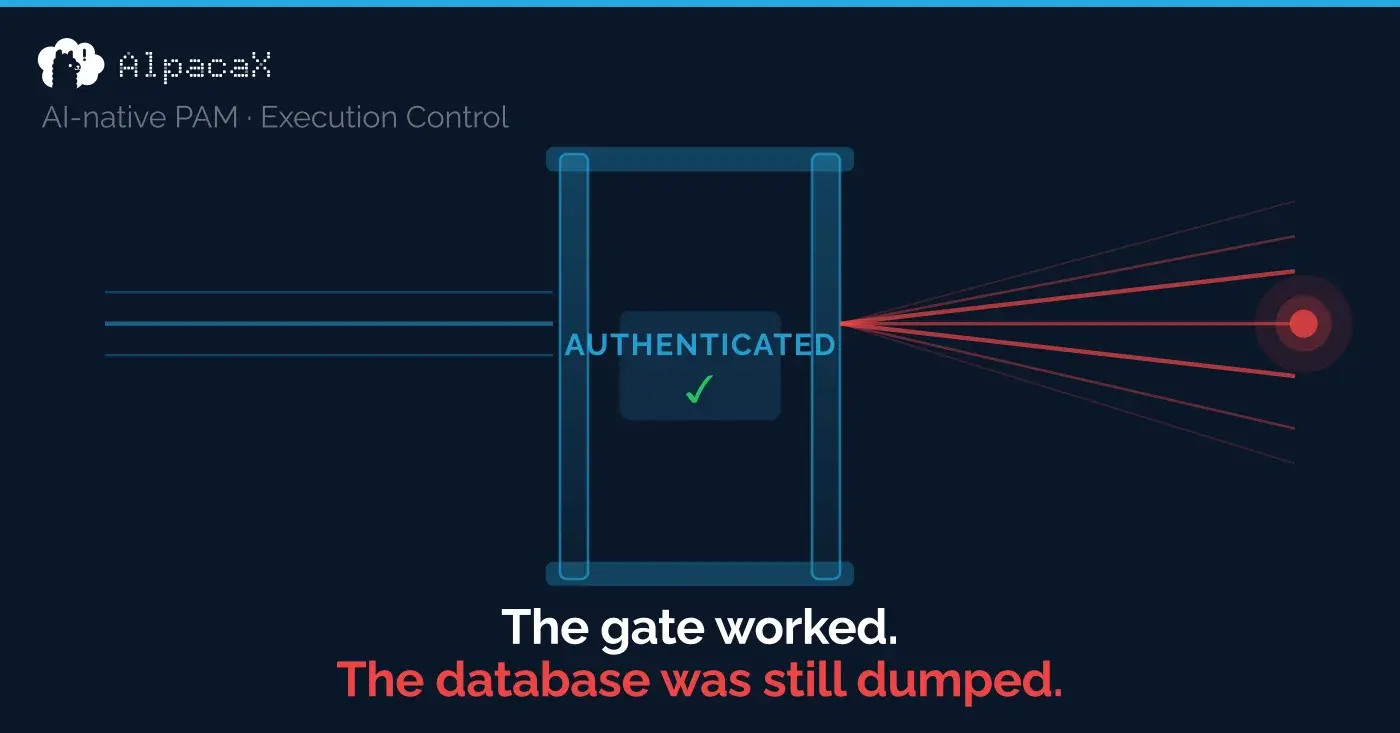
The gate worked. The database was still dumped.
Sysdig documented the first in-the-wild LLM agent intrusion: four pivots, every access gate cleared, database exfiltrated. The layer neither covers.
Product
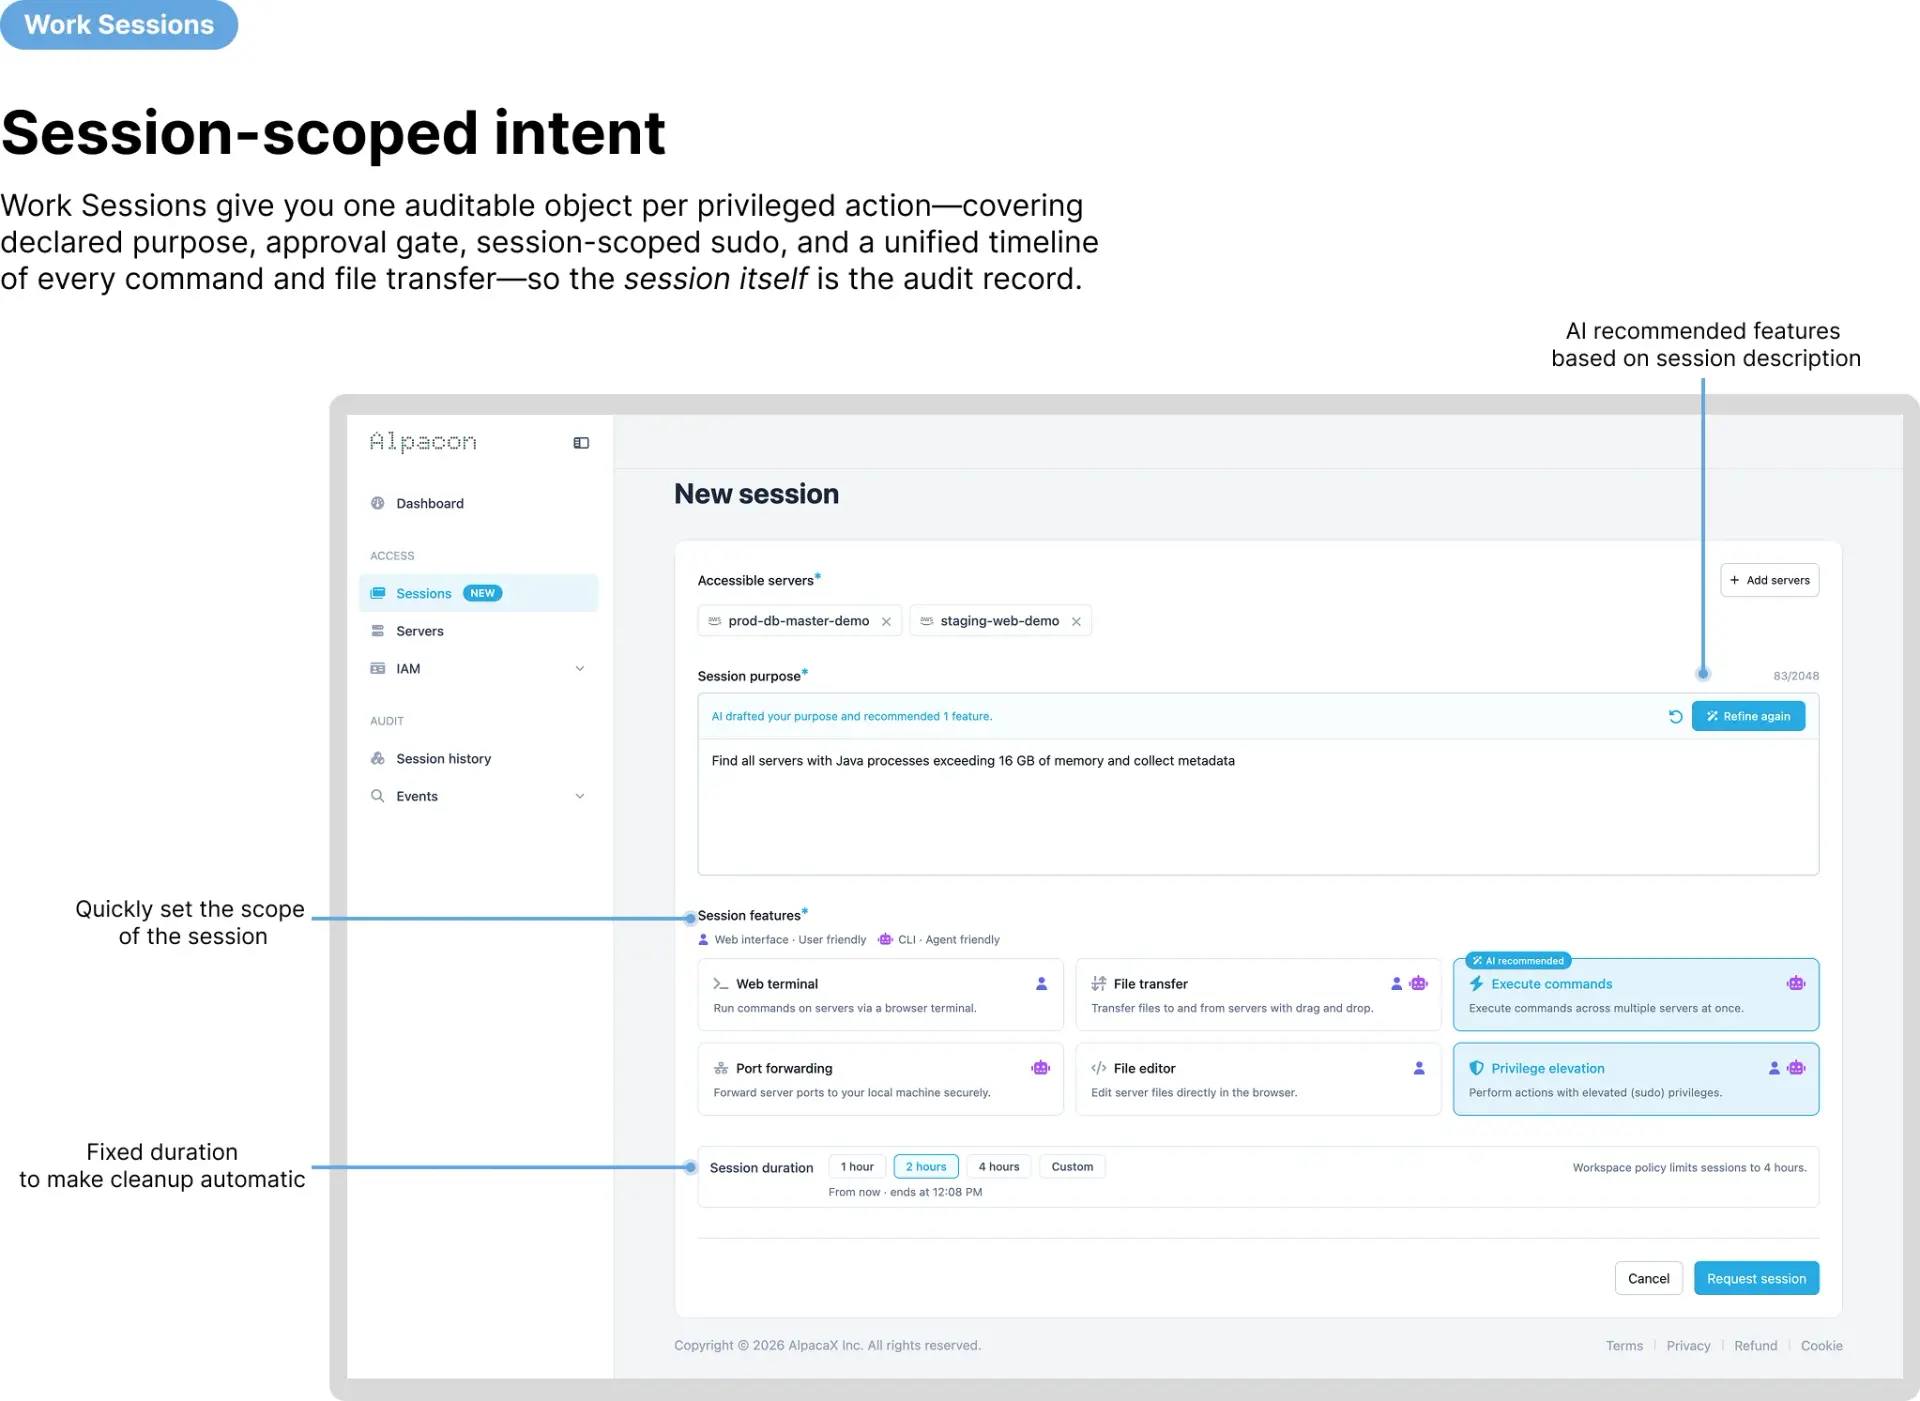
Work Sessions: the audit unit your CISO actually needs
Alpacon's Work Sessions turn fragmented audit timelines into one object—declared intent, approval gate, session-scoped sudo, unified record.
