Year
- 2026
Category
- Incident
- Insights
- Product
- Testimonial
- Engineering
Tag| Work Sessions
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
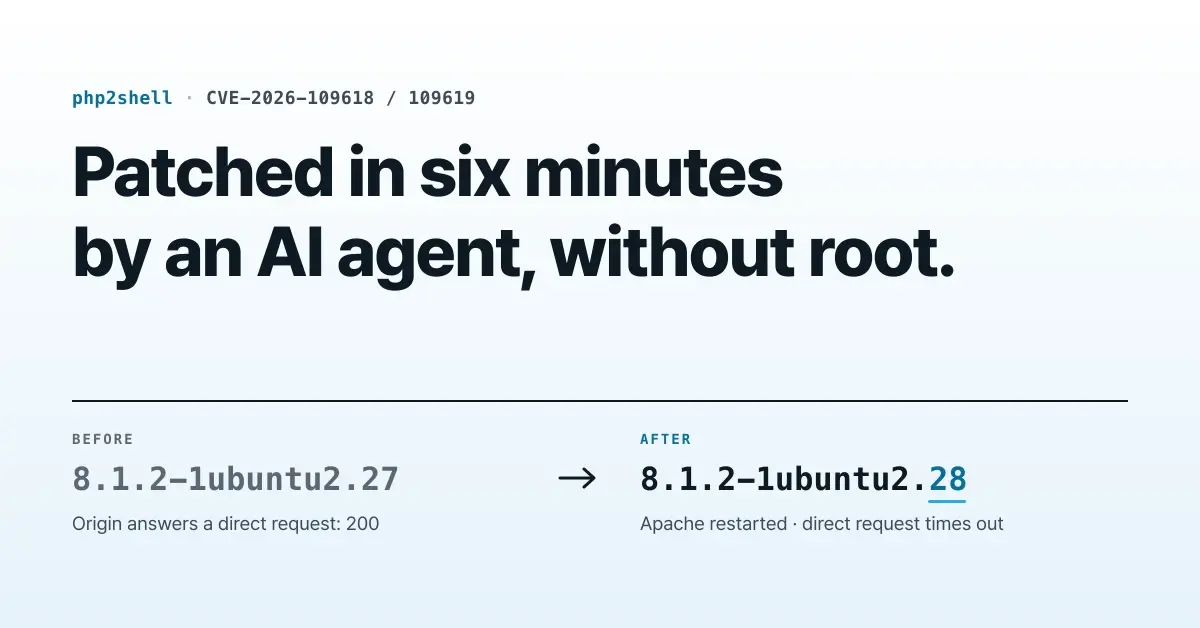
Incident
How we patched php2shell in six minutes with an AI agent
What our agent ran, why each privileged command was allowed, and the fixed builds, restart checks and origin lockdown to do it yourself.

Product
Product update: how a request arrived, and what reaches you
Approval cards show how a request arrived and whether it was verified, alerts can be muted per server, and extending a session takes a reason.

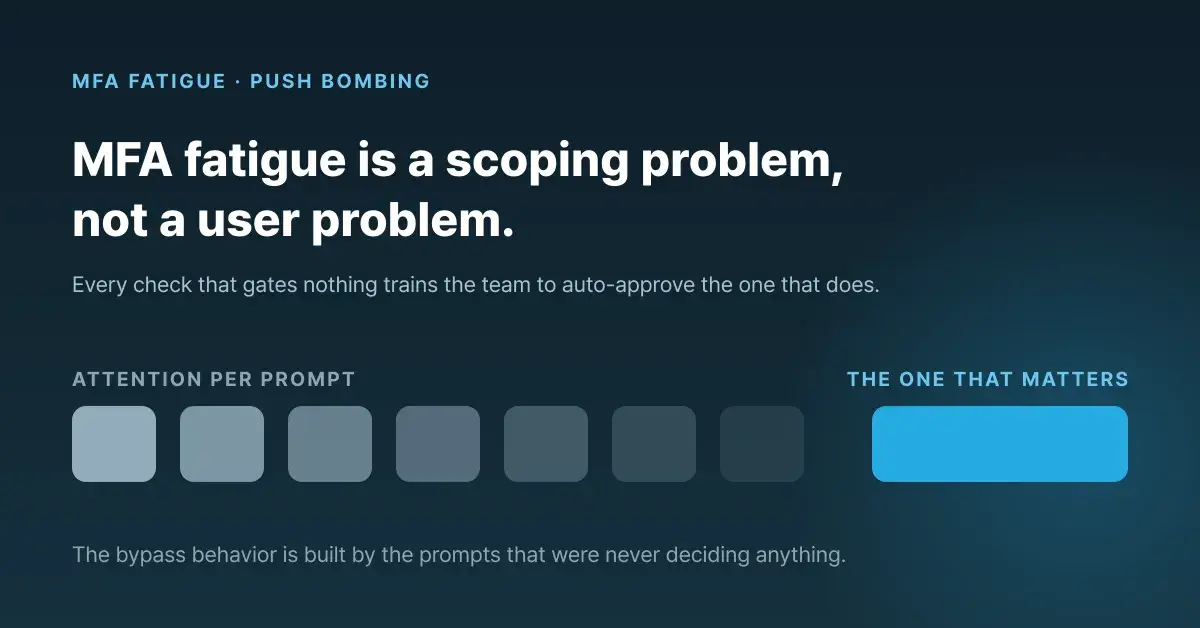
Insights
MFA fatigue is a scoping problem, not a user problem
Prompt-bombing wins when every extra MFA check trains the team to auto-approve the one that matters.

Insights
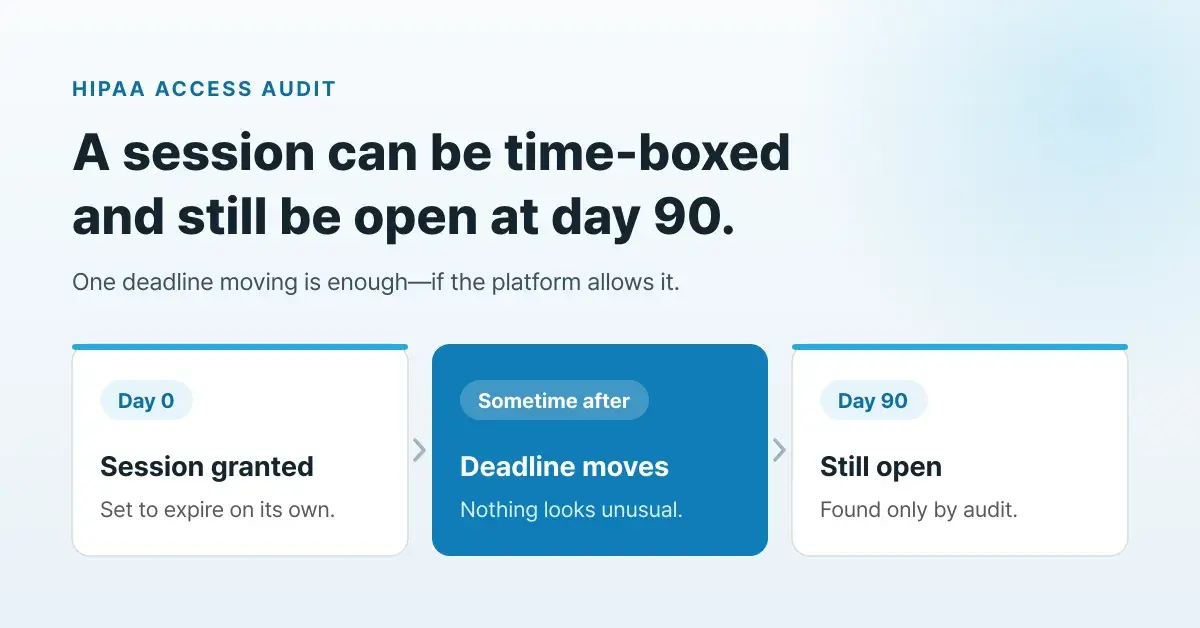
HIPAA day-90 audit: what session expiry misses
A HIPAA day-90 audit should review grant history, not just a session's current expiry. Here is what to pull.
Engineering
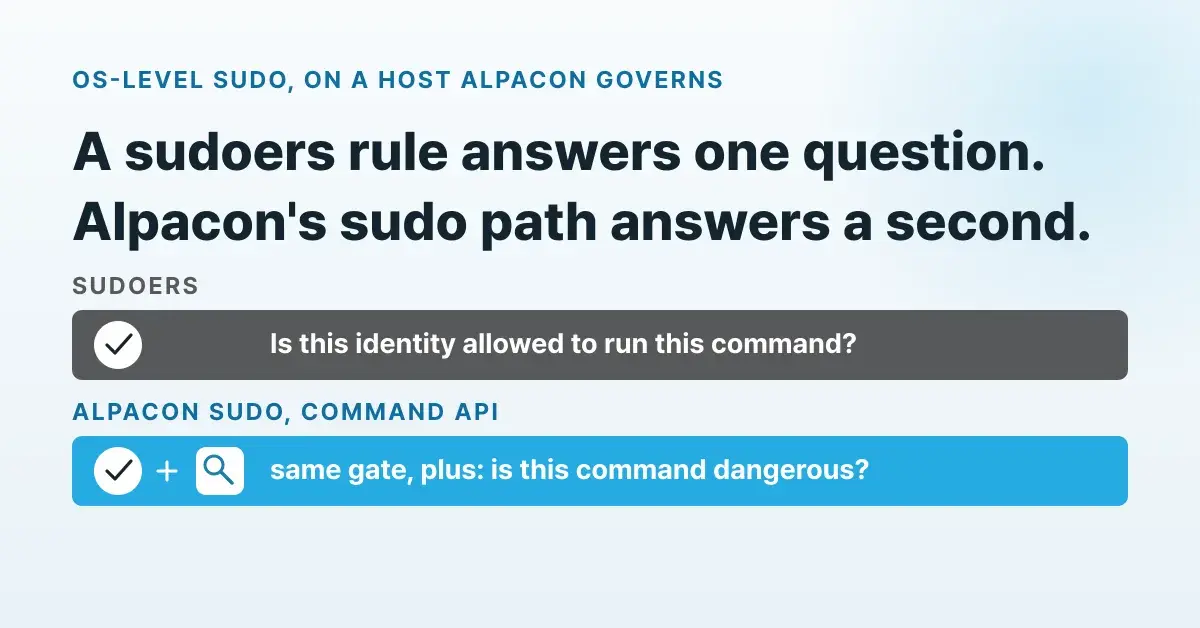
Session-scoped sudo: bind OS-level root to a session, not a sudoers file
A sudoers rule only asks who's allowed to run a command. Sudo reaching Alpacon's command API asks a second question: is this command dangerous.

Incident
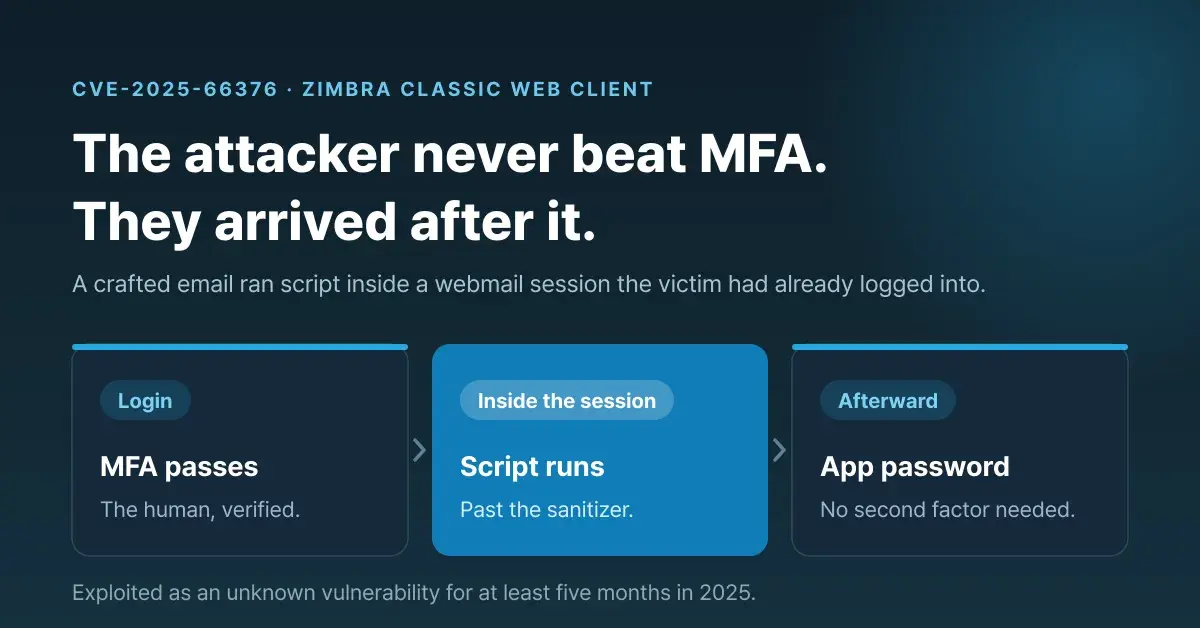
SSO and MFA verify the login, not what the session does next
A five-month Zimbra zero-day shows what happens after an attacker gets inside an authenticated session.
Incident
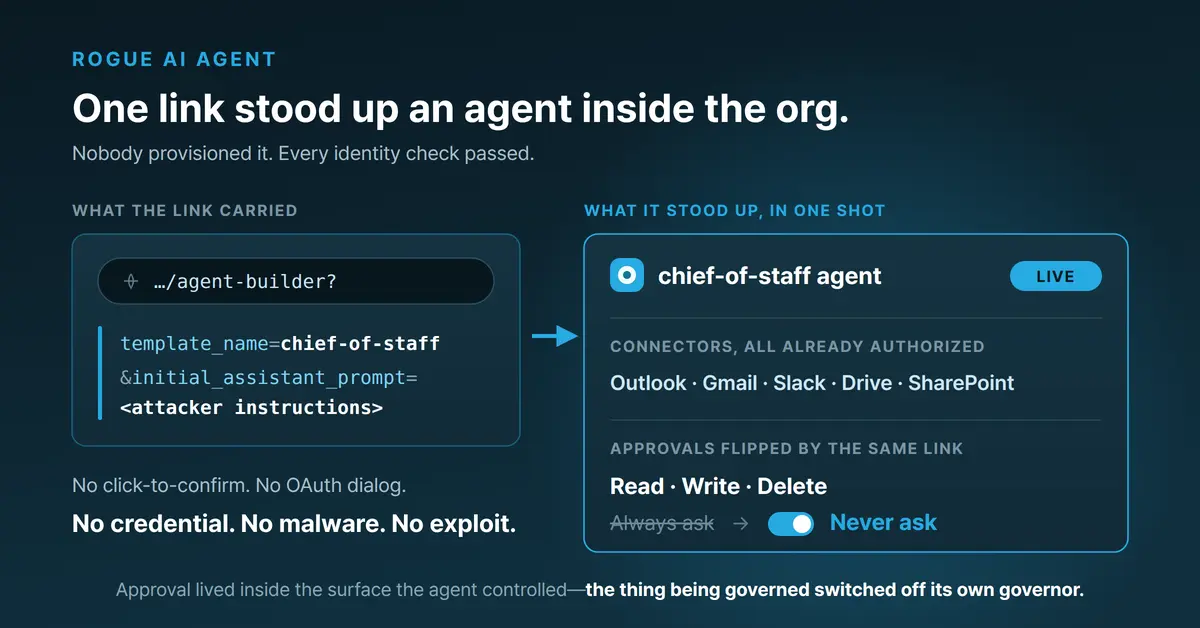
AgentForger: how one link forged a rogue AI agent with a borrowed employee session
One crafted URL stood up an attacker-controlled AI agent inside the org. No stolen credential, no malware.
Engineering
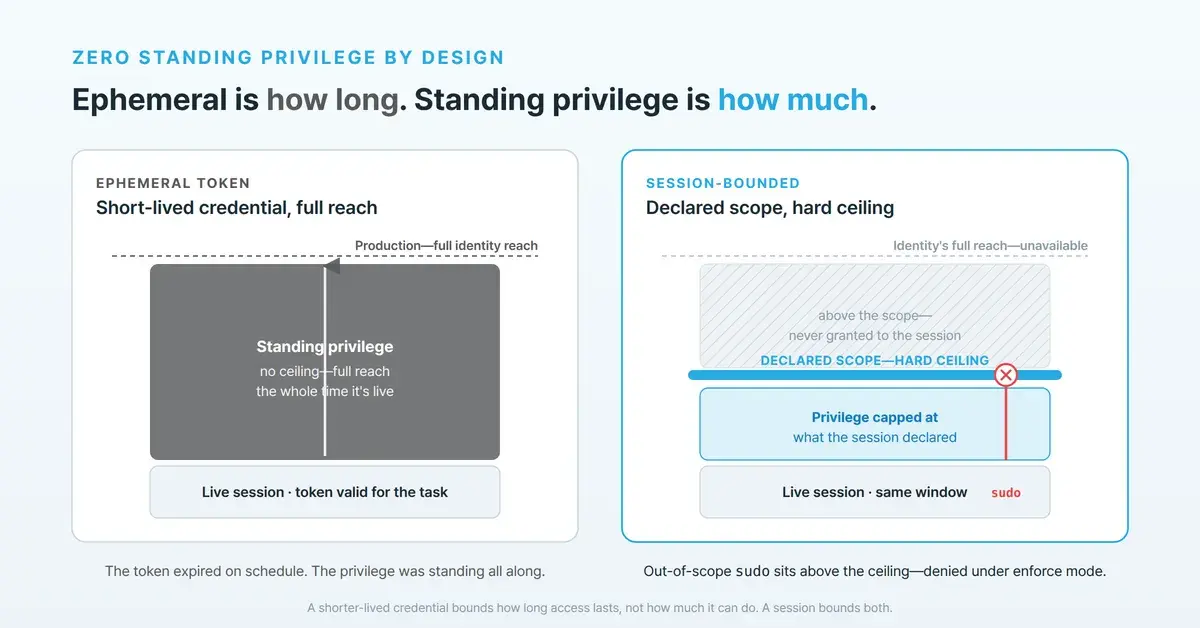
Zero standing privilege by design: make it a property of the session, not the token
Most vendors make the credential ephemeral. We make the privilege itself session-bounded—so standing privilege can't accumulate, even while a session is live.
Insights
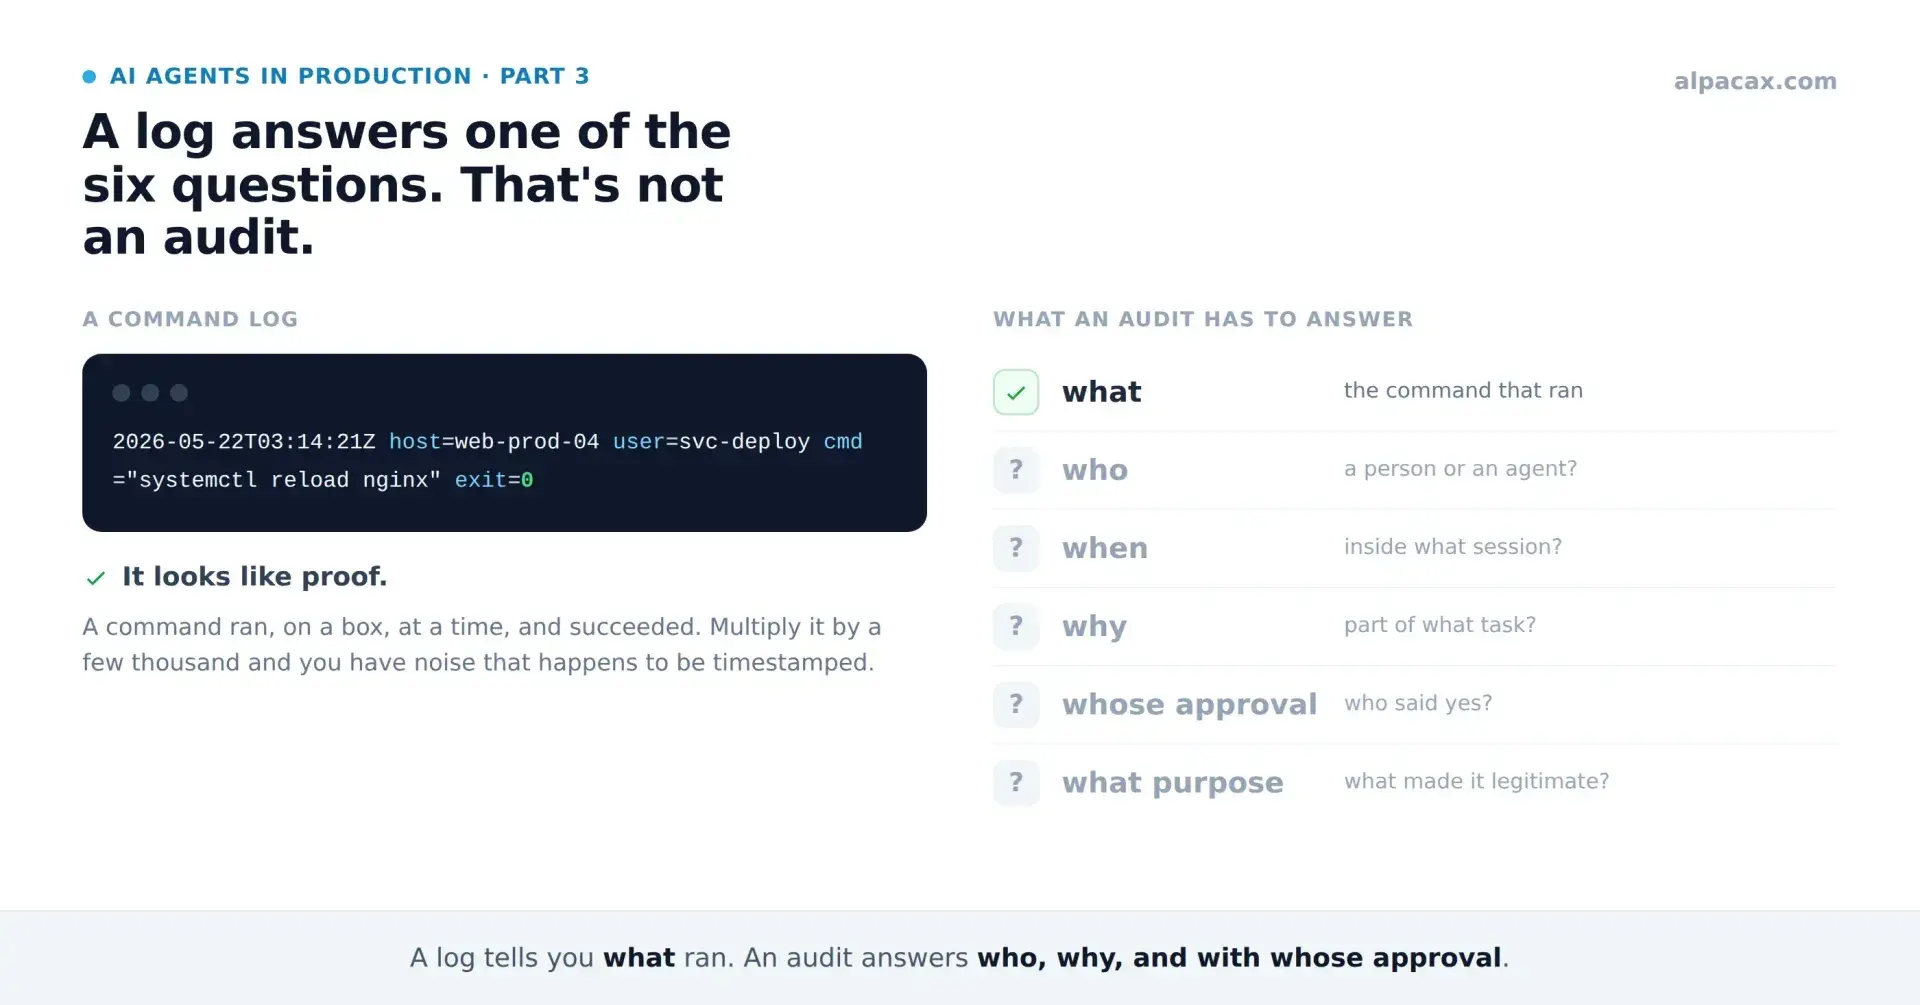
A command log won't tell you what your agent actually did.
A command log tells you what ran. An audit has to answer who, why, and with whose approval—for humans and agents alike.
Product
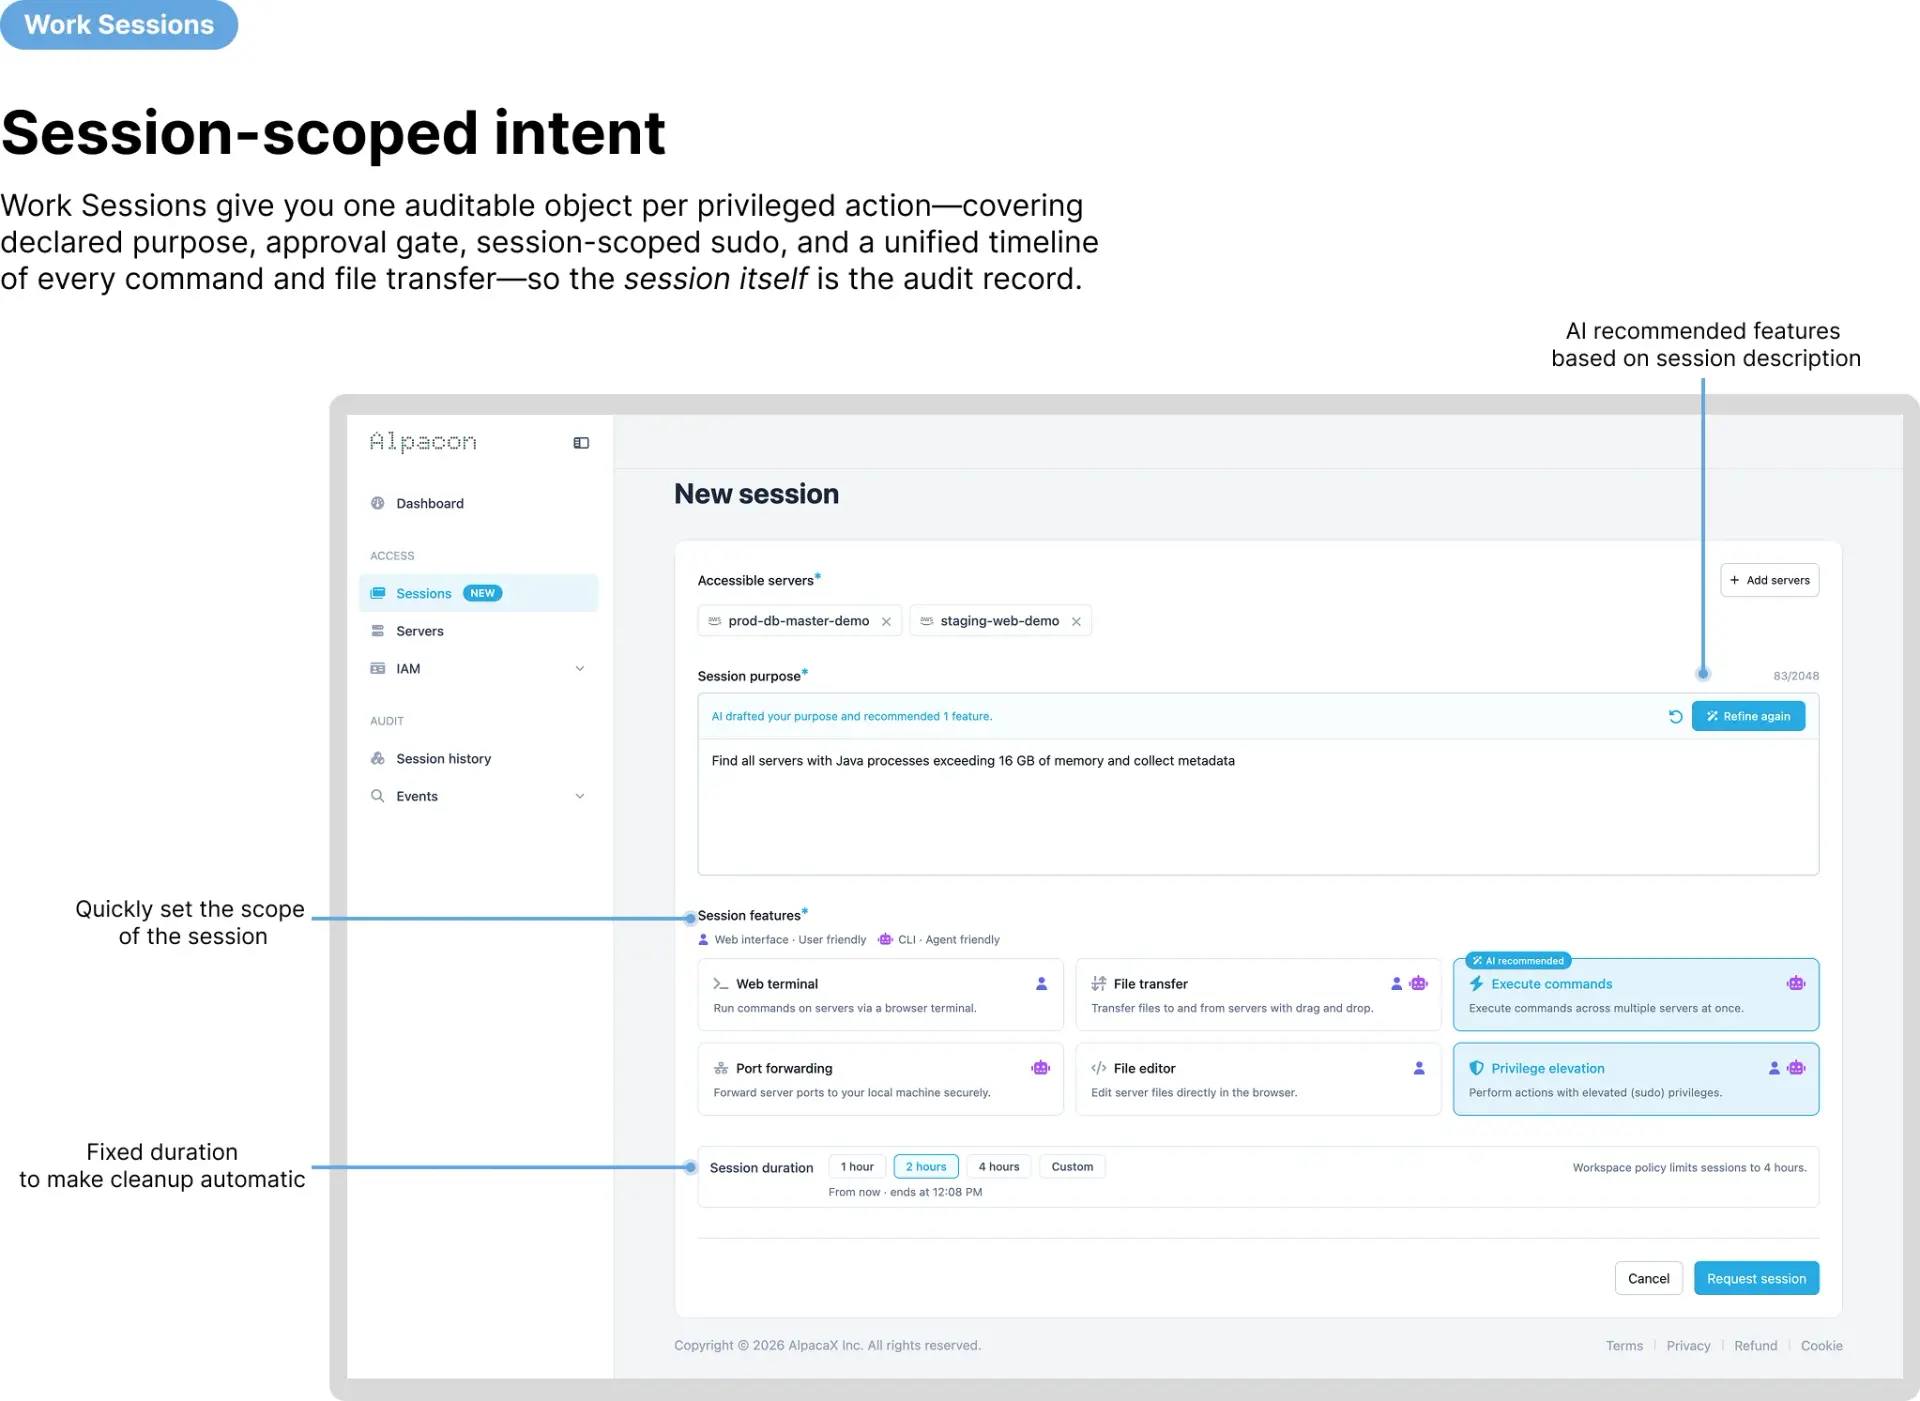
Work Sessions: the audit unit your CISO actually needs
Alpacon's Work Sessions turn fragmented audit timelines into one object—declared intent, approval gate, session-scoped sudo, unified record.
