Year
- 2026
Category
- Insights
- Incident
- Product
- Engineering
Tag| Zero standing privilege
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
Insights
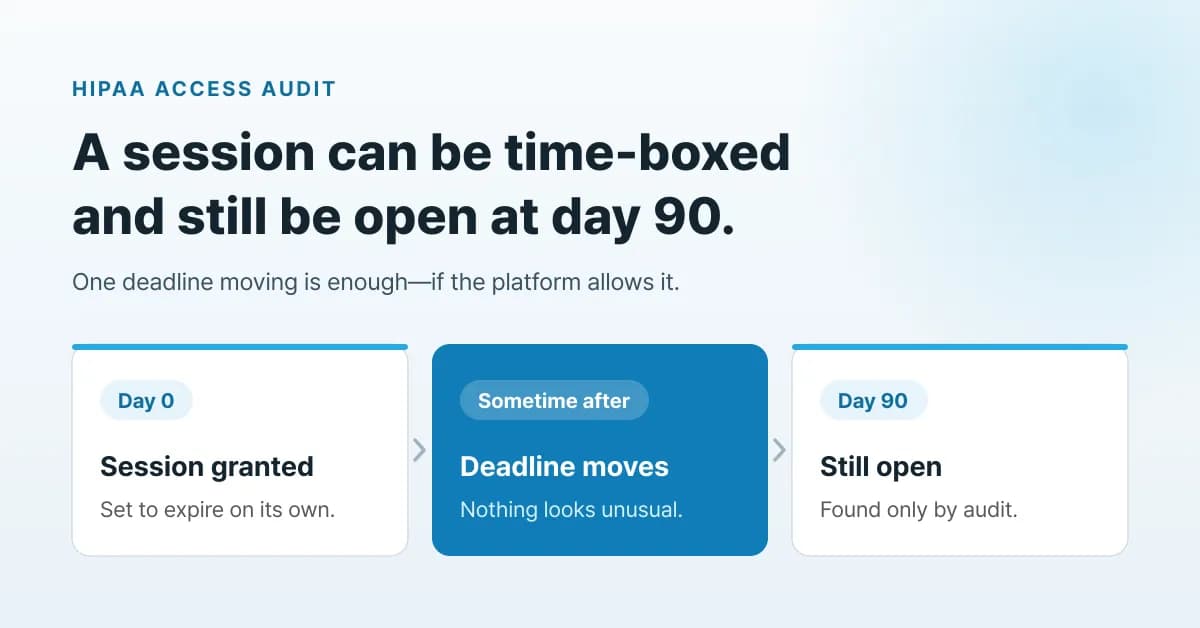
HIPAA day-90 audit: what session expiry misses
A HIPAA day-90 audit should review grant history, not just a session's current expiry. Here is what to pull.

Marco KwakHead of GTM · August 27, 2026
Engineering
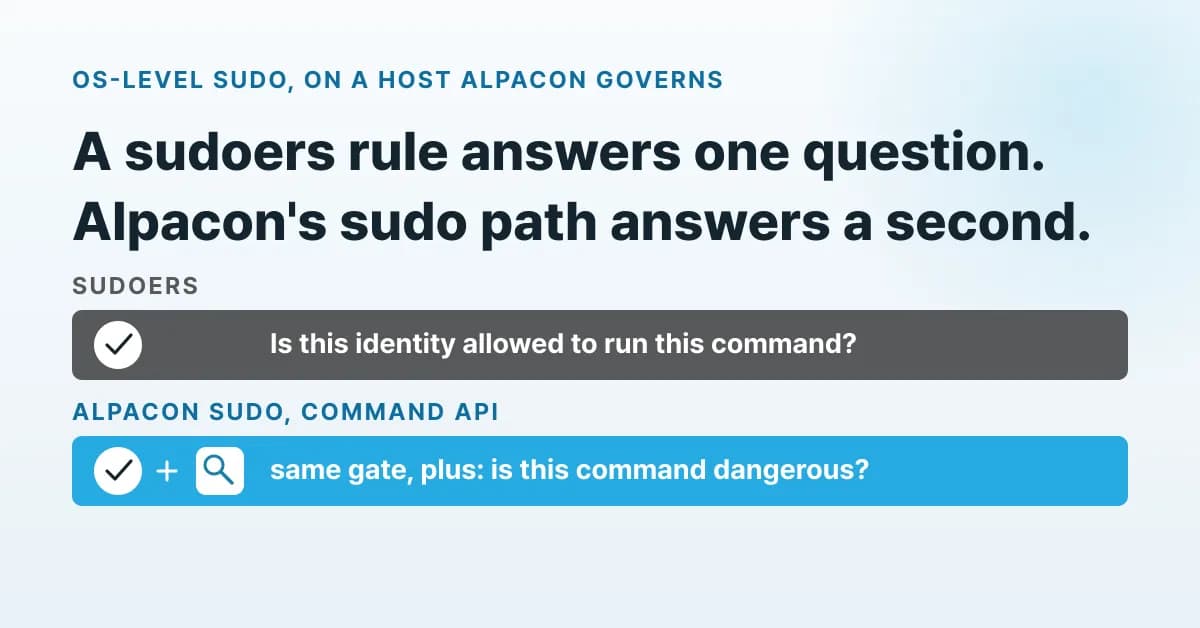
Session-scoped sudo: bind OS-level root to a session, not a sudoers file
A sudoers rule only asks who's allowed to run a command. Sudo reaching Alpacon's command API asks a second question: is this command dangerous.

Jungyeon LeeContent Marketer · August 26, 2026
Engineering
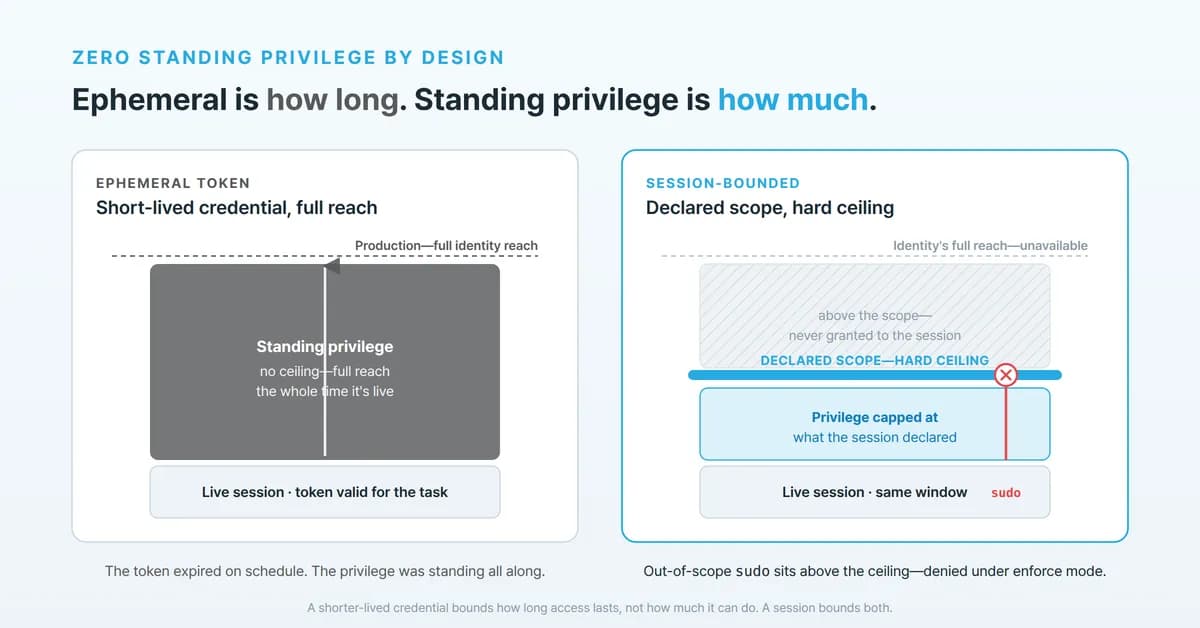
Zero standing privilege by design: make it a property of the session, not the token
Most vendors make the credential ephemeral. We make the privilege itself session-bounded—so standing privilege can't accumulate, even while a session is live.

Eunyoung JeongFounder & CEO · August 13, 2026
Insights
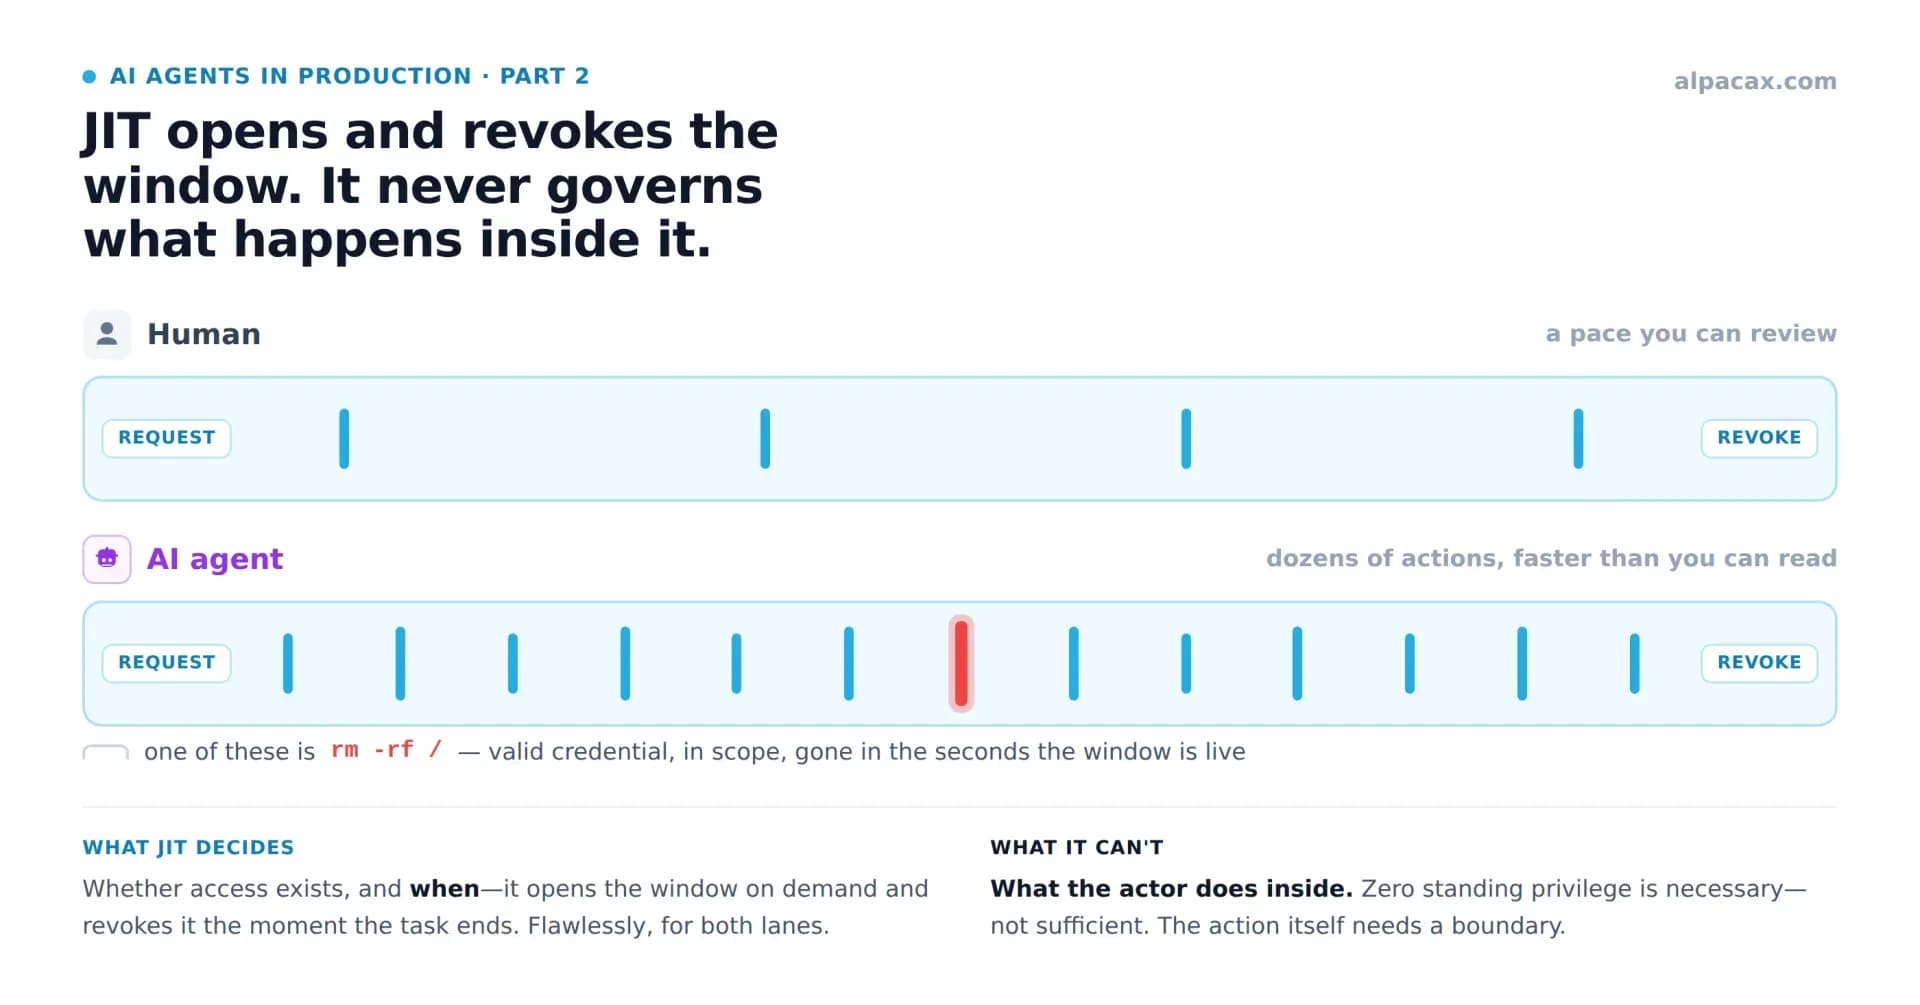
JIT access control is for humans. What should we have for AI agents?
Just-in-time access governs whether an agent gets in, and when. It says nothing about what the agent does once inside.
Eunyoung JeongFounder & CEO · July 14, 2026
Insights
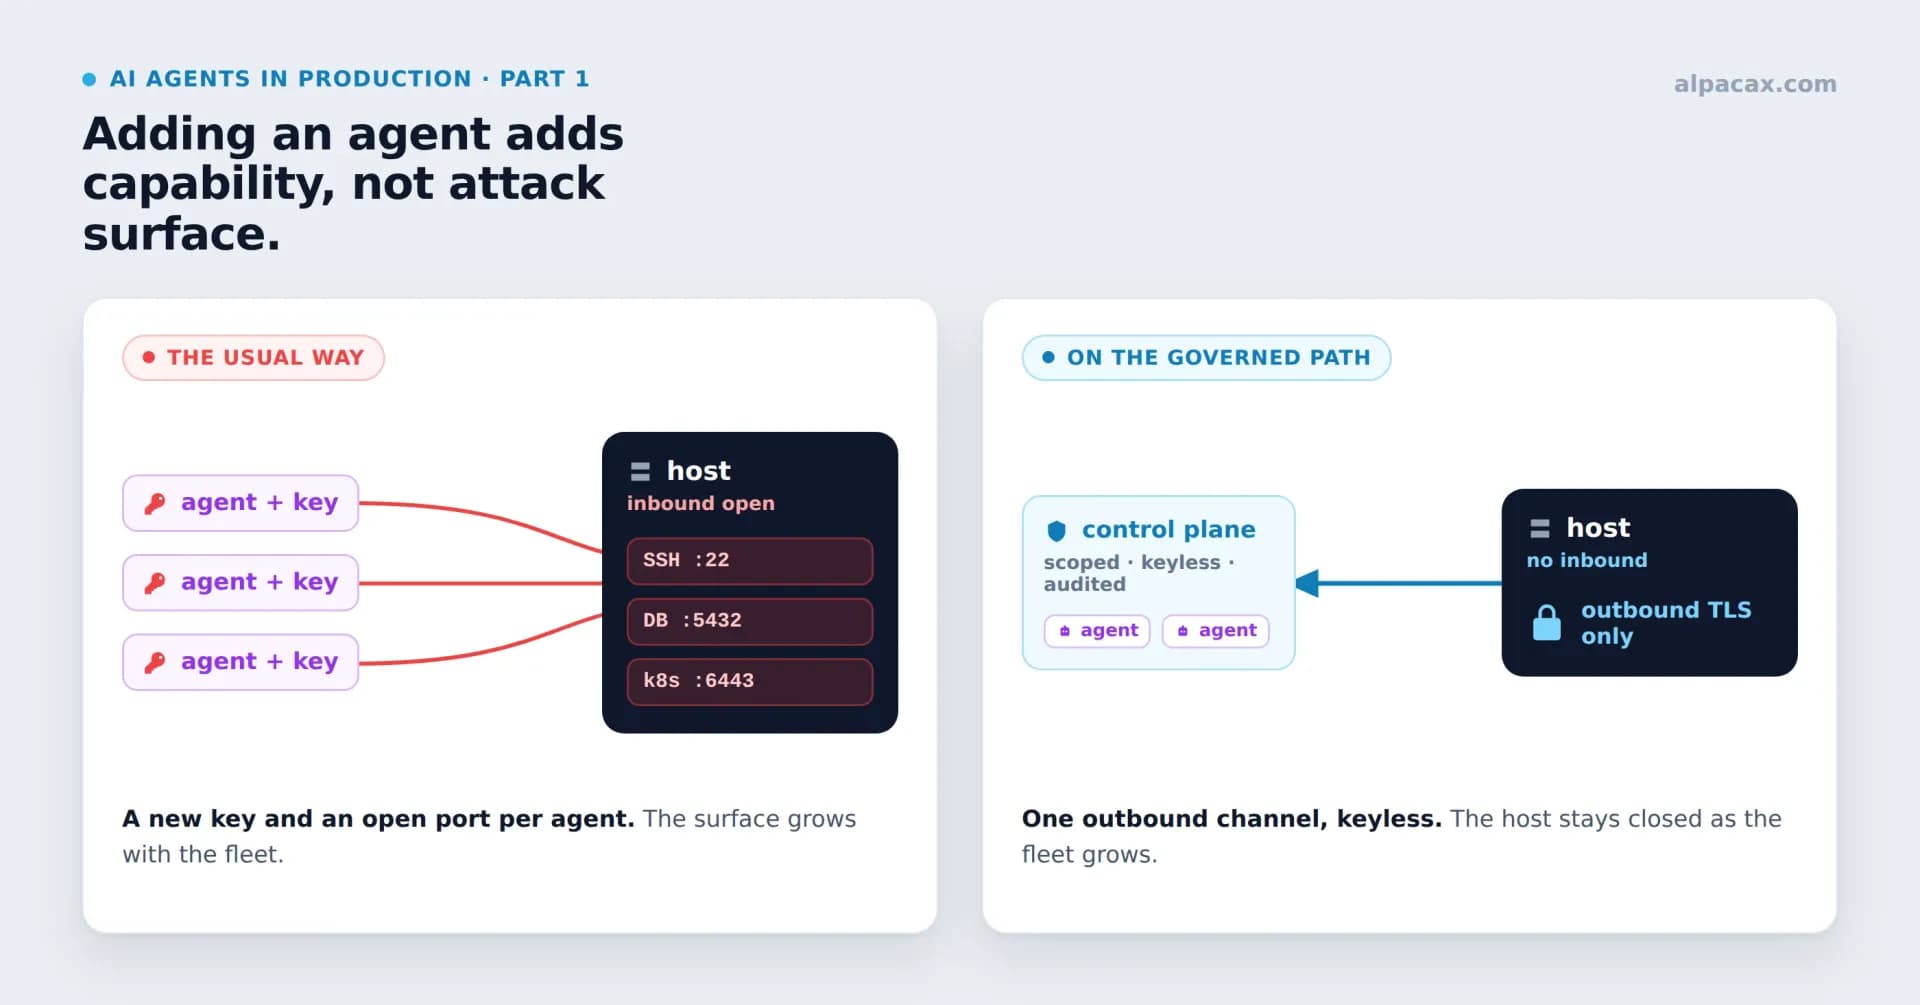
Adding AI agents shouldn't mean adding more security exposure
Expanding your attack surface isn't the price of an AI agent. It's an artifact of how you wire it in—and it's avoidable.
Eunyoung JeongFounder & CEO · July 9, 2026