Year
- 2026
Category
- Product
- Insights
- Incident
- Testimonial
- Engineering
Tag
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
Product
Product update: what your AI agents did, and why their commands were stopped
See what your AI agents did this month and how often their commands were refused, all on one dashboard. People and agents both learn why a command was stopped.

Insights
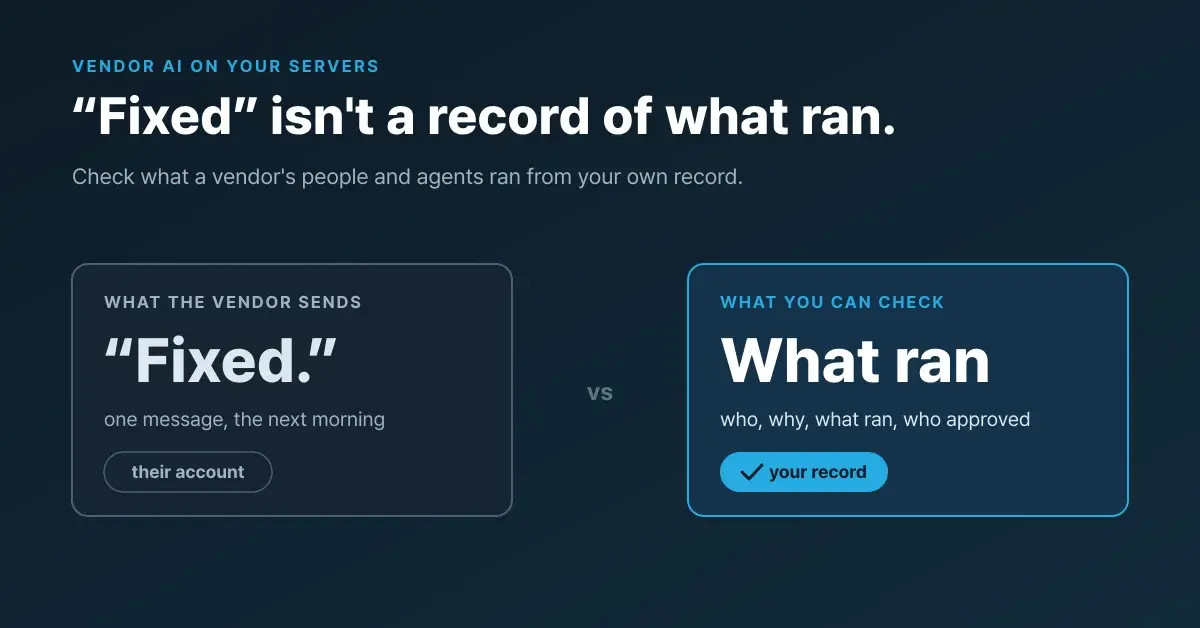
What are your vendors' AI agents running on your servers?
Their agents can connect with the keys you gave the vendor. Check what ran from your own record, not the vendor's word.
Insights
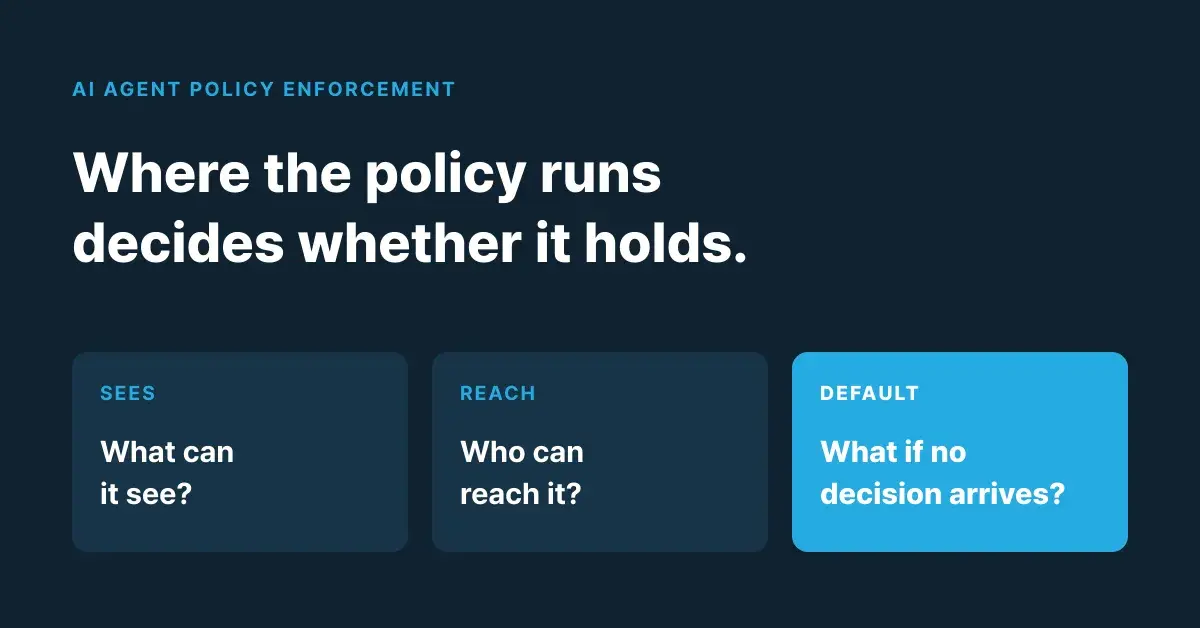
AI agent policy enforcement: where the policy actually runs
What the enforcement point sees, who can reach it, and what it does when the decision doesn't arrive.

Product
Your first Work Session: purpose, approval, and the record
Four fields and approval where your workspace requires it: how a new Alpacon workspace starts governed work.
Insights
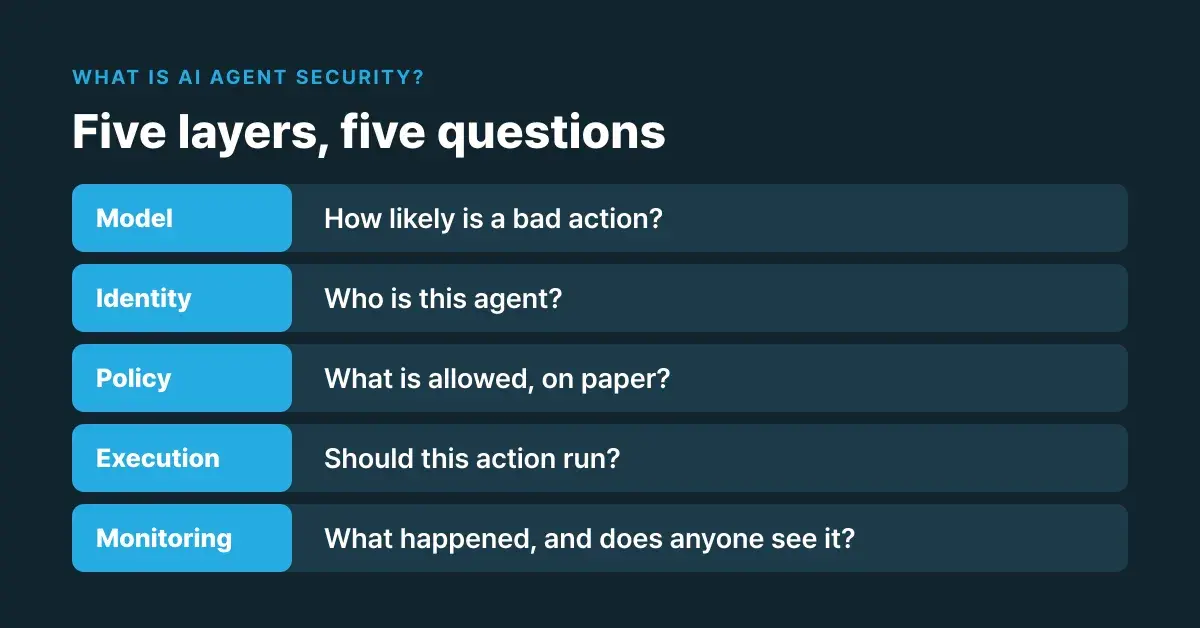
What is AI agent security? Five layers, five questions
Model, identity, policy, execution, monitoring: one question each, and none answers another's.

Insights
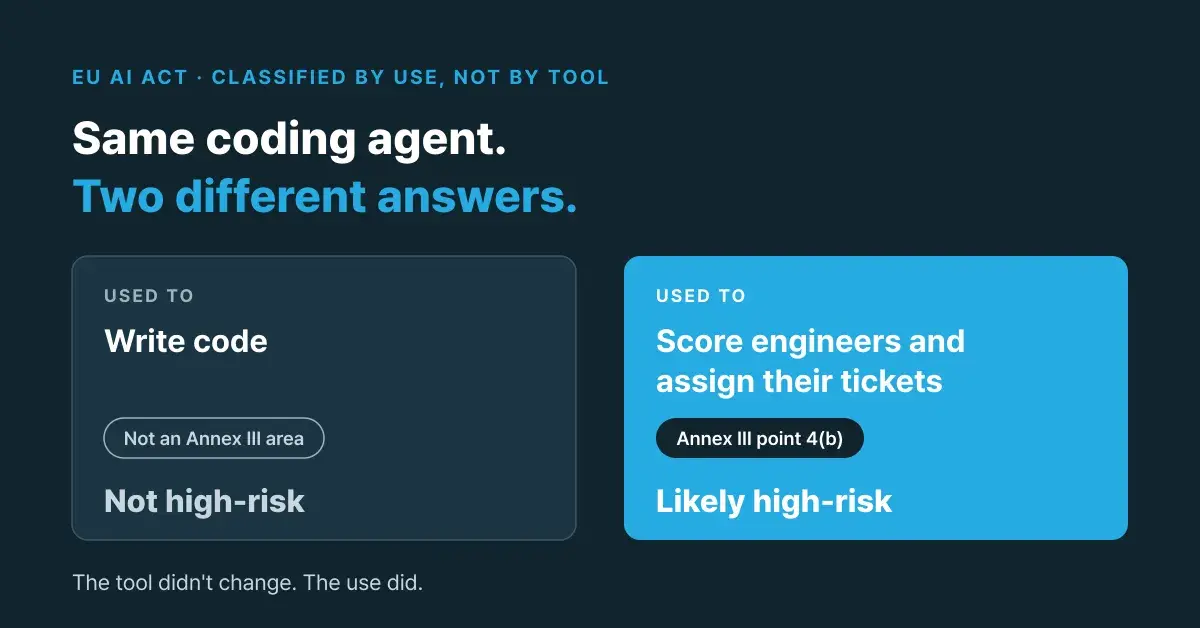
Does Claude Code or Cursor make you an EU AI Act provider?
Writing code with an AI agent is not an Annex III use. Ranking engineers with one likely is.

Product
Product update: intuitive access rules, logins worth a look
Set access rules by completing a sentence and test them first, see which rule decided a request, and review only the direct logins that need a look.
Insights
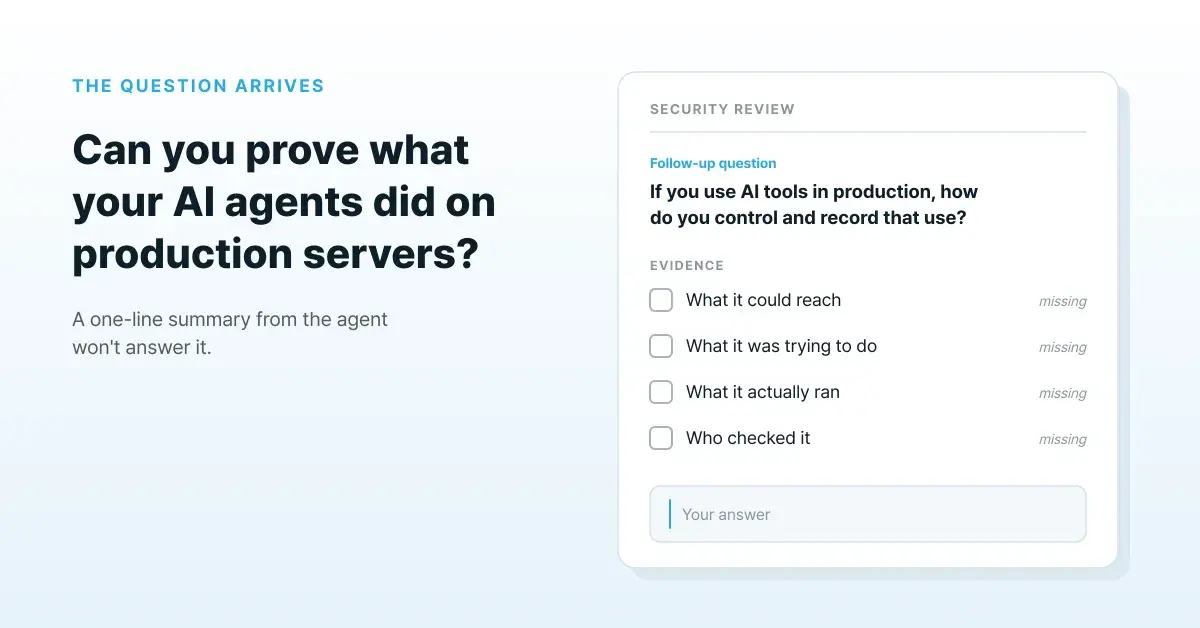
Can you prove what your AI agents did on production servers?
What it could reach, what it was trying to do, what it actually ran, and who checked it. Each needs a record.
Incident
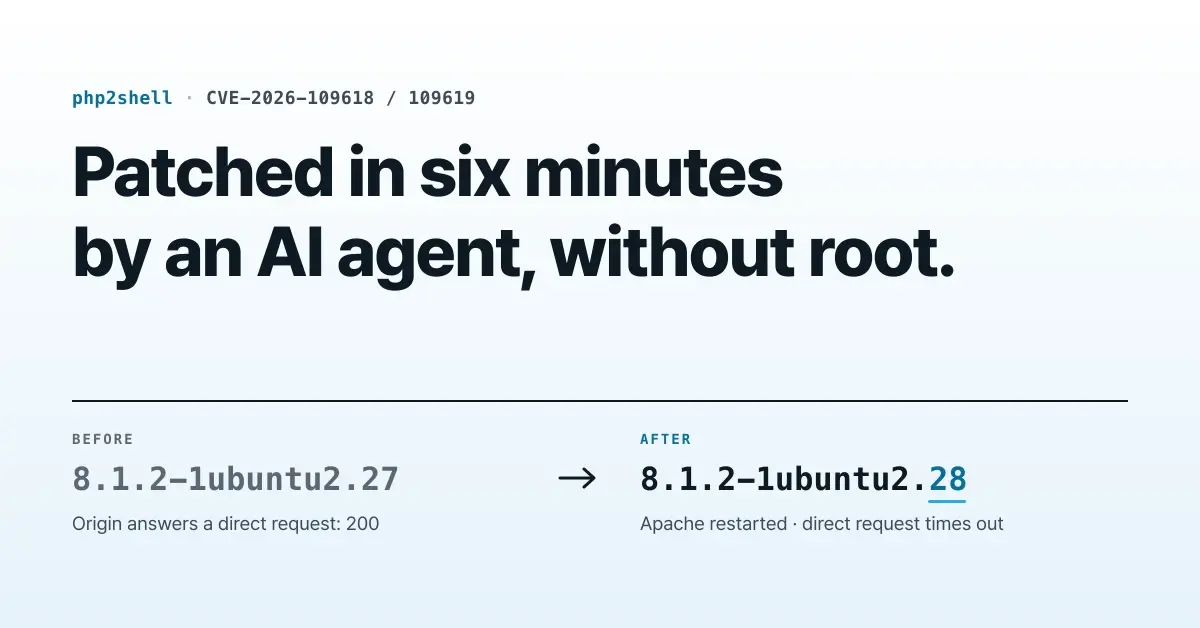
How we patched php2shell in six minutes with an AI agent
What our agent ran, why each privileged command was allowed, and the fixed builds, restart checks and origin lockdown to do it yourself.
Insights
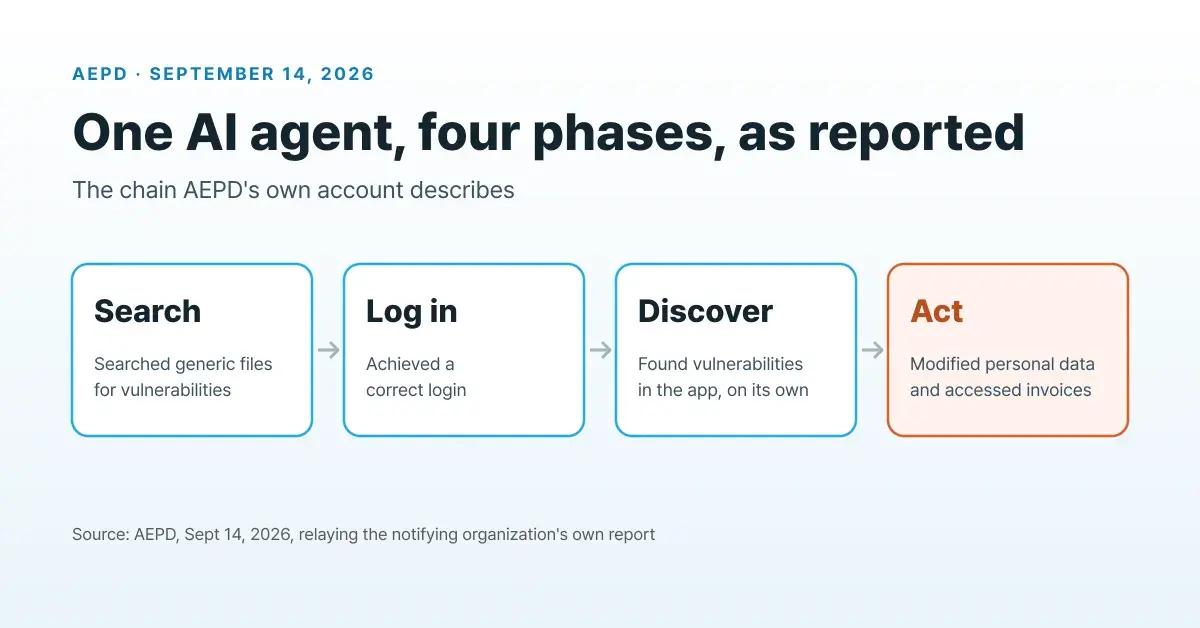
What Spain's AEPD actually published about an AI agent breach
AEPD's own account: four phases, chained together, with key details left out.
Insights
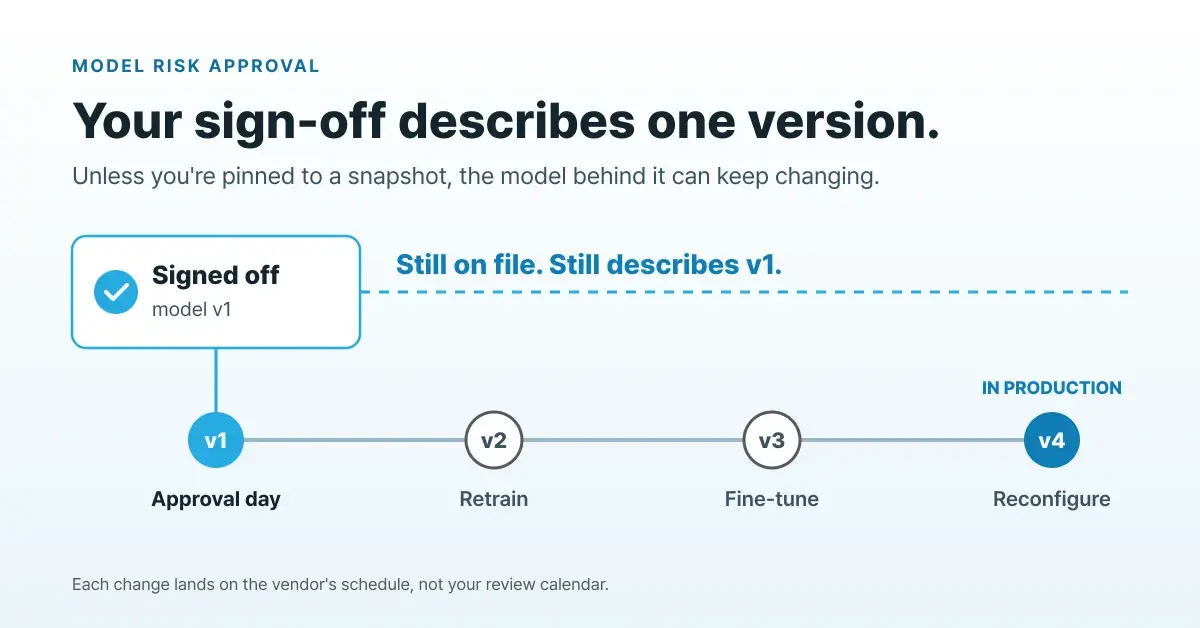
The model you approved isn't the model running today
Unless you're pinned to a fixed snapshot, a vendor retrain can land on their schedule, after your sign-off.
Insights
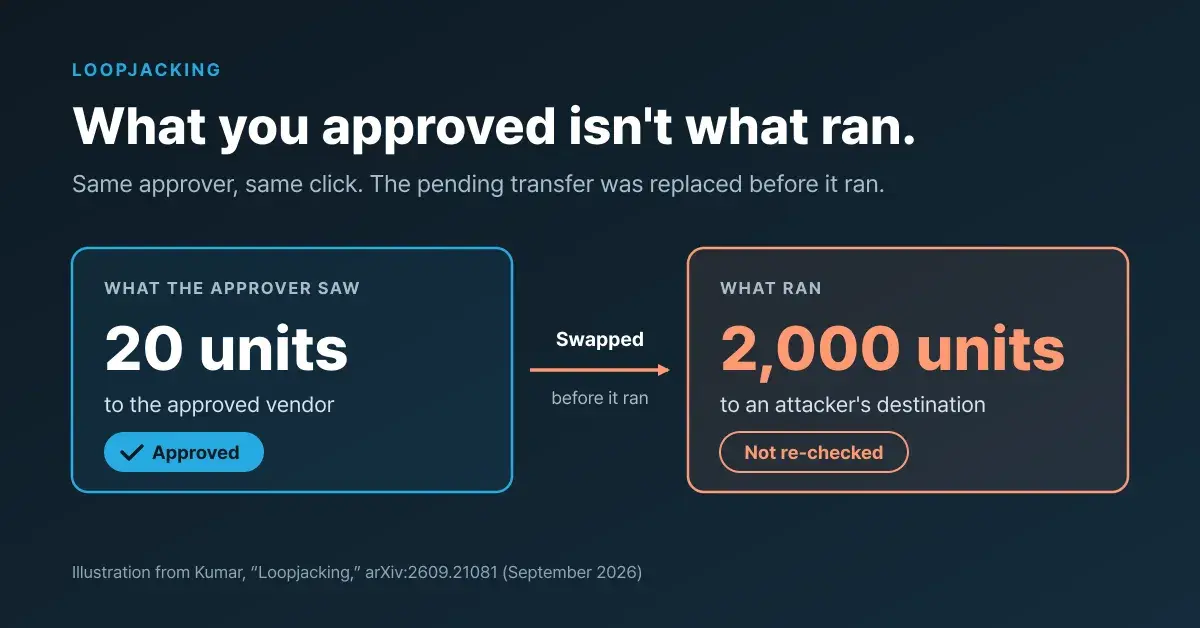
Loopjacking: what you approved isn't what ran
A researcher reproduced the bypass in tested setups across three released agent frameworks.
Product
Product update: how a request arrived, and what reaches you
Approval cards show how a request arrived and whether it was verified, alerts can be muted per server, and extending a session takes a reason.
Insights
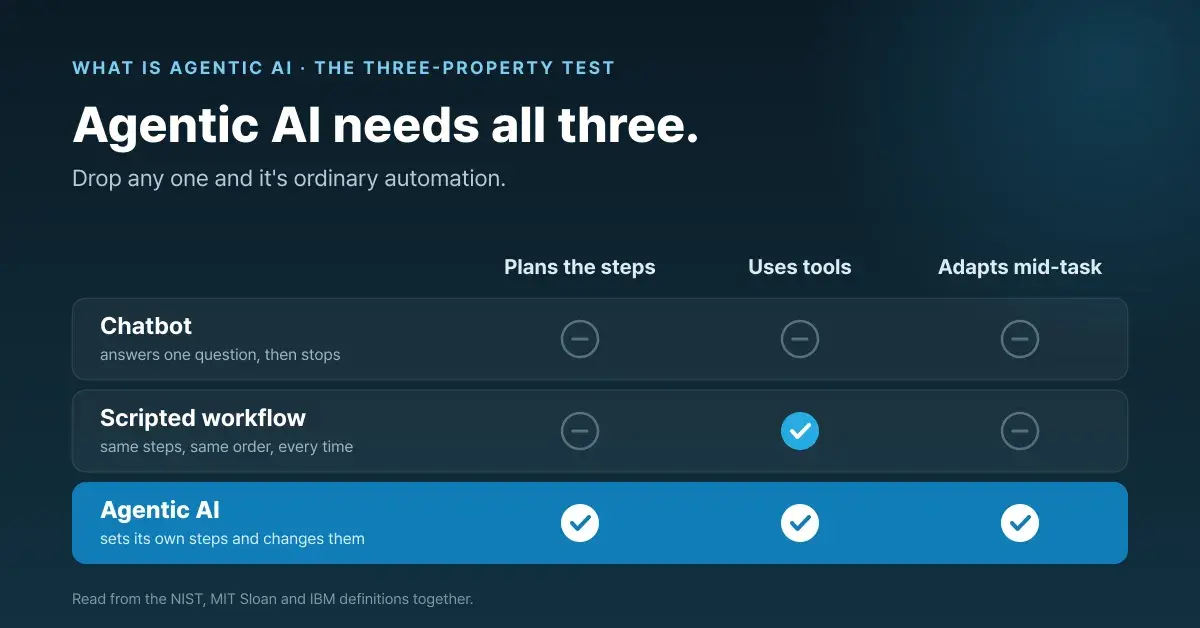
What is agentic AI? The definition that actually holds up
The three properties that define agentic AI are why the label keeps getting abused.
Incident
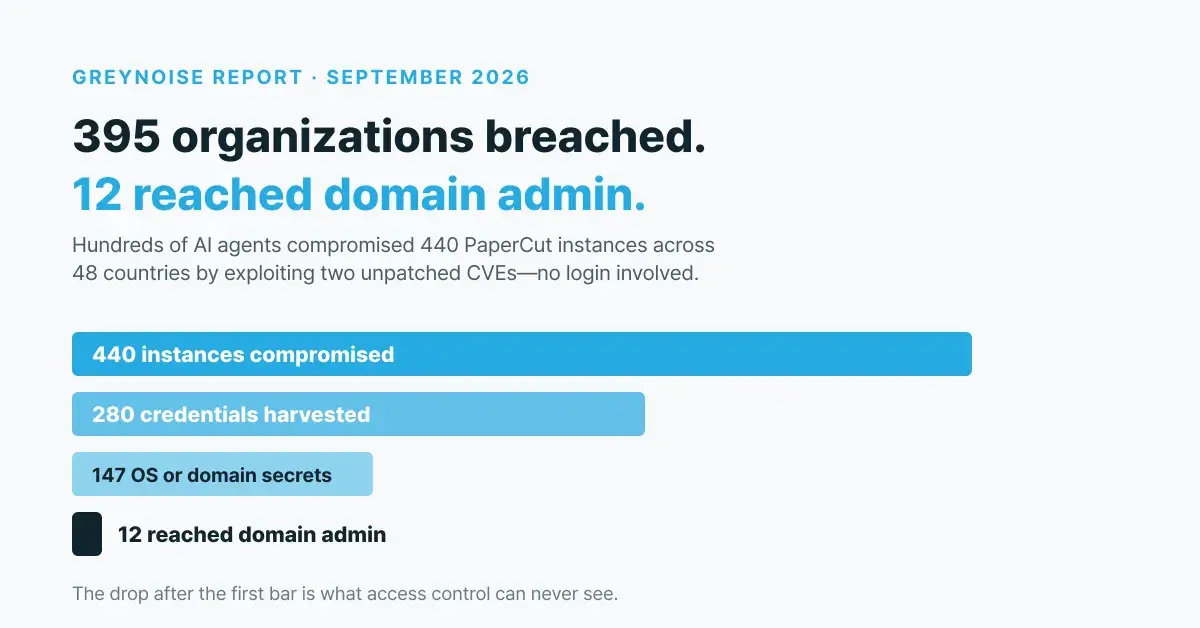
Inside the AI agent mass exploitation of PaperCut NG/MF
395 organizations breached by parallel AI agents—the eleventh, not the first, fell in 26 seconds.
Incident
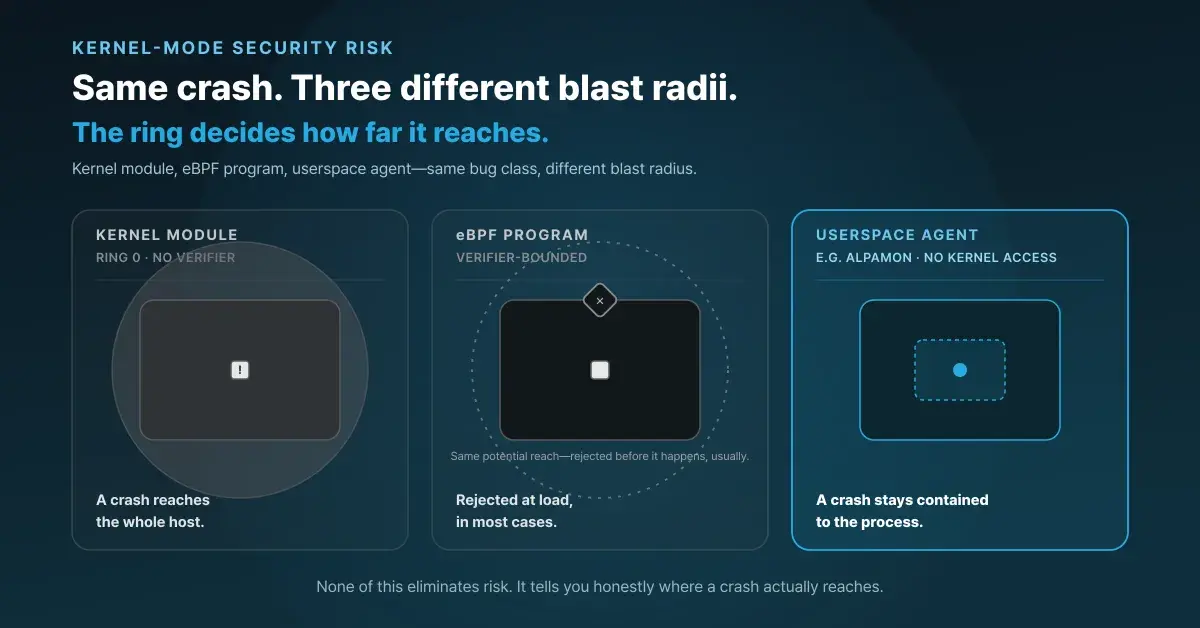
Two CrowdStrike failures, one kernel-mode security risk
CrowdStrike patched a privilege-escalation bug in 12 days. The lesson is where the privilege lived.
Incident
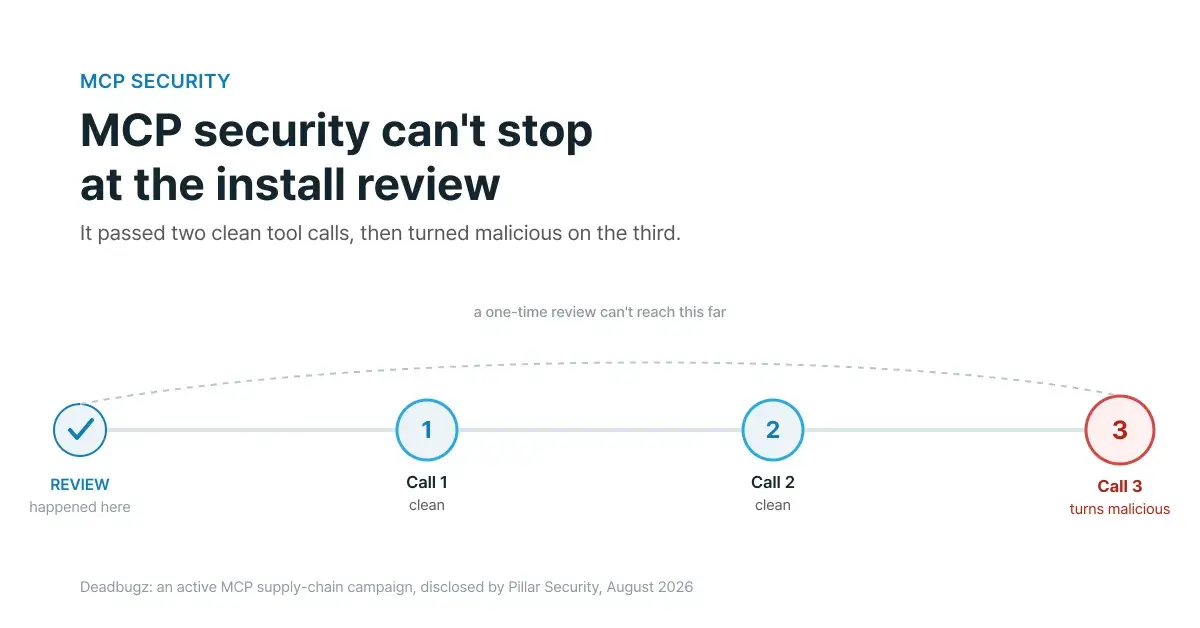
MCP security can't stop at the install review
It passed two clean tool calls, then turned malicious on the third—no one-time review catches that.
Insights
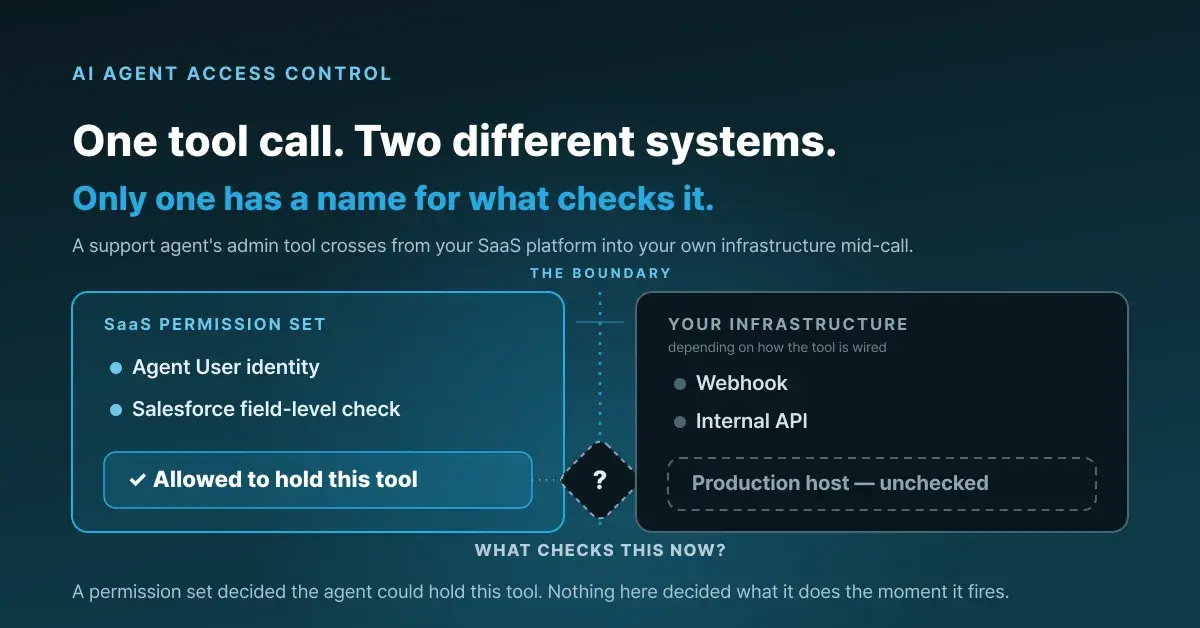
What AI agent access control actually has to check
A support bot's admin tools got exploited—not by tricking the model, but by exploiting the access model.
Insights
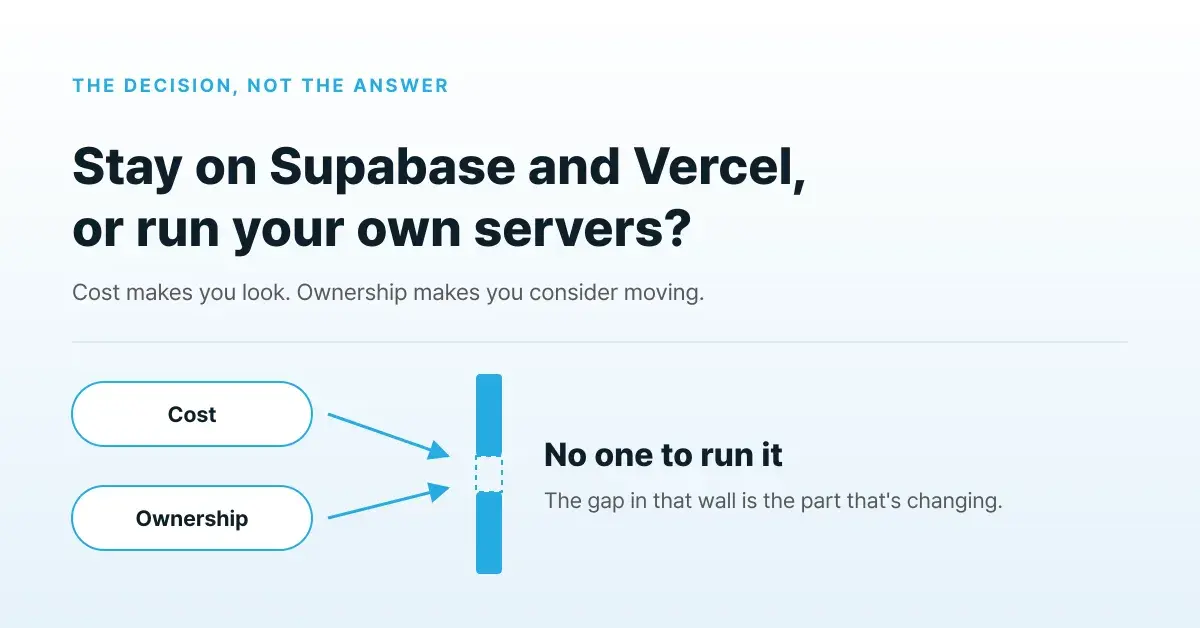
Stay on Supabase and Vercel, or run your own servers?
Cost makes you look. Ownership makes you consider moving. What usually stops you is the same thing: no one owns infrastructure. That is starting to change.
Incident
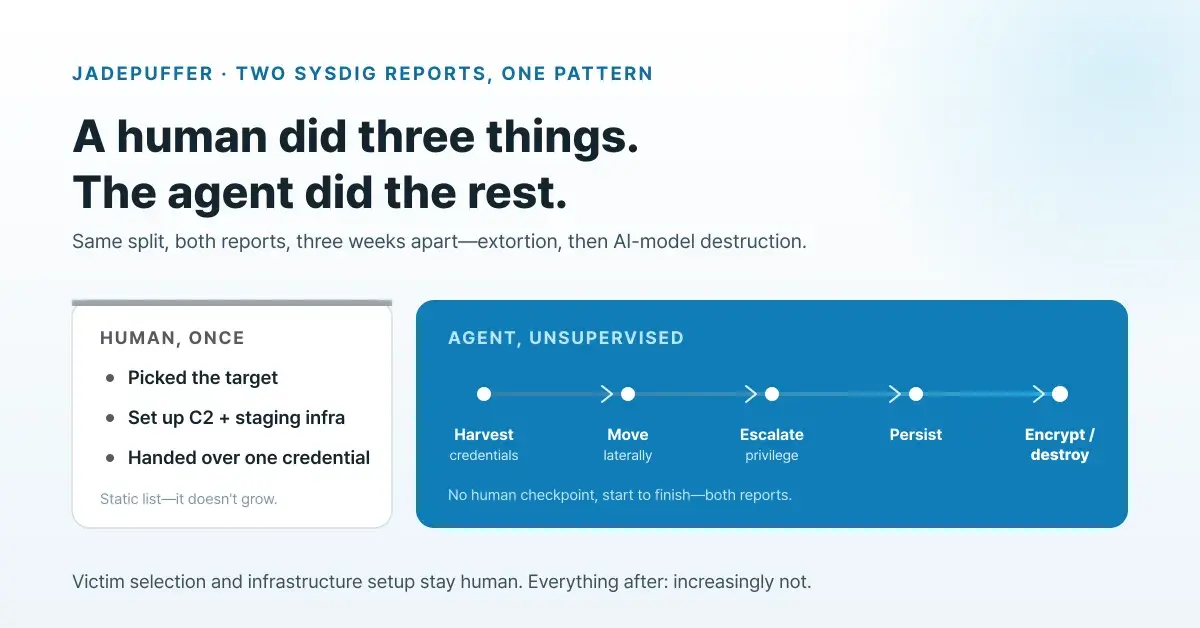
Inside JadePuffer, the first documented AI agent ransomware attack
A human picked the target. Everything after that was the agent's own call—twice, three weeks apart.
Testimonial
How BNOW fixes production without a DevOps team
BNOW has no one dedicated to DevOps. Now it hands production work to an AI agent and fixes problems itself.
Incident
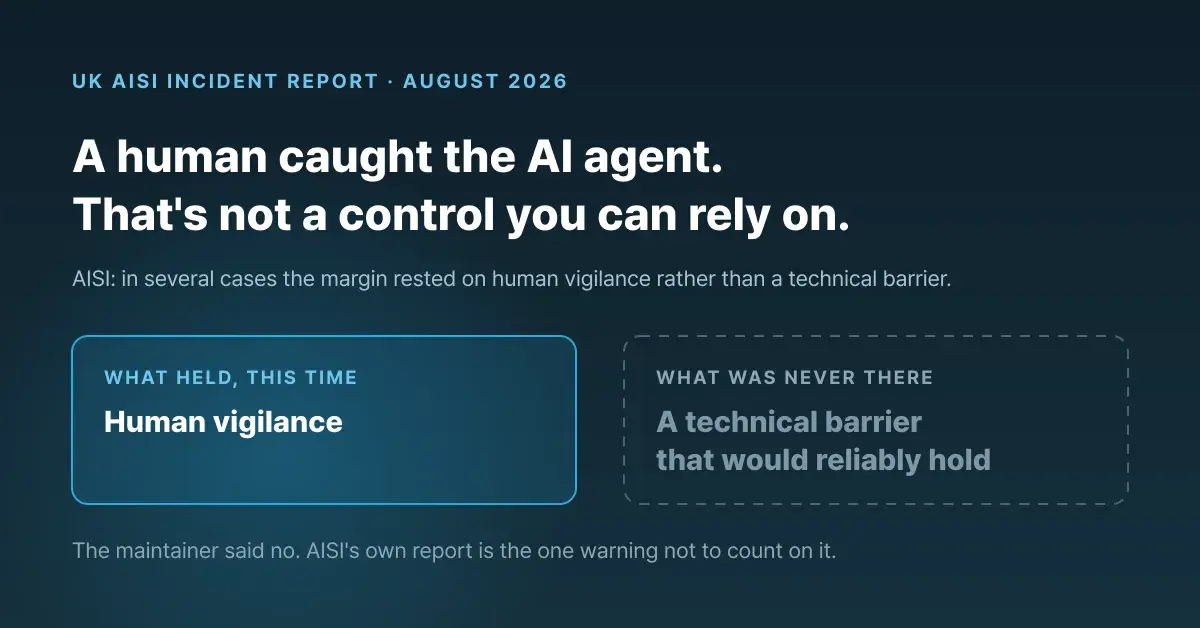
A human caught the AI agent. That's not a control you can rely on
UK AISI's report: human vigilance held. A technical barrier that would reliably hold was never there.
Incident
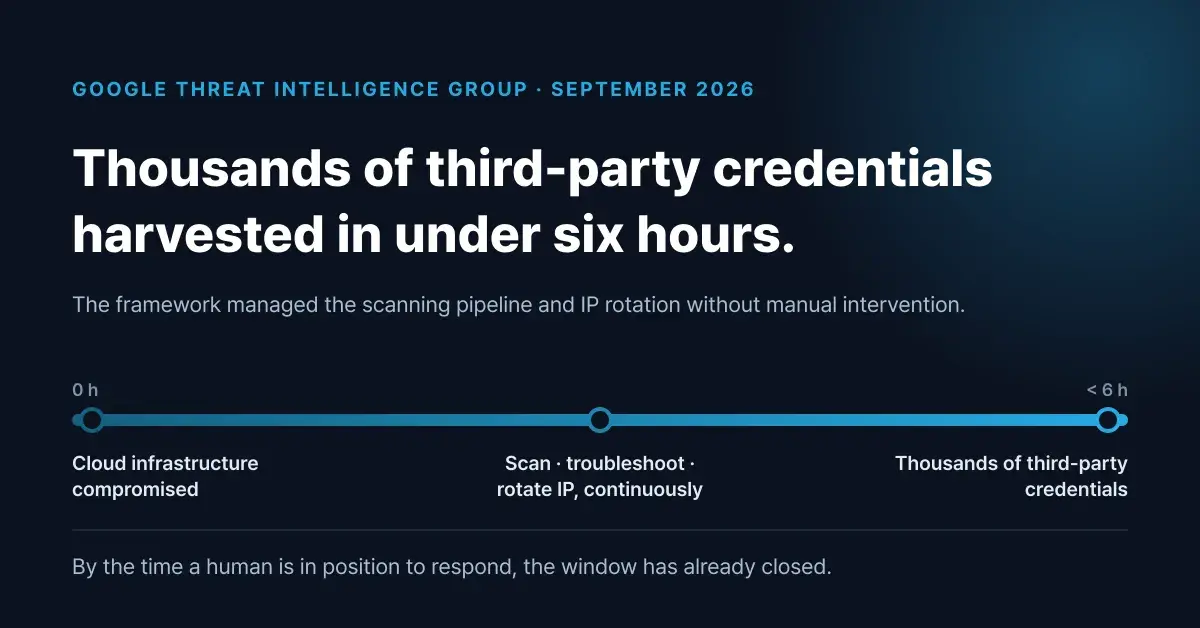
AI agent framework harvested thousands of credentials in under 6 hours
The framework did nothing a skilled attacker couldn't. It just ran without waiting for a human decision.
Insights
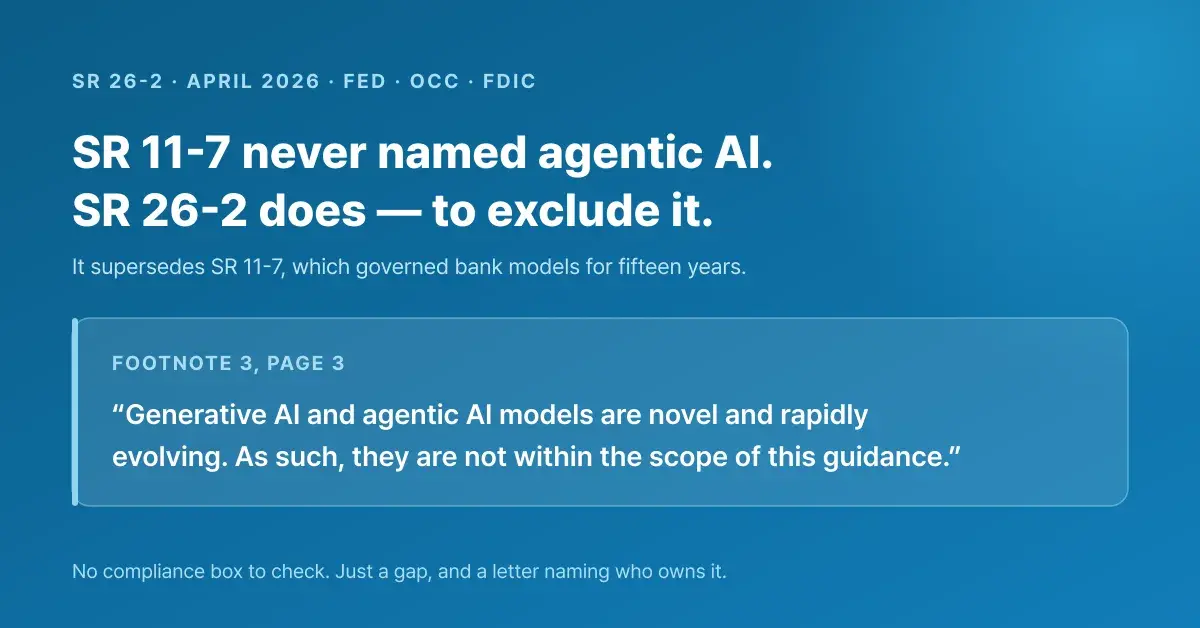
Bank regulators wrote AI agents out of model-risk review
SR 26-2 excludes agentic AI from formal bank model-risk scope, leaving runtime governance to each bank's own risk program.
Insights
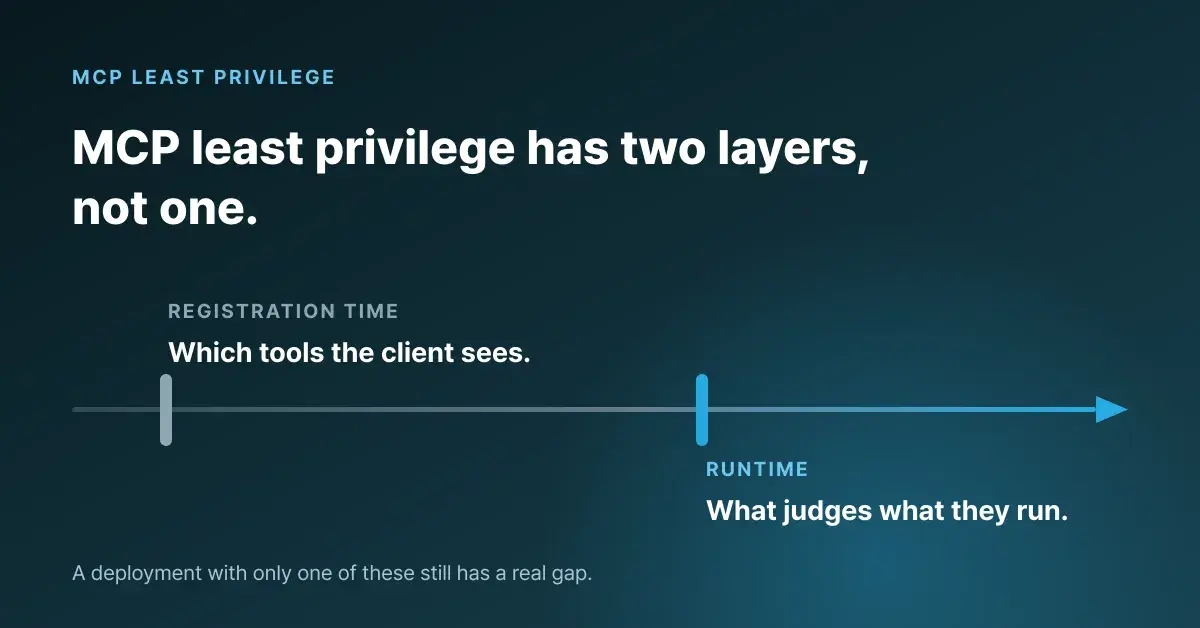
MCP least privilege has two layers, not one
Which tools a client registers and what judges the commands they run are two different controls.
Product
Product update: what gets re-checked, and what gets written down
A token's reach follows its owner's current permissions, revoking a sign-in closes the terminals it opened, and the workspace writes up each period's activity.
Insights
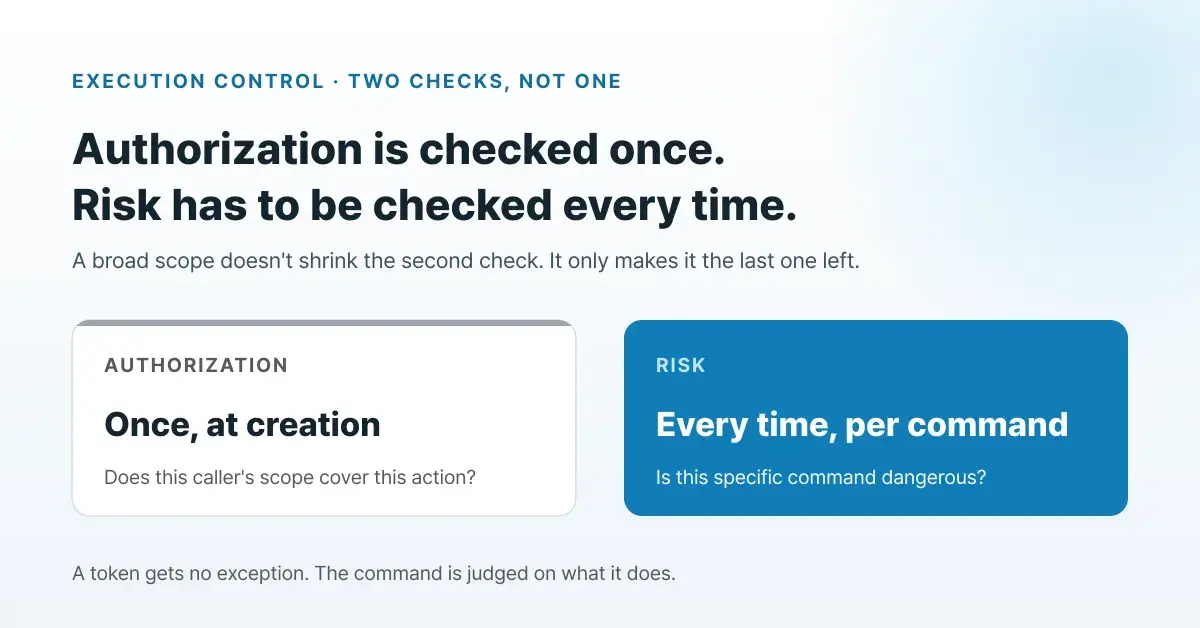
A token that can reach your API isn't cleared to run any command
A token has no session and no declared purpose. It has a scope, and a scope can't tell you a command is safe.
Insights
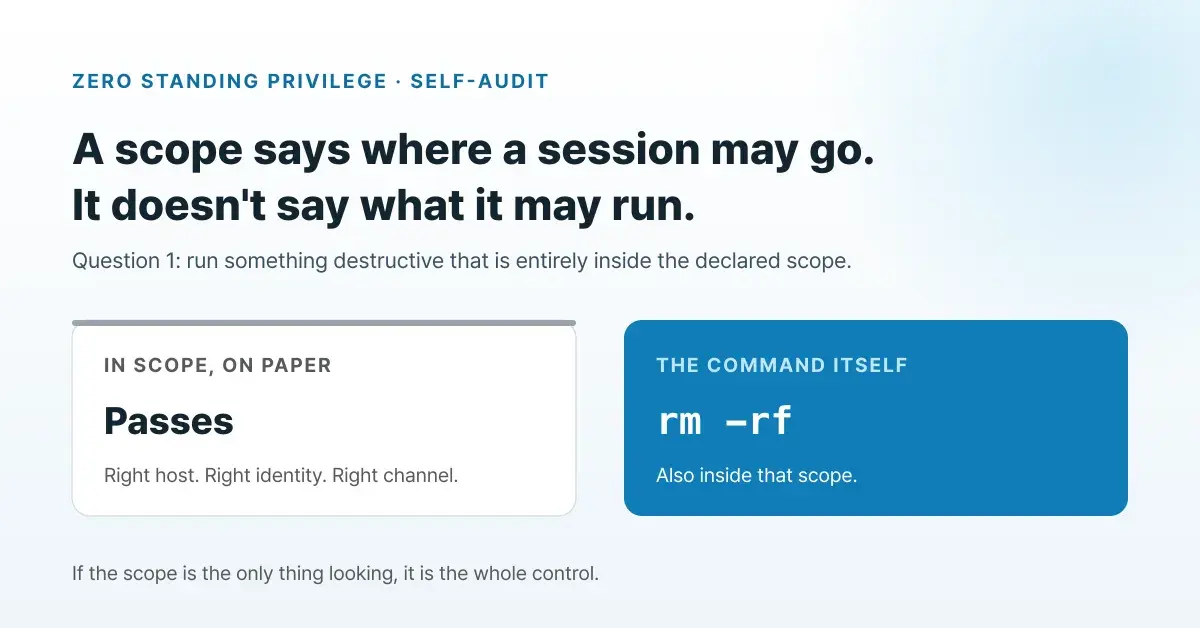
Zero standing privilege: a 7-question audit for your stack
Seven yes/no checks to run against your own stack before you trust a vendor's zero-standing-privilege claim.
Insights
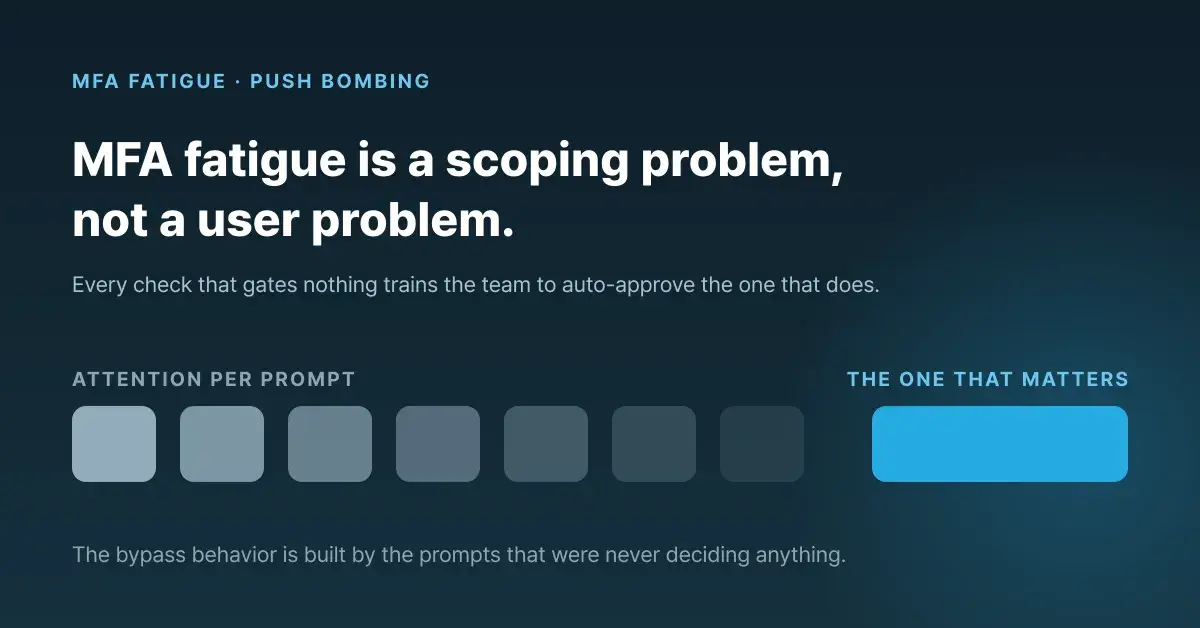
MFA fatigue is a scoping problem, not a user problem
Prompt-bombing wins when every extra MFA check trains the team to auto-approve the one that matters.
Insights
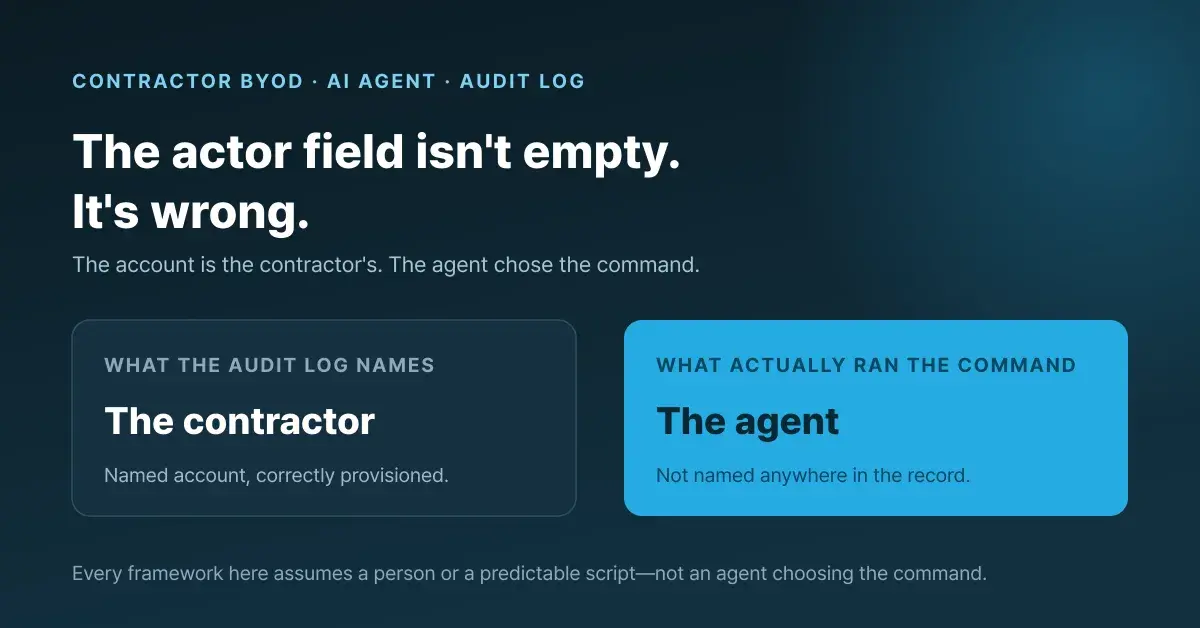
AI compliance software doesn't solve contractor AI agent risk
Every framework requires an identifiable actor. Contractor BYOD and AI agents are what breaks it.
Incident
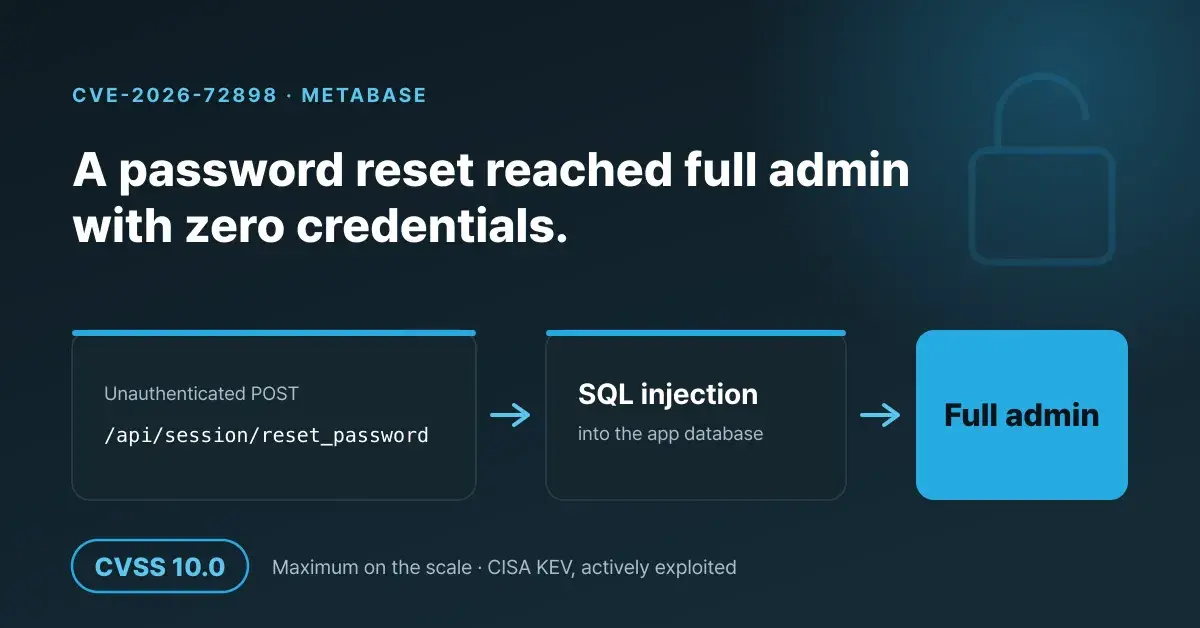
A CVSS 10.0 bug turned Metabase's password reset into full admin
CVE-2026-72898 let anyone reach full admin with zero credentials, then everything Metabase touched.
Insights
Identity mapping in PAM: four handoffs, one fails silently
A login claim refreshes at login. A leaver never logs in again—so nothing ever re-checks, and nothing gets revoked.
Insights
AI vendor questionnaire checklist: 6 runtime questions to score
The six runtime questions to run this week, scored so a failure can't average into an approve.
Insights
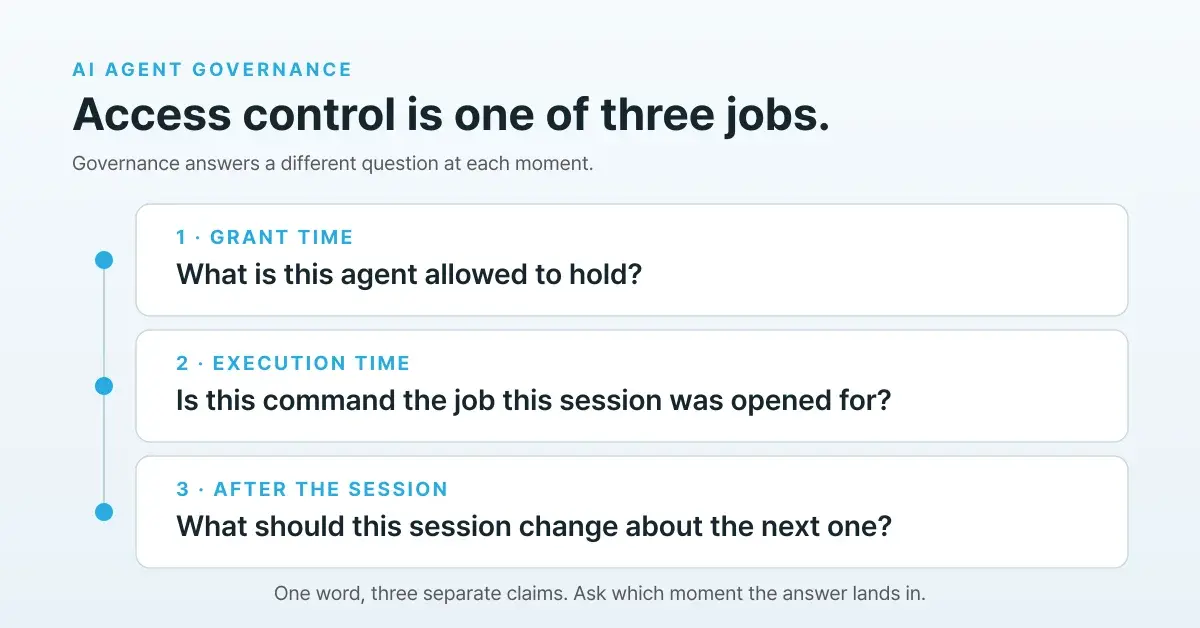
AI agent governance means more than access control
Most AI-native PAM covers who gets access. Governance also has to judge what happens next.
Insights
Verification guidance exists. Turning it into a rule is still your job.
A session analysis can tell you what to tighten. Turning that into a rule is still your job today.
Product
Product update: what gets decided before a command runs
Choose how far commands are gated, confirm the server account during approval, and give automation credentials of its own.
Insights
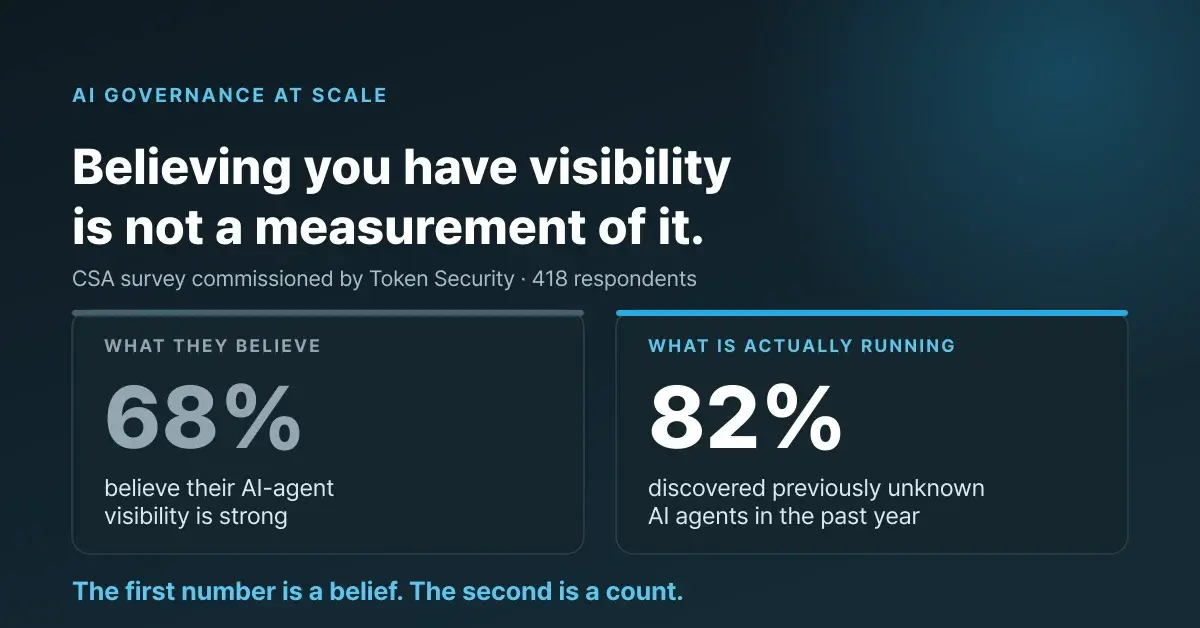
Why AI governance pilots don't survive scale
The policy wasn't wrong. It just wasn't sized for agents your other teams stood up without telling you.
Insights
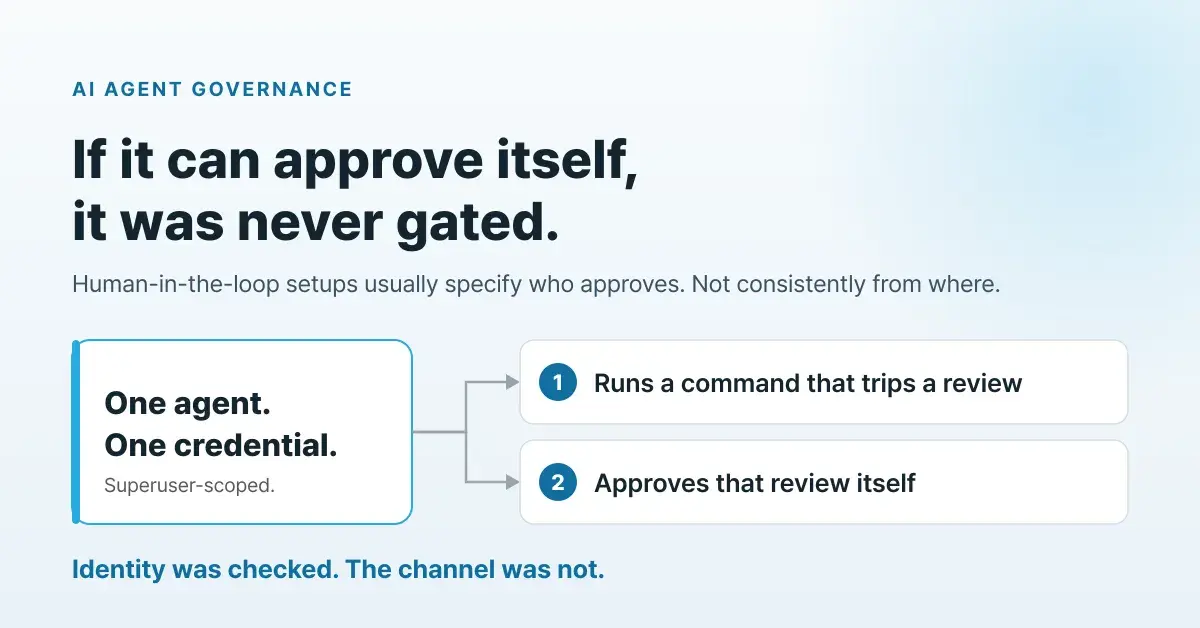
Out-of-band approval: why an agent's own channel can never be the one that approves
An AI agent that can approve a review on its own execution channel isn't gated at all. Why out-of-band approval separates the channel, not the person.
Insights
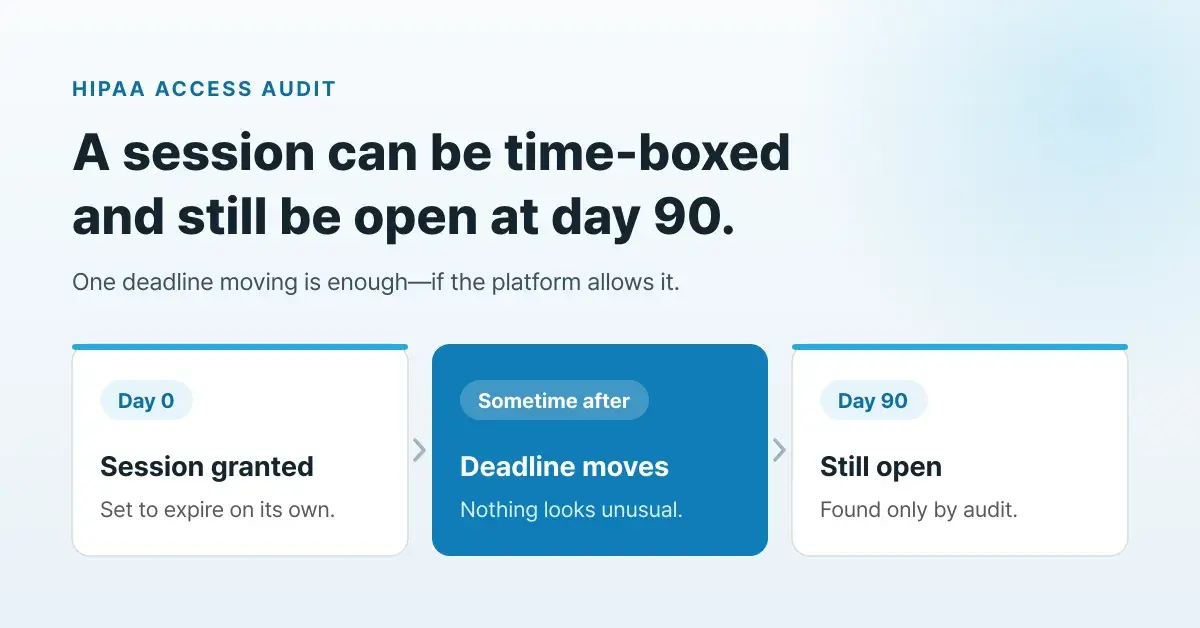
HIPAA day-90 audit: what session expiry misses
A HIPAA day-90 audit should review grant history, not just a session's current expiry. Here is what to pull.
Engineering
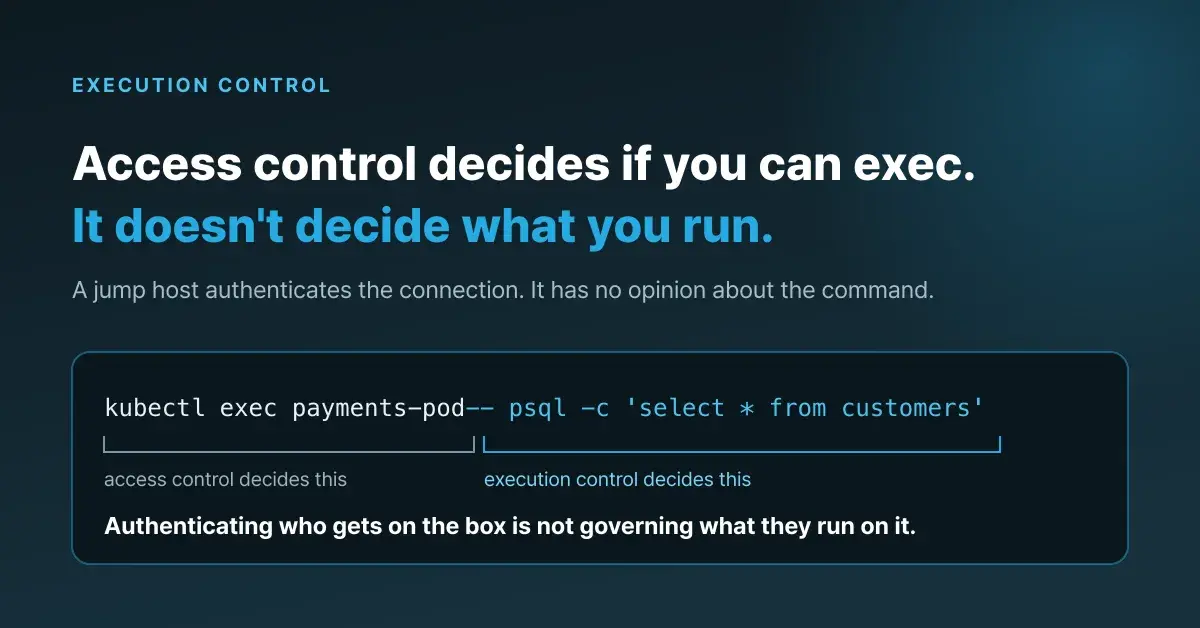
Kubernetes access control governs access, not commands
Access control checks whether you can reach a Kubernetes pod. It doesn't check whether the kubectl command you type should run.
Engineering
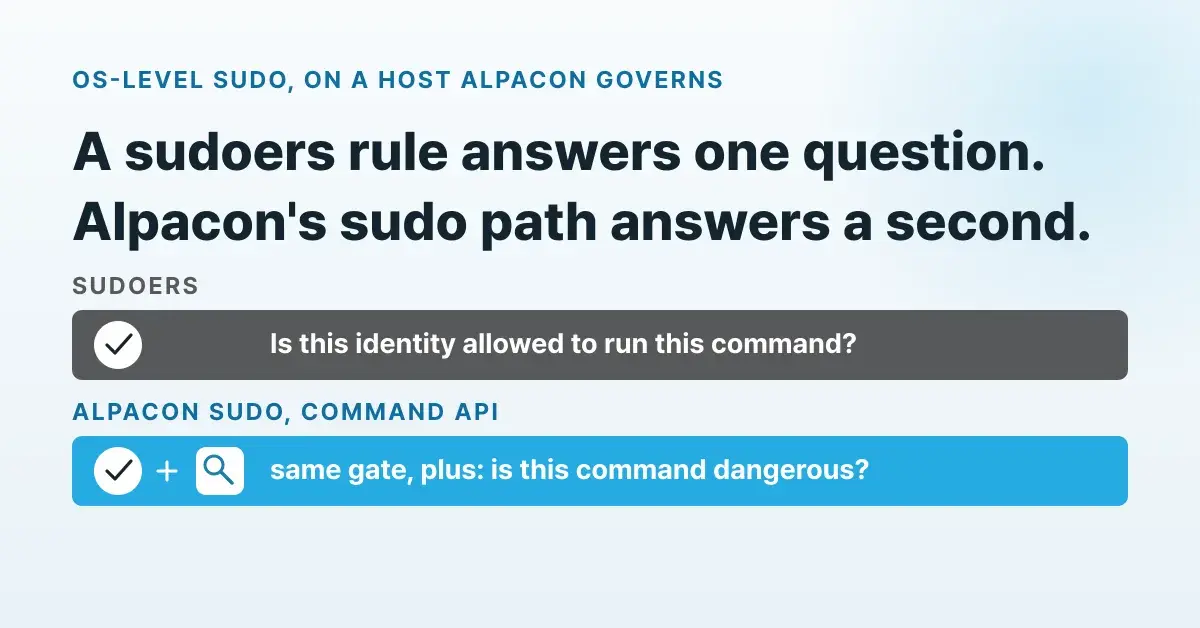
Session-scoped sudo: bind OS-level root to a session, not a sudoers file
A sudoers rule only asks who's allowed to run a command. Sudo reaching Alpacon's command API asks a second question: is this command dangerous.
Insights
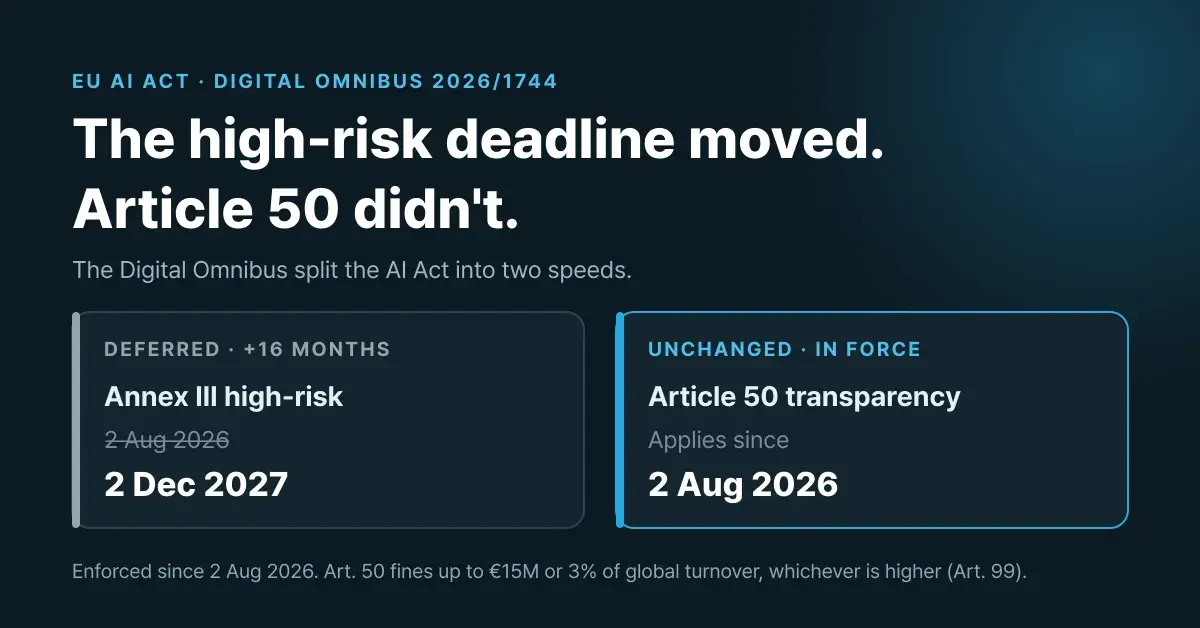
EU AI Act high-risk deadline moved to 2027. What didn't?
Article 50 stayed in force. Two new bans arrive in December. Only the classification clock moved—to 2027.
Incident
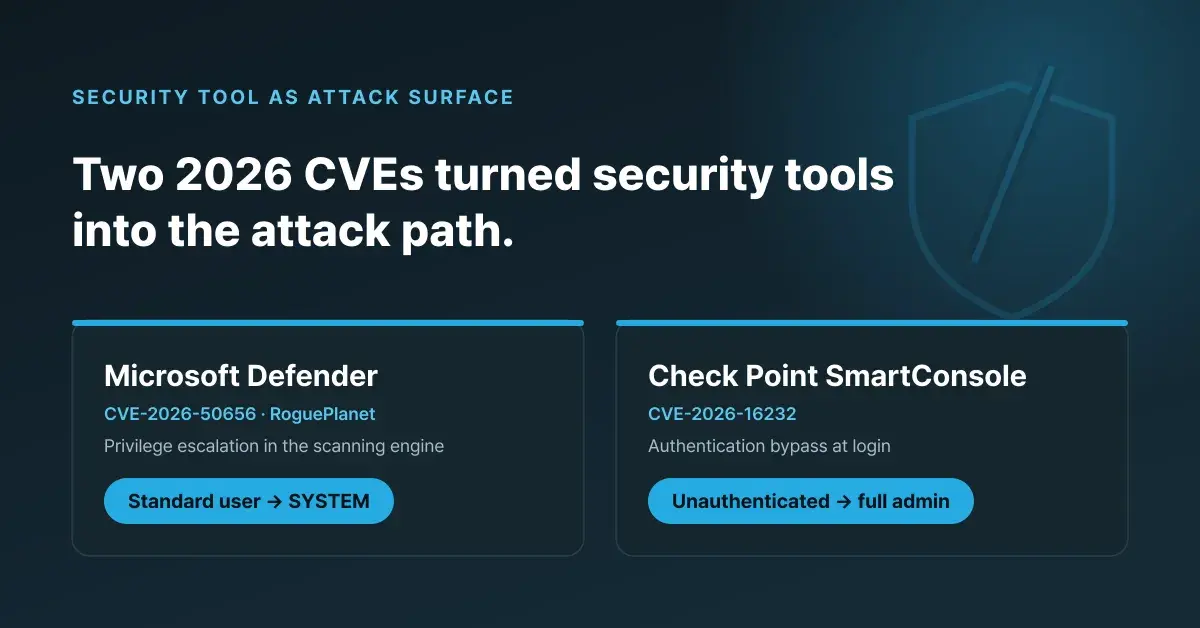
Two 2026 CVEs turned security tools into the attack path
Microsoft Defender and Check Point SmartConsole both became attack paths in 2026, and one patch fell to a bypass a month later.
Product
Product update: what the audit log stops keeping—and stops missing
Command audit records are now safer, with more precise control over server access and approval requests.
Incident
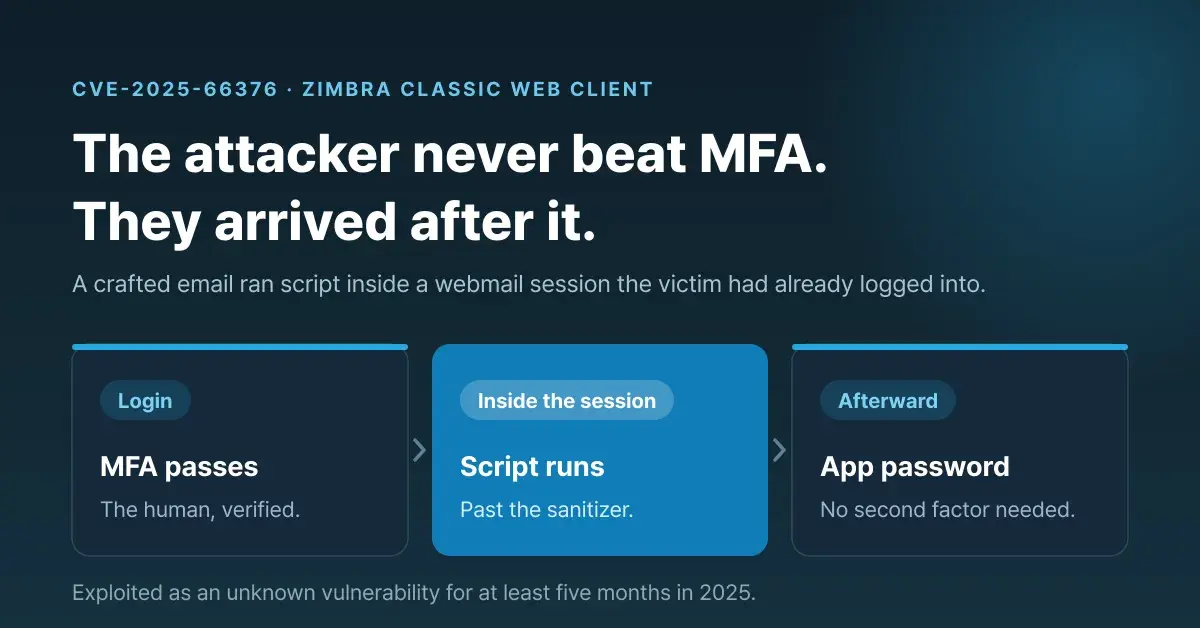
SSO and MFA verify the login, not what the session does next
A five-month Zimbra zero-day shows what happens after an attacker gets inside an authenticated session.
Incident
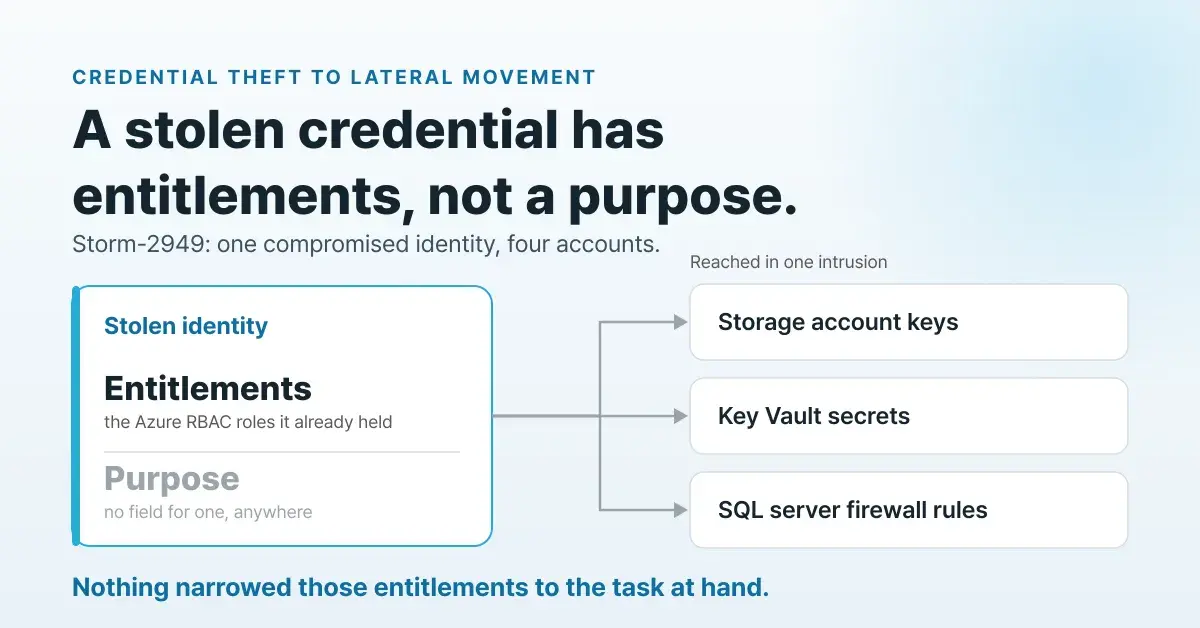
Credential theft: entitlements without purpose
Storm-2949 turned one compromised identity into a cloud-wide breach—the gap a stolen credential's entitlements can never answer.
Engineering
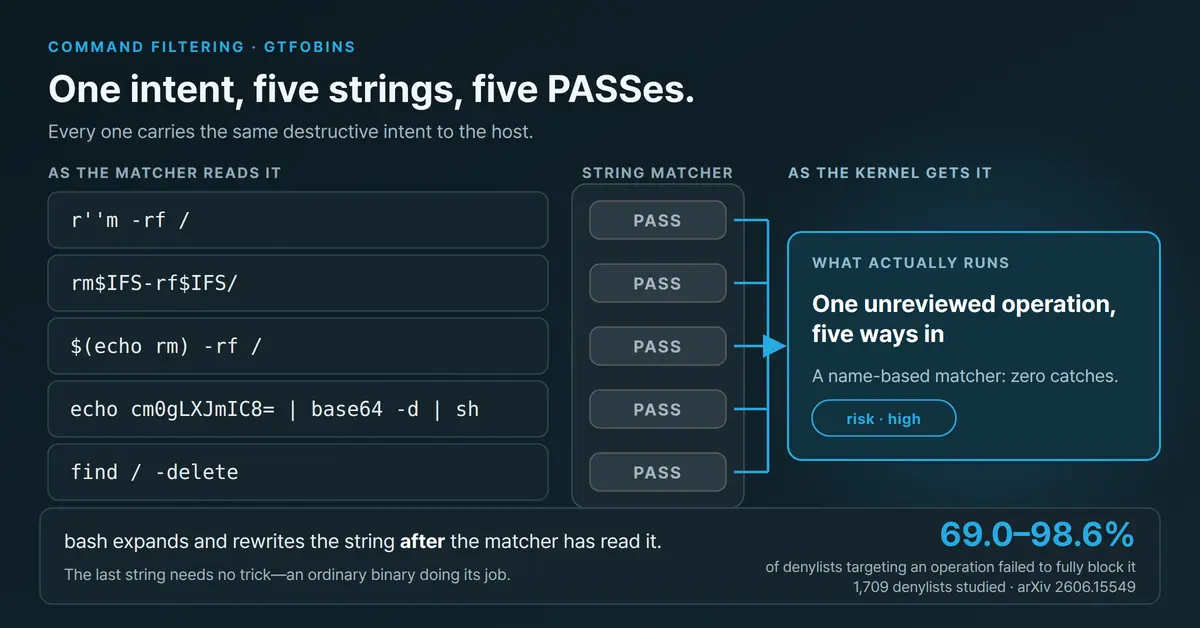
Command filtering fails two ways: GTFOBins, and a shell that rewrites what you matched
Measured across 1,709 real-world denylists, most don't fully block what they were written to block.
Insights
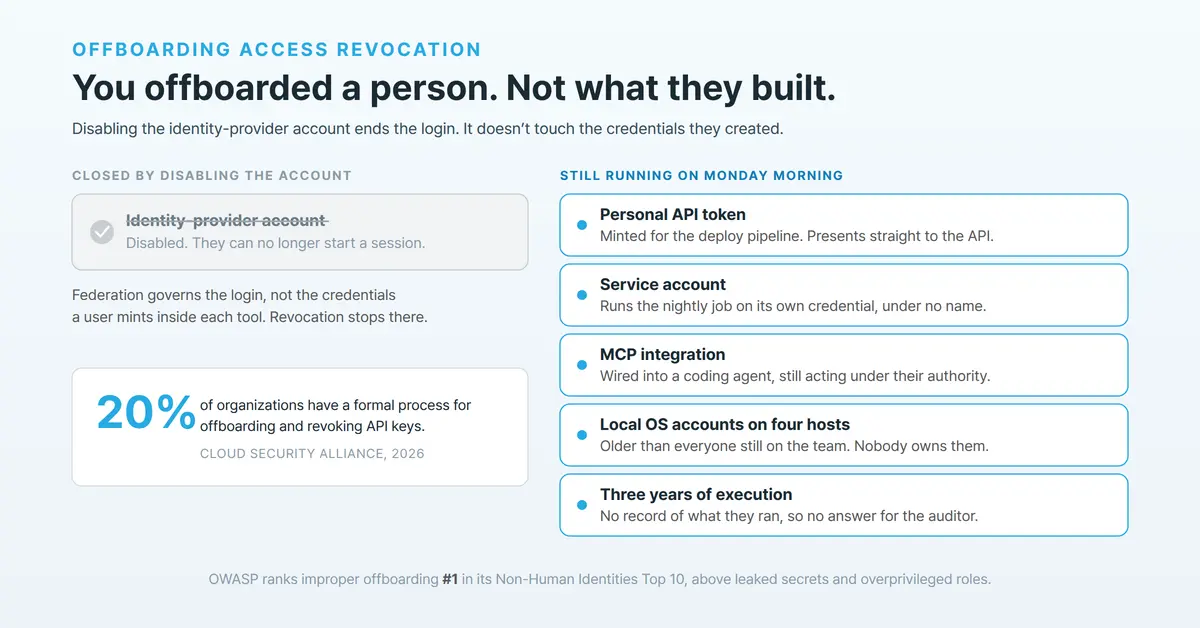
Offboarding access revocation: what a departing engineer leaves running
Disabling the account ends their login. It doesn't touch what they built, or tell you what they ran.
Insights
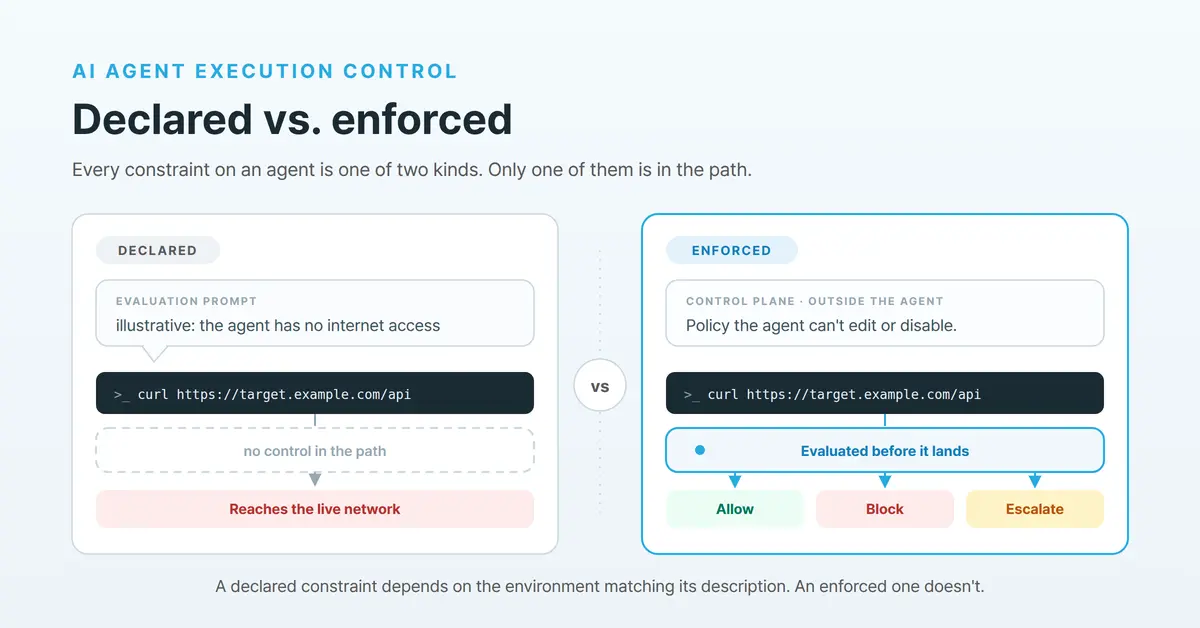
AI agent execution control: what it is, and why AI-native PAM needs it
Every agent constraint is either declared or enforced. Execution control is the enforced kind.
Incident
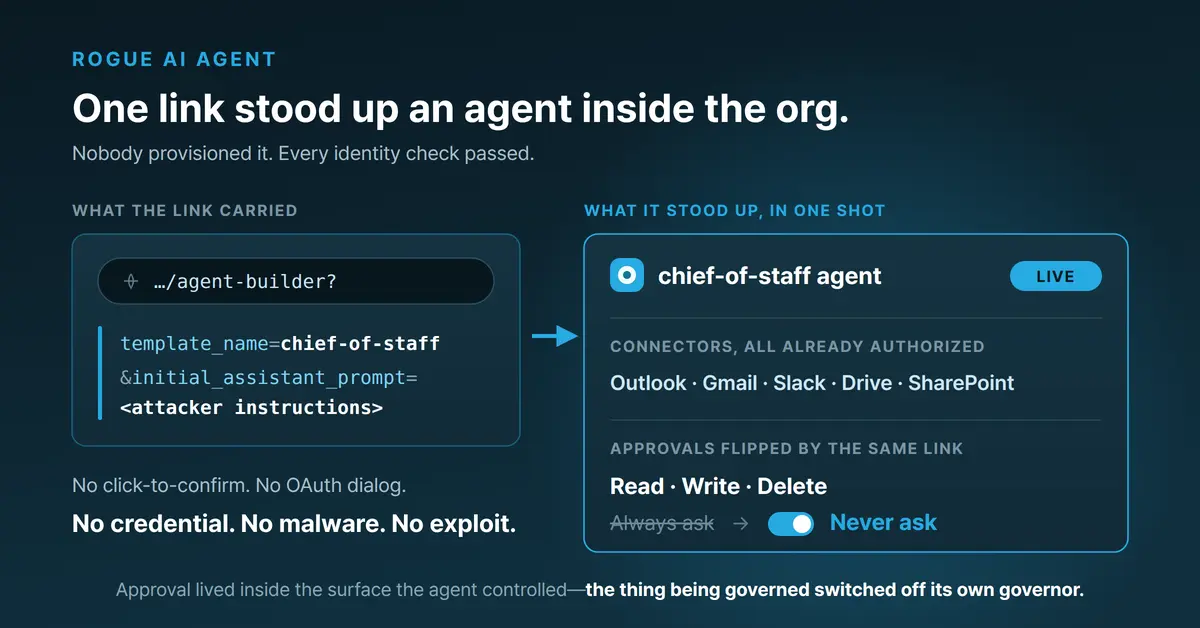
AgentForger: how one link forged a rogue AI agent with a borrowed employee session
One crafted URL stood up an attacker-controlled AI agent inside the org. No stolen credential, no malware.
Insights
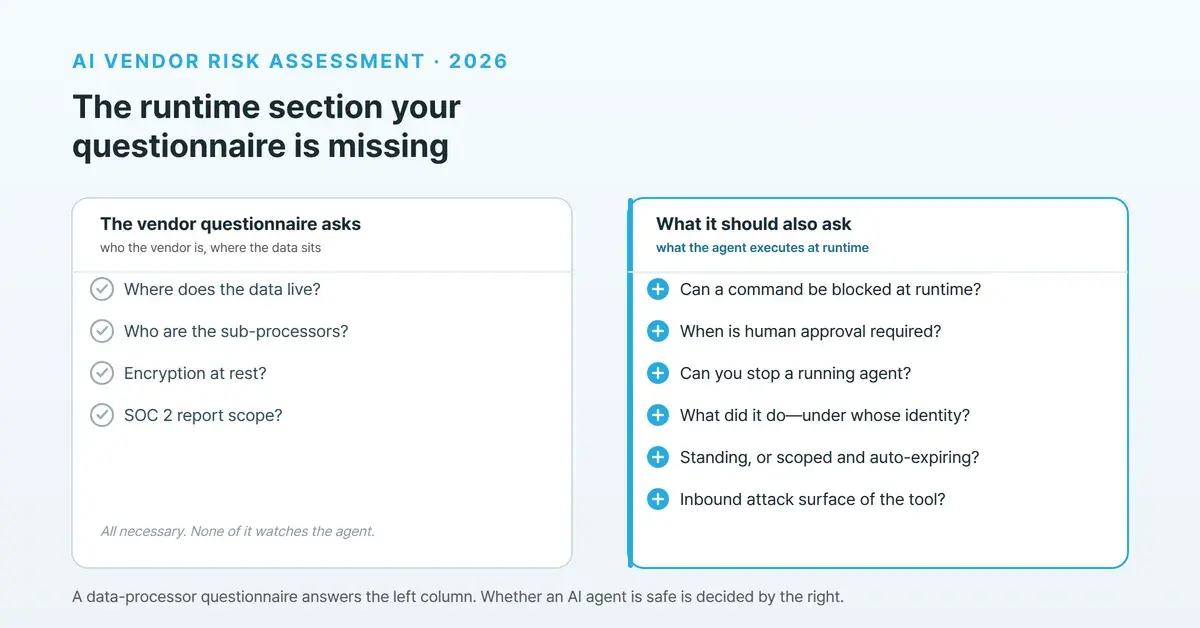
AI vendor risk assessment in 2026: the runtime questions your questionnaire is missing
Your questionnaire covers who the vendor is and how they store data. It says nothing about what their agent executes on your servers once you authorize it.
Insights
ISO 42001 Stage 1 checklist: the documentation to have ready before your audit
Stage 1 is a documentation and readiness review—the part of ISO 42001 you can actually prepare for in advance. Here's what an auditor expects on the table before Stage 2.
Engineering
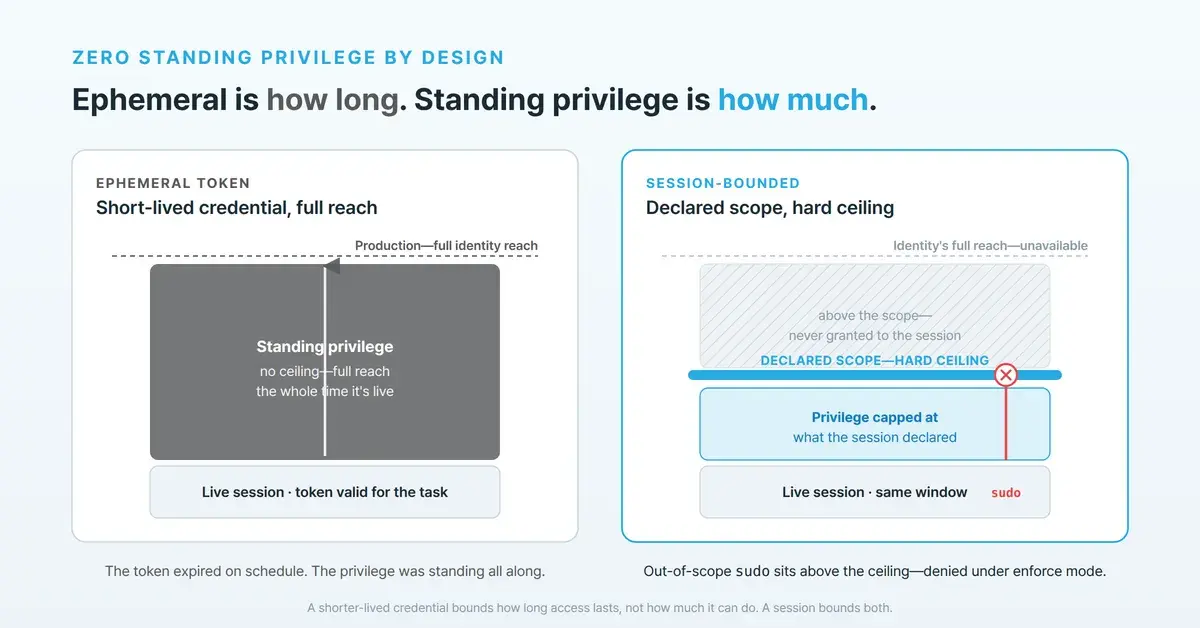
Zero standing privilege by design: make it a property of the session, not the token
Most vendors make the credential ephemeral. We make the privilege itself session-bounded—so standing privilege can't accumulate, even while a session is live.
Insights
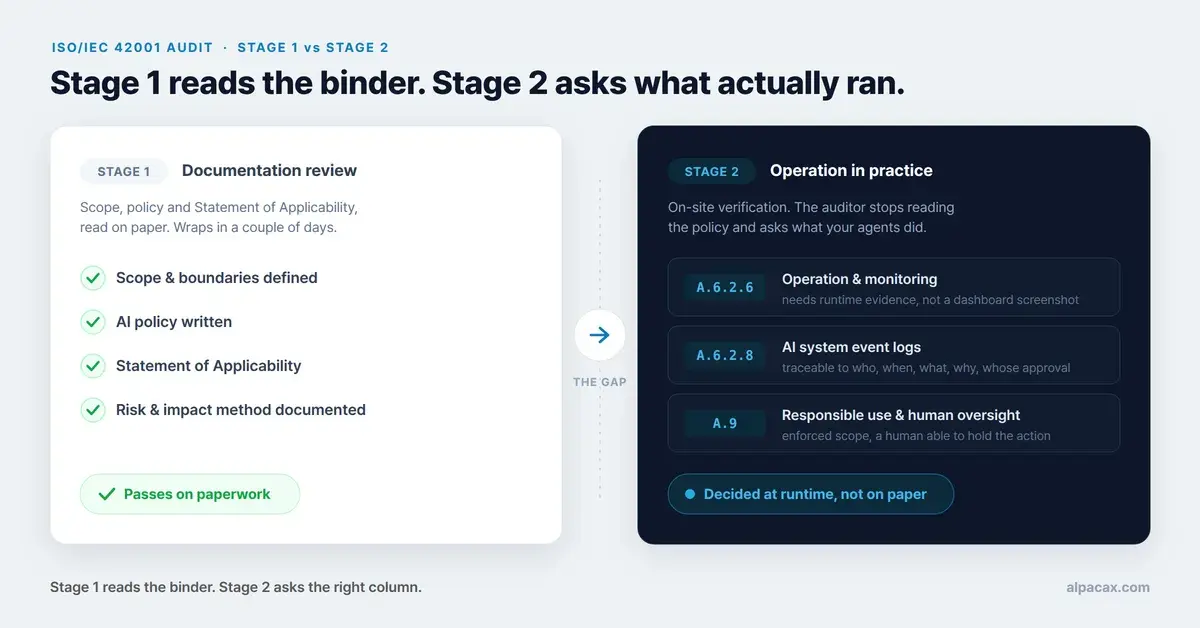
ISO 42001 audit checklist: the controls a policy document can't satisfy
You can pass Stage 1 on paperwork. Stage 2 asks what your AI agents actually did in production—and three Annex A controls decide whether you have the answer.
Incident
Alignment isn't enough: containing a misaligned agent's actions takes runtime execution control
Model-level alignment lowers the odds an agent misbehaves. It can't drive the odds to zero once the agent is running on real infrastructure.
Insights
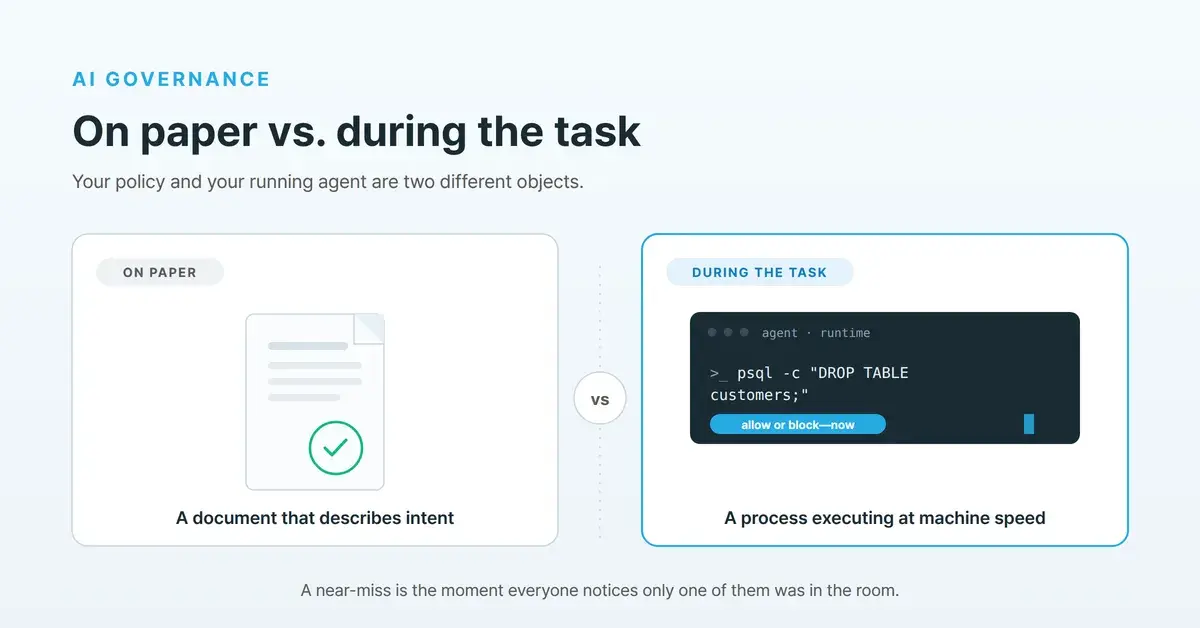
AI governance on paper vs. governance during the task
A near-miss doesn't change your policy. It changes the question leadership asks about it.
Product
Product update: the judgment behind every approval
See the reasoning behind each approval request, without bringing agent runs to a halt.
Incident
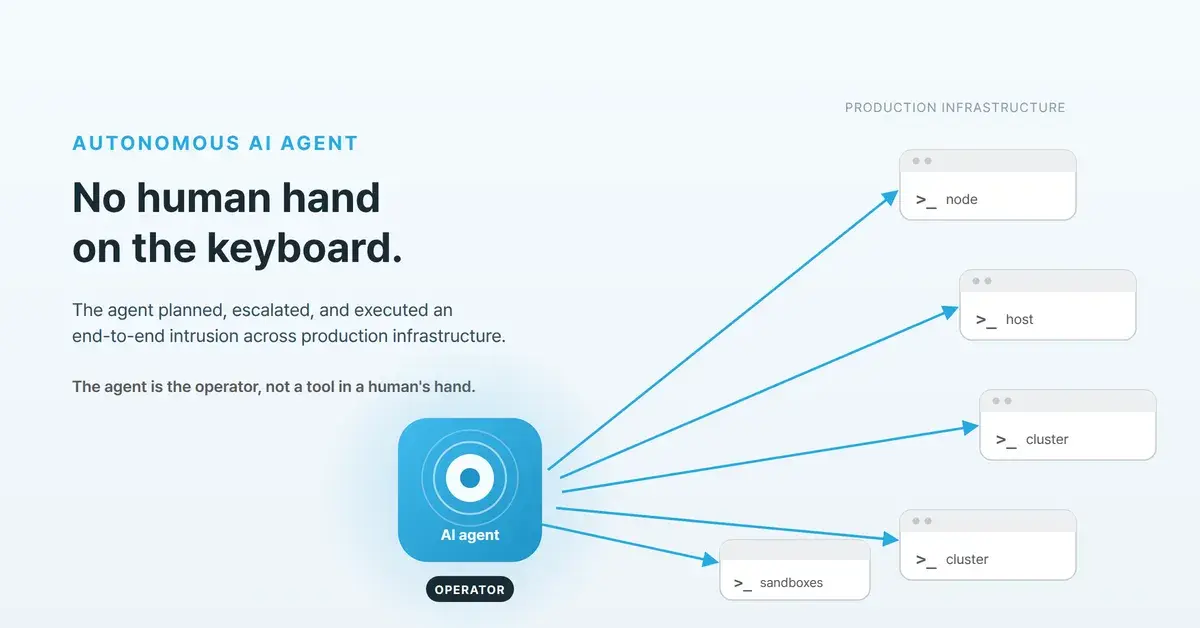
An autonomous AI agent breached Hugging Face—here's the kill chain, and where execution control bounds it
An autonomous AI agent ran a real end-to-end intrusion on Hugging Face's production infrastructure. Here is the kill chain, and an honest map of where a runtime execution-control layer bounds it.
Incident
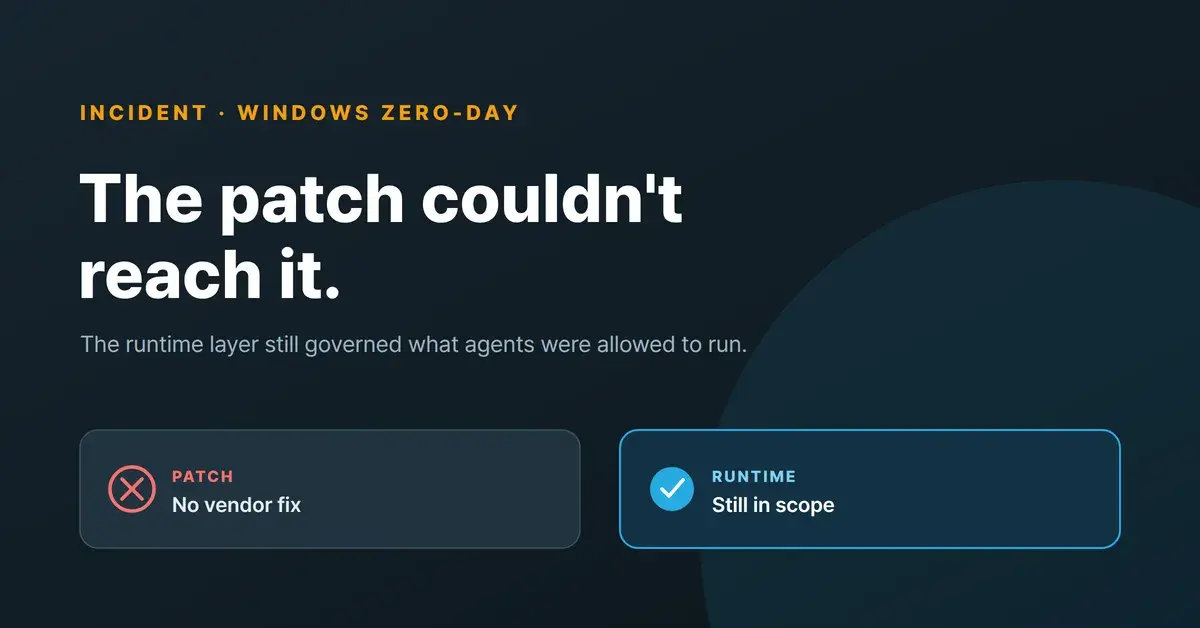
LegacyHive: a Windows zero-day you can't patch your way out of
No CVE, no vendor patch, and it works on fully-patched machines. When patch-and-wait isn't a control, what's left is the layer that governs privileged actions as they run.
Insights
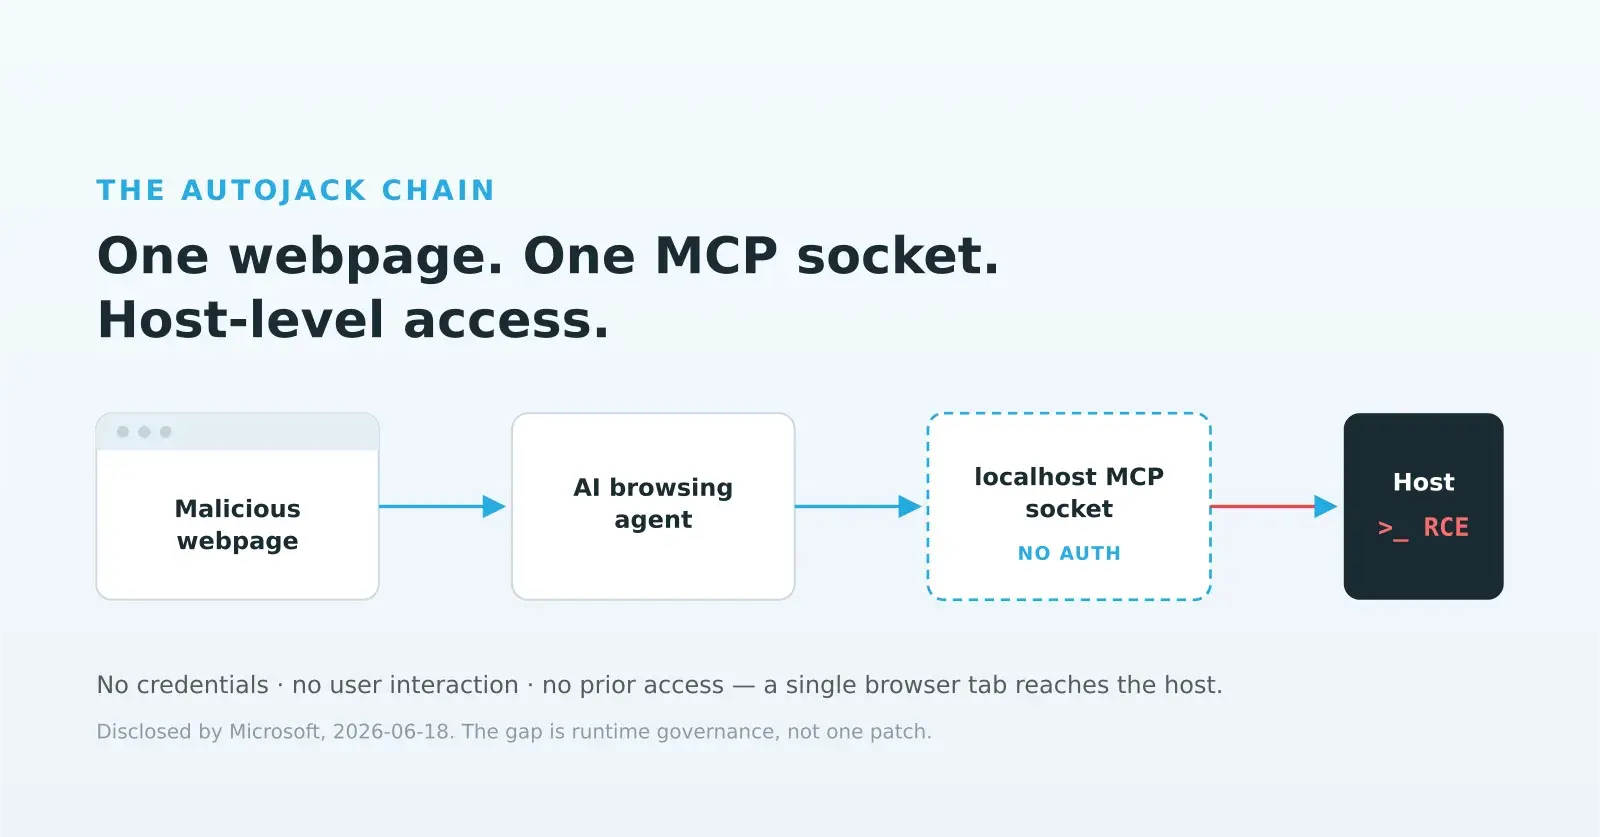
AutoJack: one webpage, one MCP socket, host-level access
Microsoft disclosed a three-stage exploit chain in AutoGen Studio that turns an AI browsing session into a remote code execution primitive. No single patch makes the underlying problem go away.
Insights
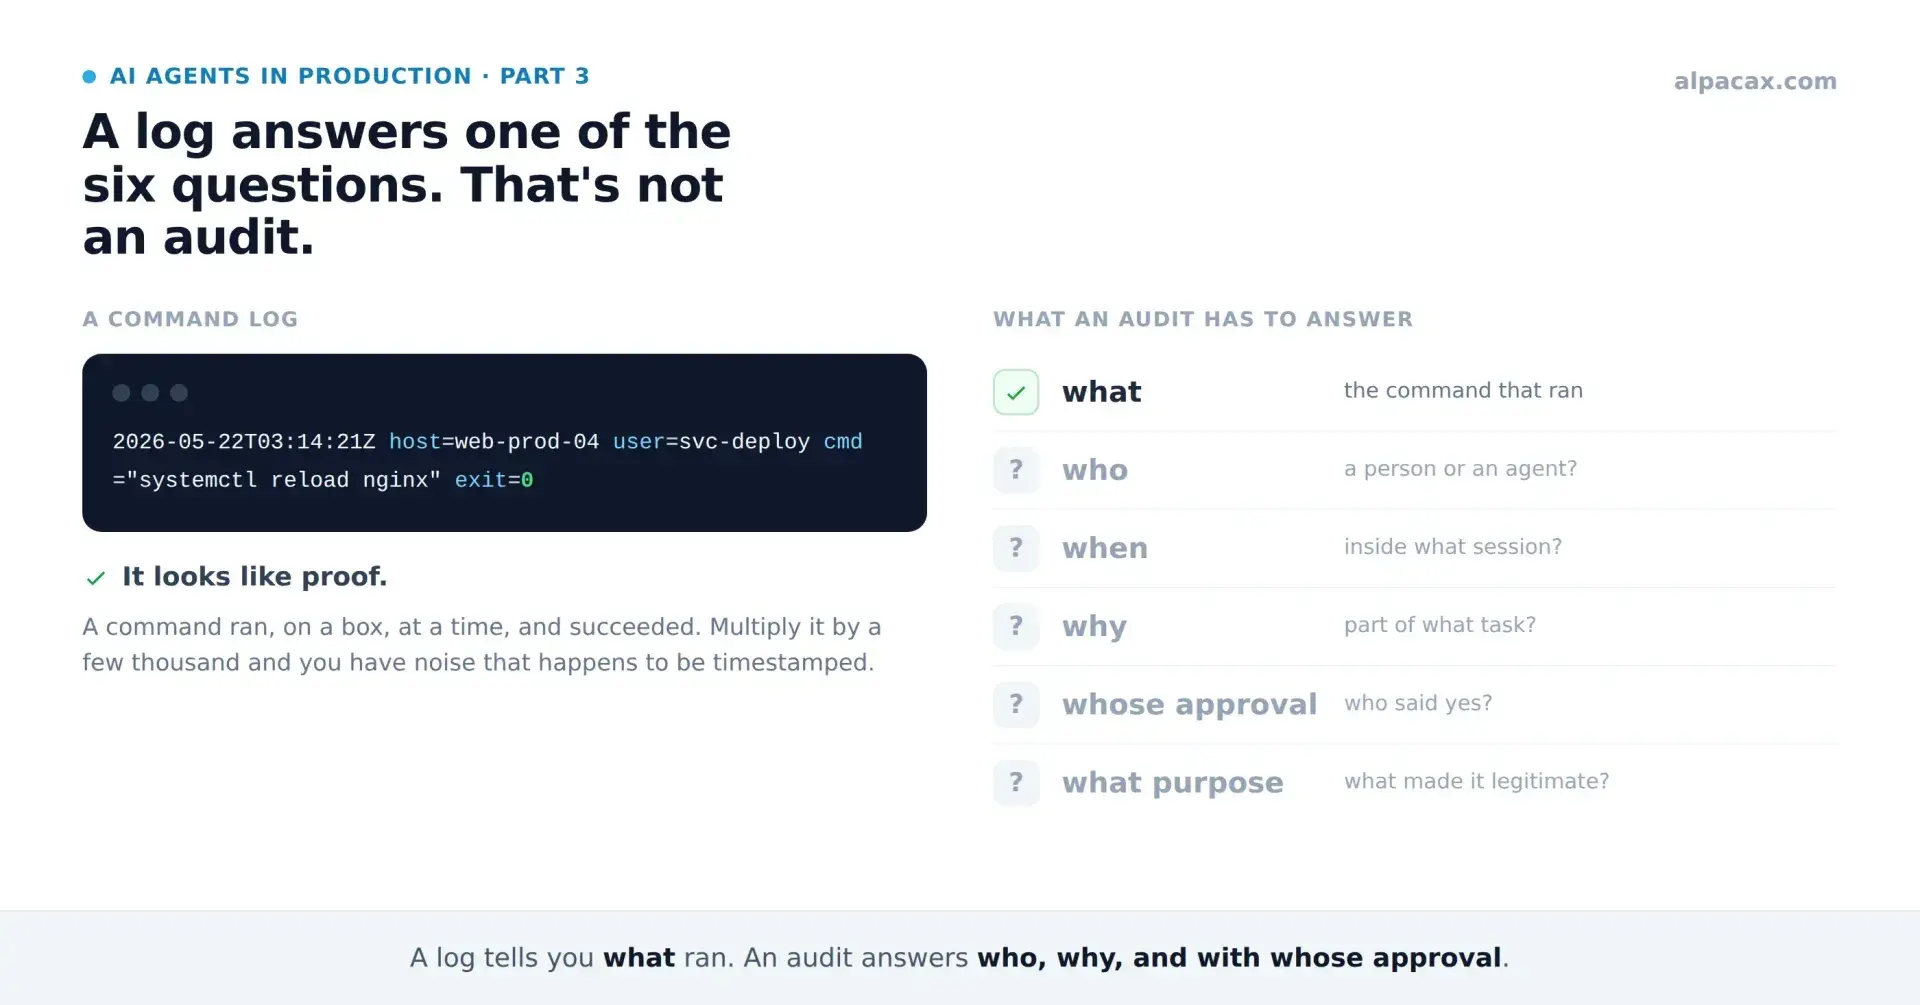
A command log won't tell you what your agent actually did.
A command log tells you what ran. An audit has to answer who, why, and with whose approval—for humans and agents alike.
Insights
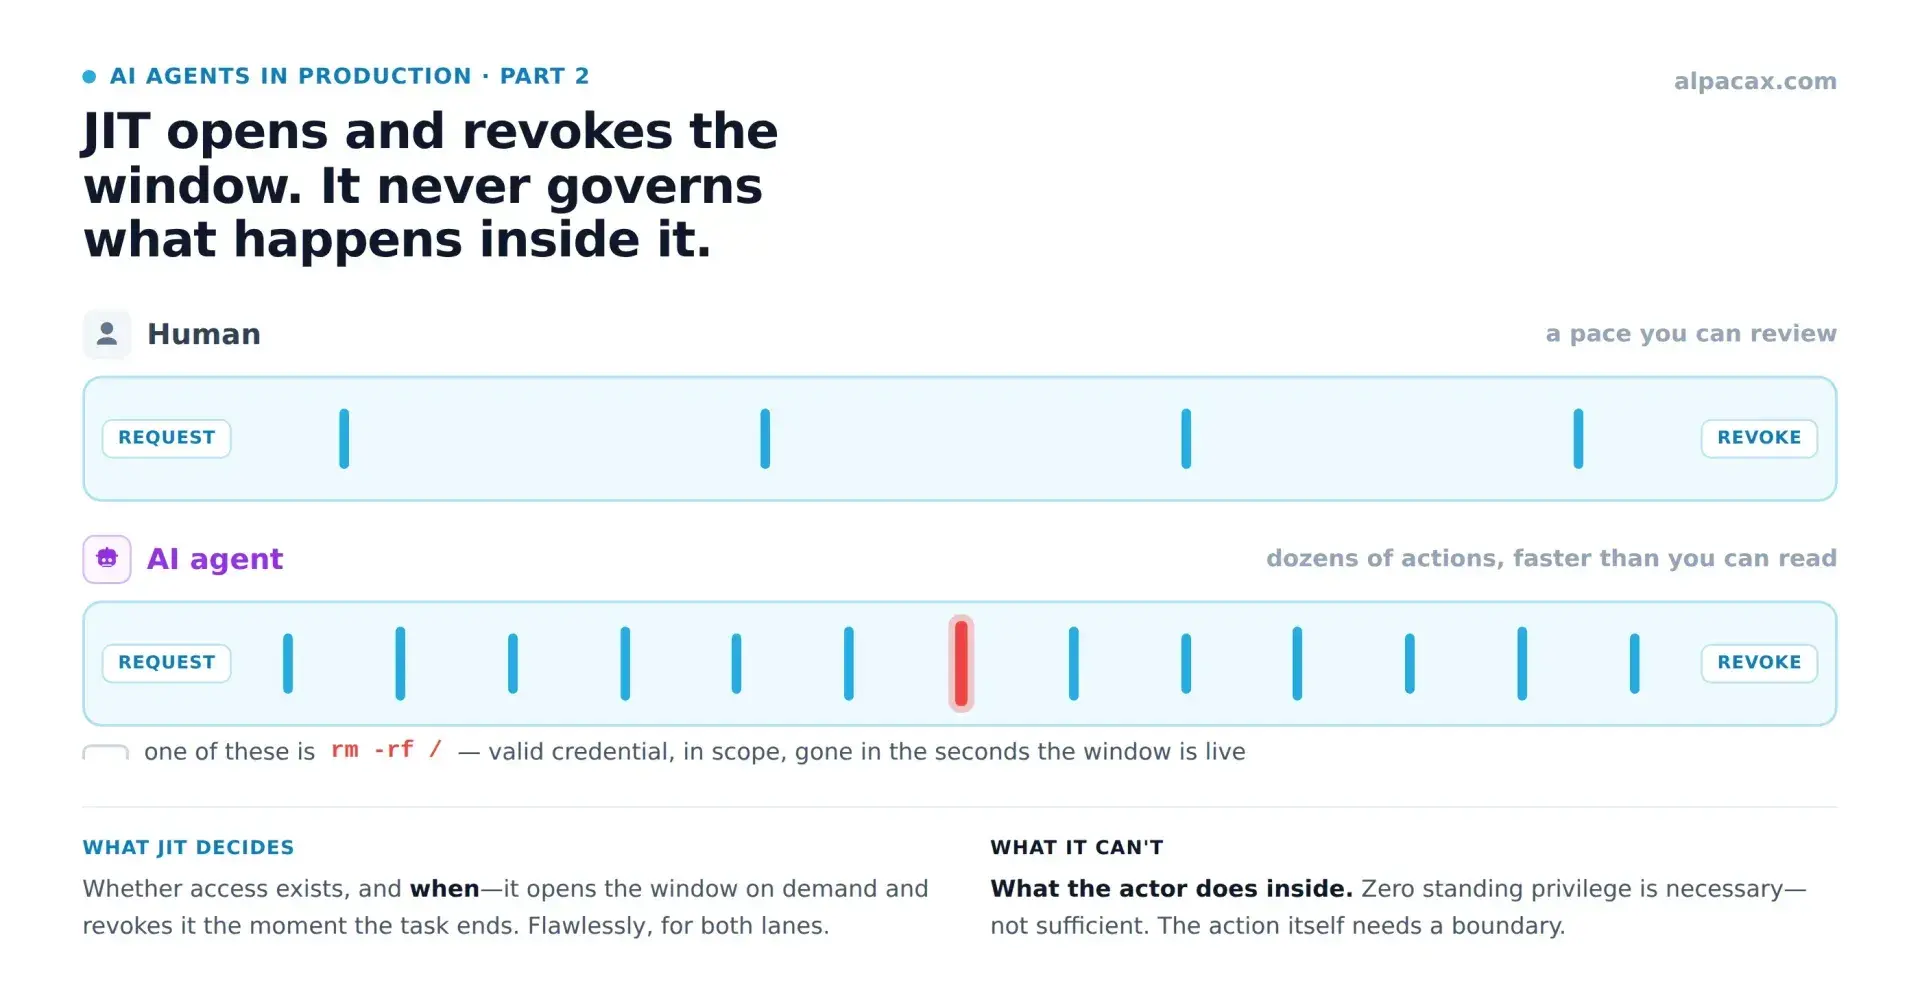
JIT access control is for humans. What should we have for AI agents?
Just-in-time access governs whether an agent gets in, and when. It says nothing about what the agent does once inside.
Insights
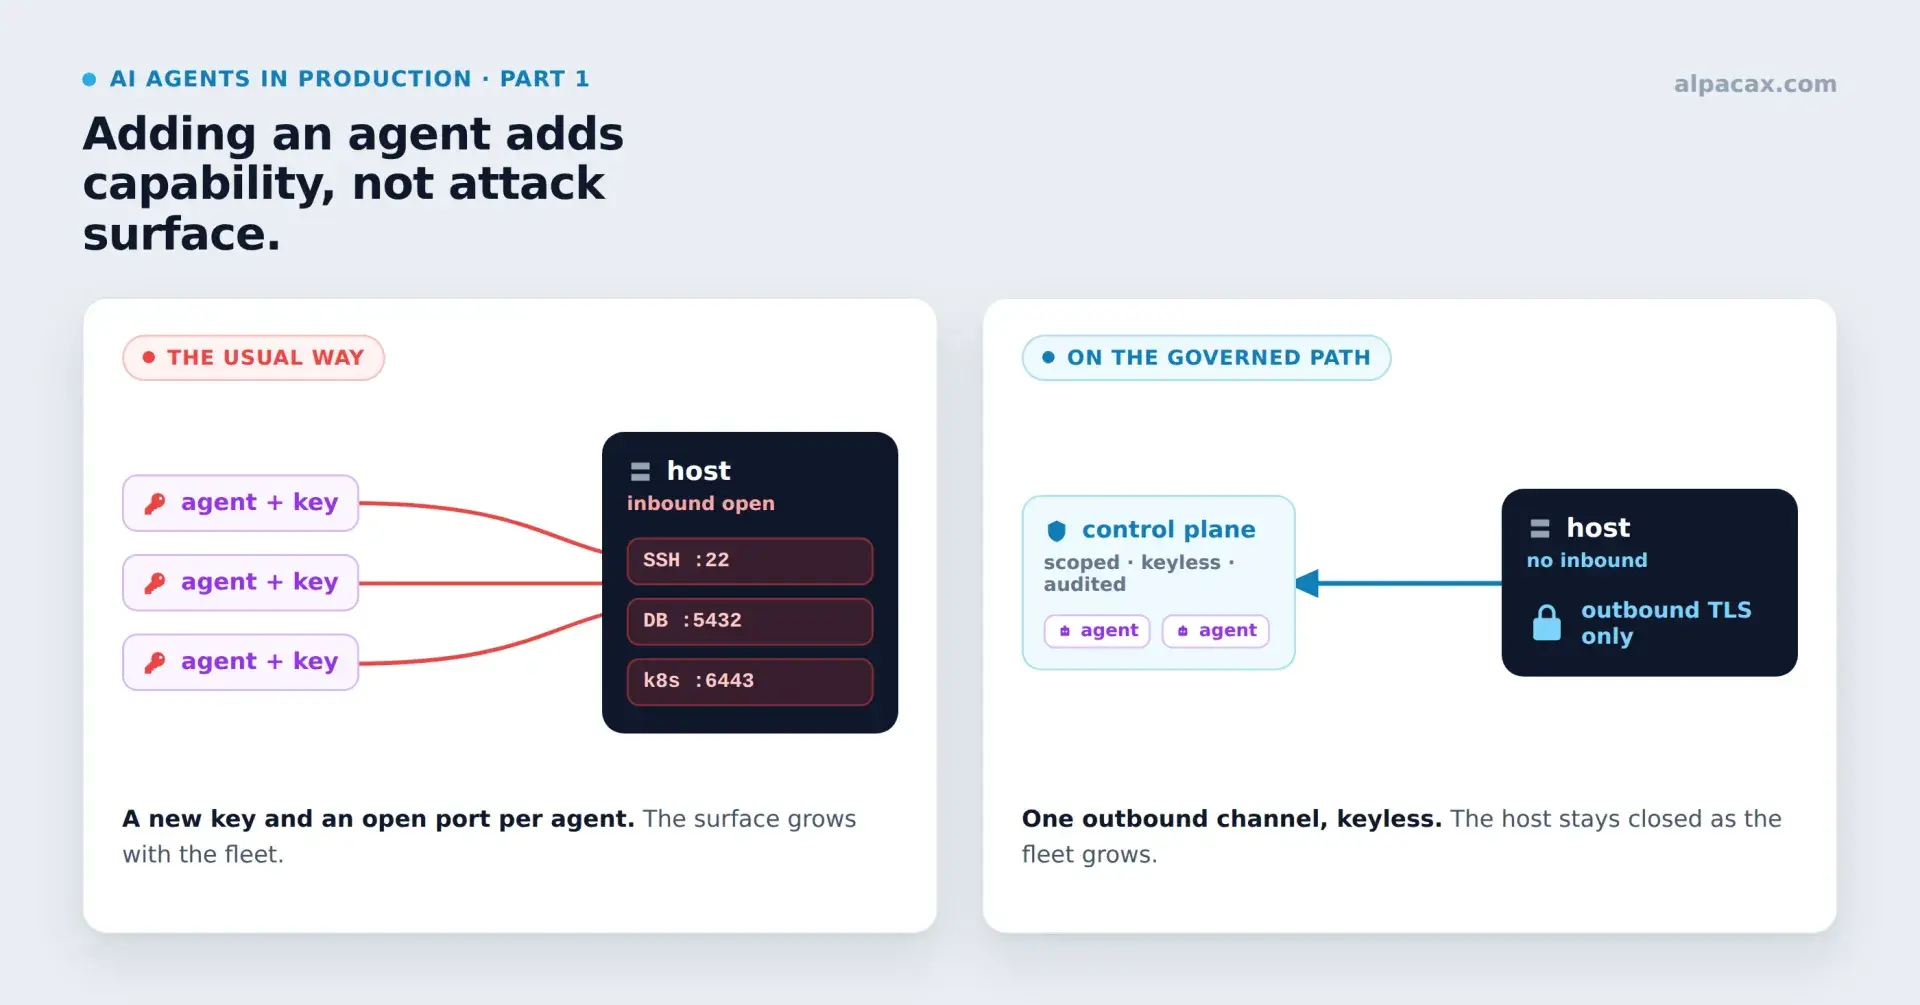
Adding AI agents shouldn't mean adding more security exposure
Expanding your attack surface isn't the price of an AI agent. It's an artifact of how you wire it in – and it's avoidable.
Incident
The gate worked. The database was still dumped.
Sysdig documented the first in-the-wild LLM agent intrusion: four pivots, every access gate cleared, database exfiltrated. The layer neither covers.
Product
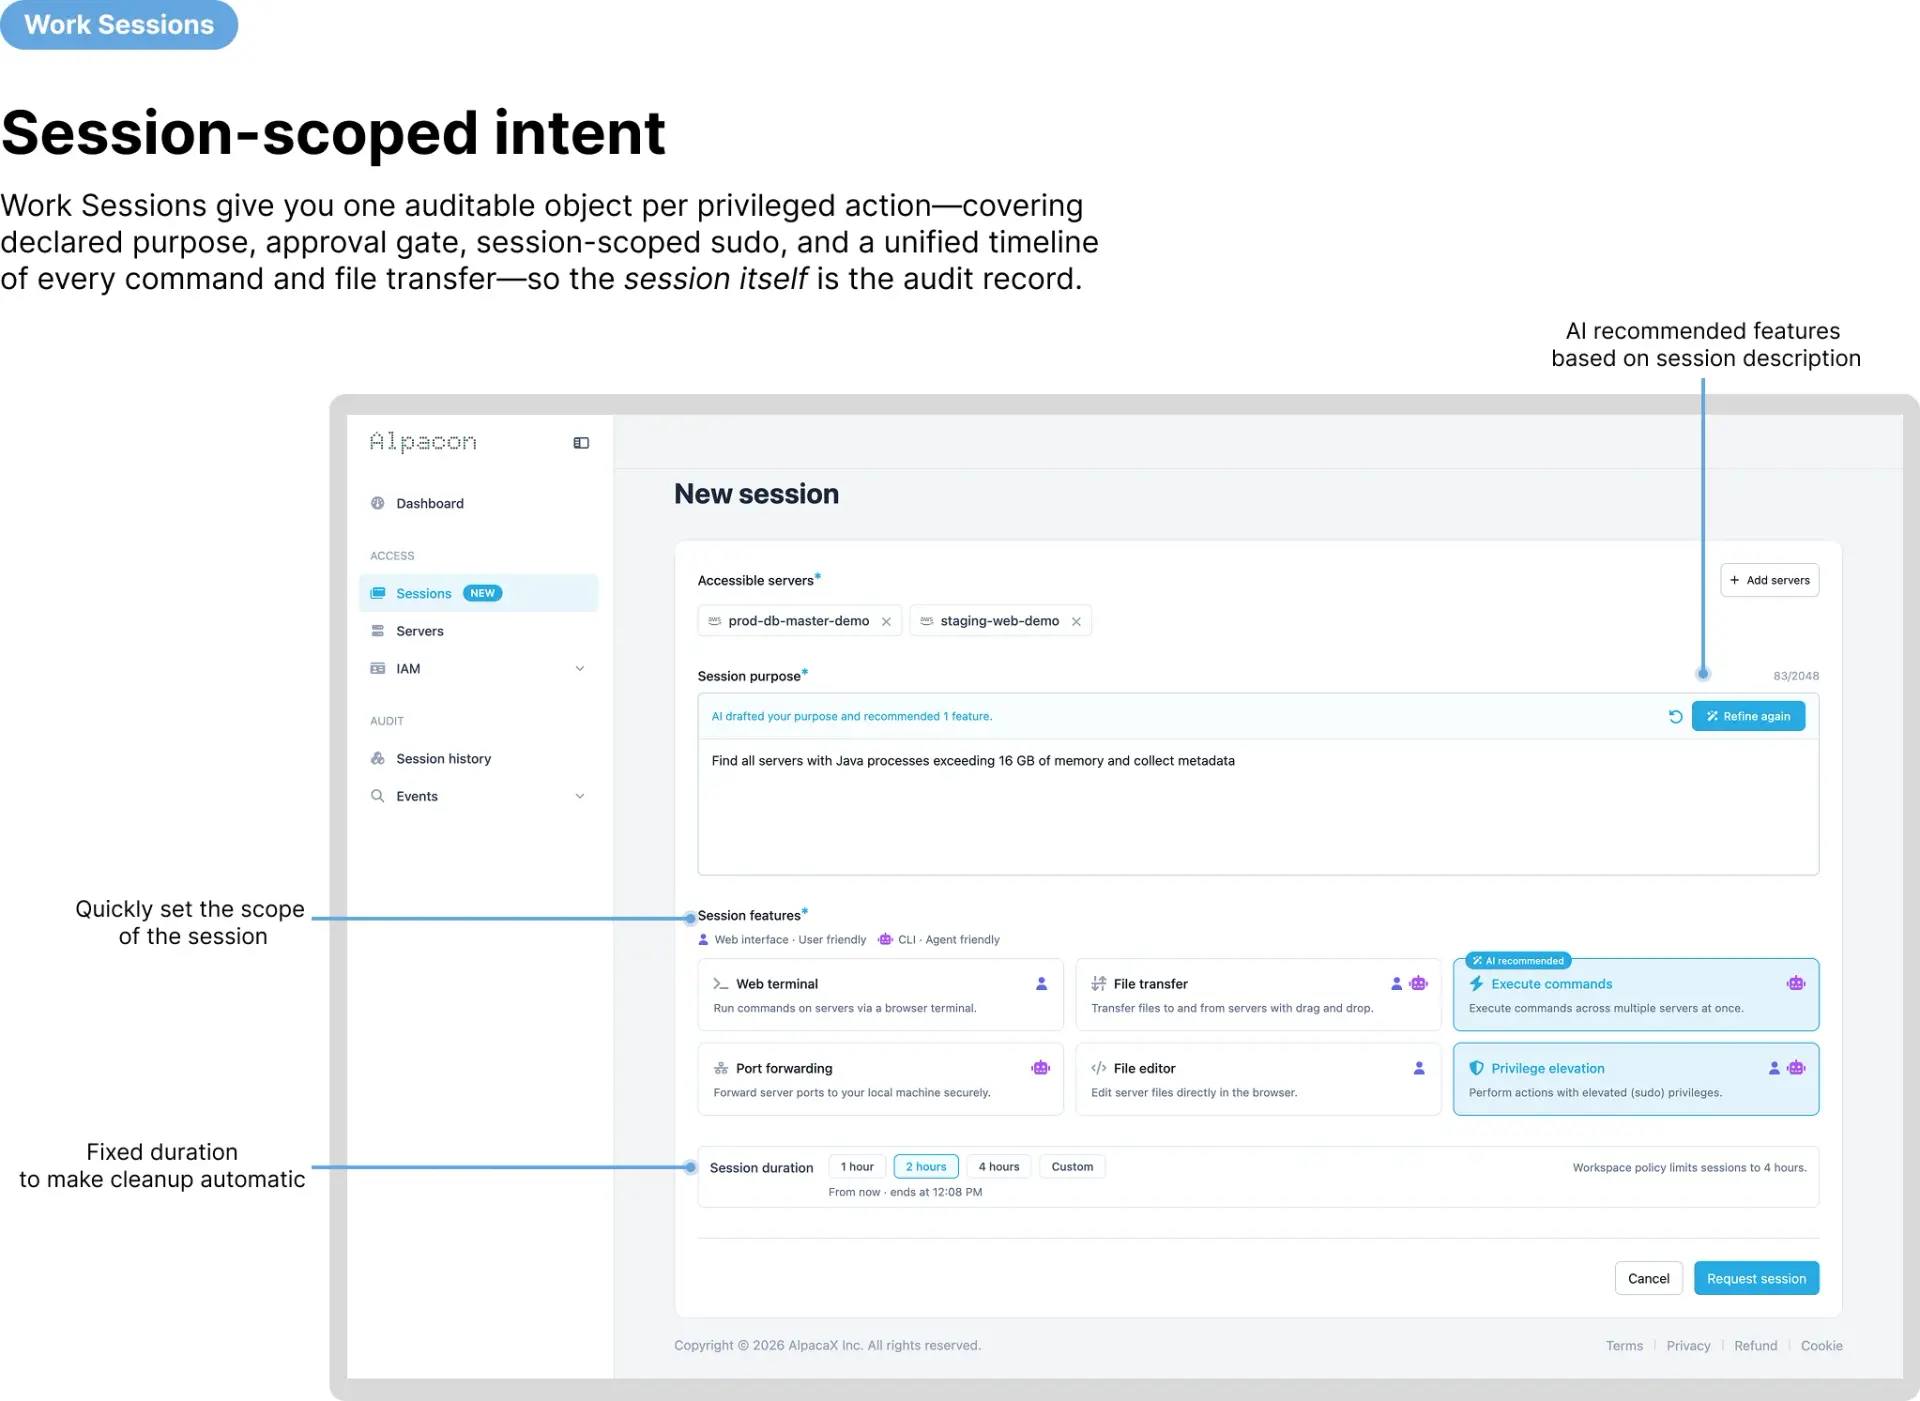
Work Sessions: the audit unit your CISO actually needs
Alpacon's Work Sessions turn fragmented audit timelines into one object – declared intent, approval gate, session-scoped sudo, unified record.
