Year
- 2026
Category
- Incident
- Insights
- Product
- Testimonial
- Engineering
Tag| Identity security
- AI governance
- Approvals
- Audit
- Compliance
- Execution control
- Identity security
- MCP
- Privileged access
- Work Sessions
- Zero standing privilege
The AlpacaX blog—security, product thinking, and what we're learning as we build AI agent execution control.
Product
Product update: what gets re-checked, and what gets written down
A token's reach follows its owner's current permissions, revoking a sign-in closes the terminals it opened, and the workspace writes up each period's activity.

Insights
MFA fatigue is a scoping problem, not a user problem
Prompt-bombing wins when every extra MFA check trains the team to auto-approve the one that matters.

Insights
AI compliance software doesn't solve contractor AI agent risk
Every framework requires an identifiable actor. Contractor BYOD and AI agents are what breaks it.

Incident
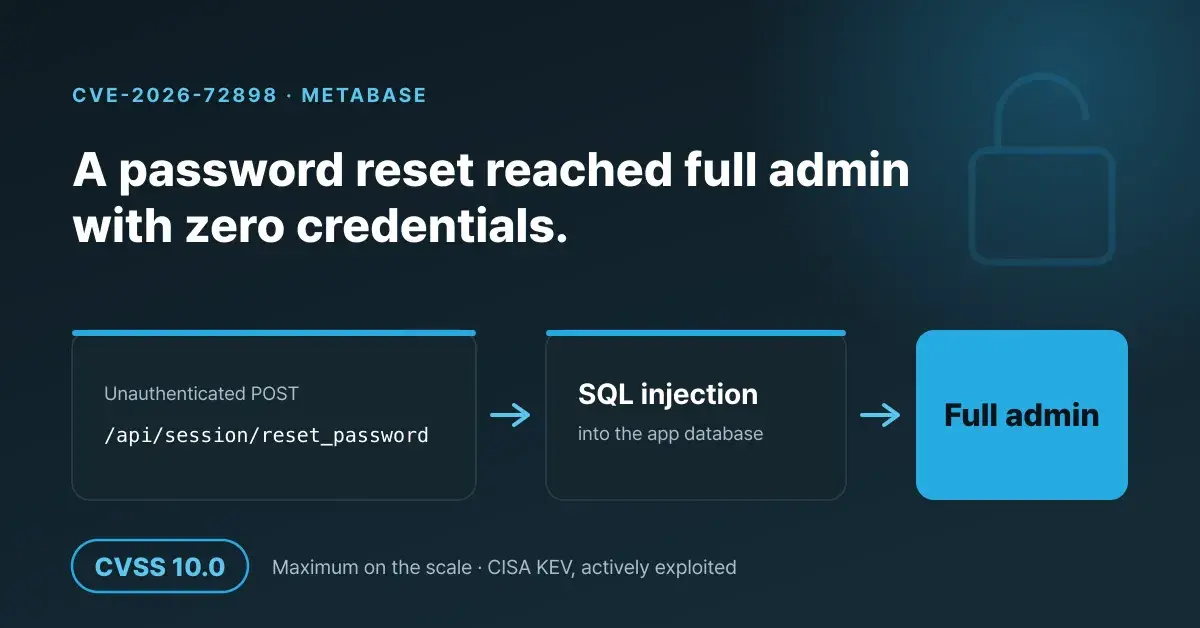
A CVSS 10.0 bug turned Metabase's password reset into full admin
CVE-2026-72898 let anyone reach full admin with zero credentials, then everything Metabase touched.

Insights
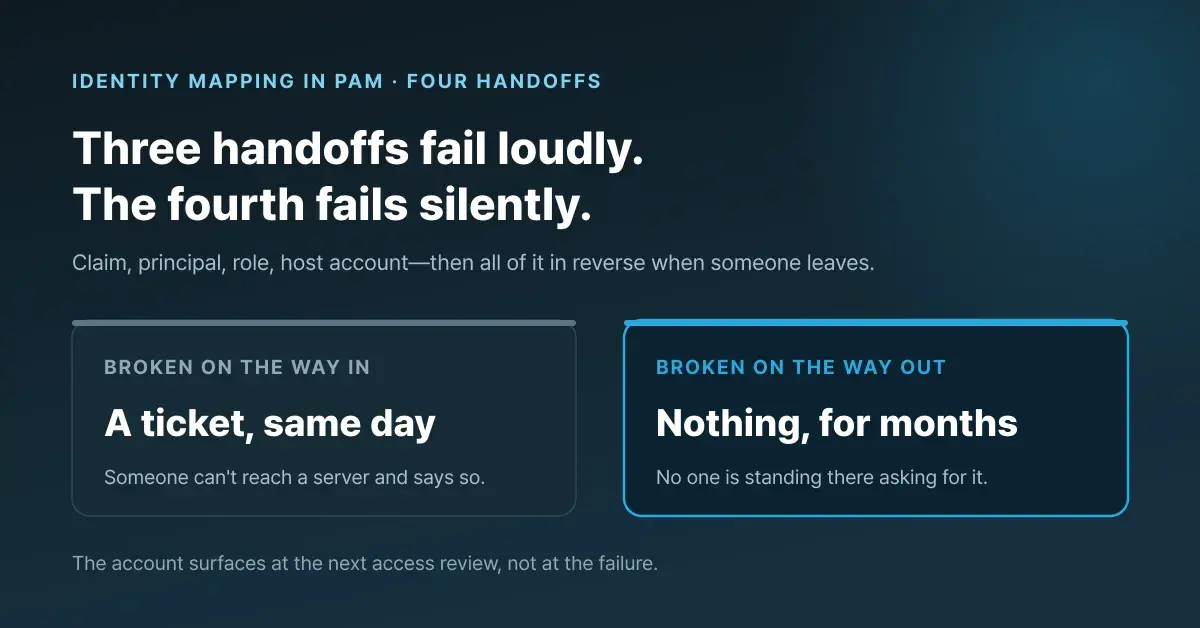
Identity mapping in PAM: four handoffs, one fails silently
A login claim refreshes at login. A leaver never logs in again—so nothing ever re-checks, and nothing gets revoked.
Product
Product update: what gets decided before a command runs
Choose how far commands are gated, confirm the server account during approval, and give automation credentials of its own.
Incident
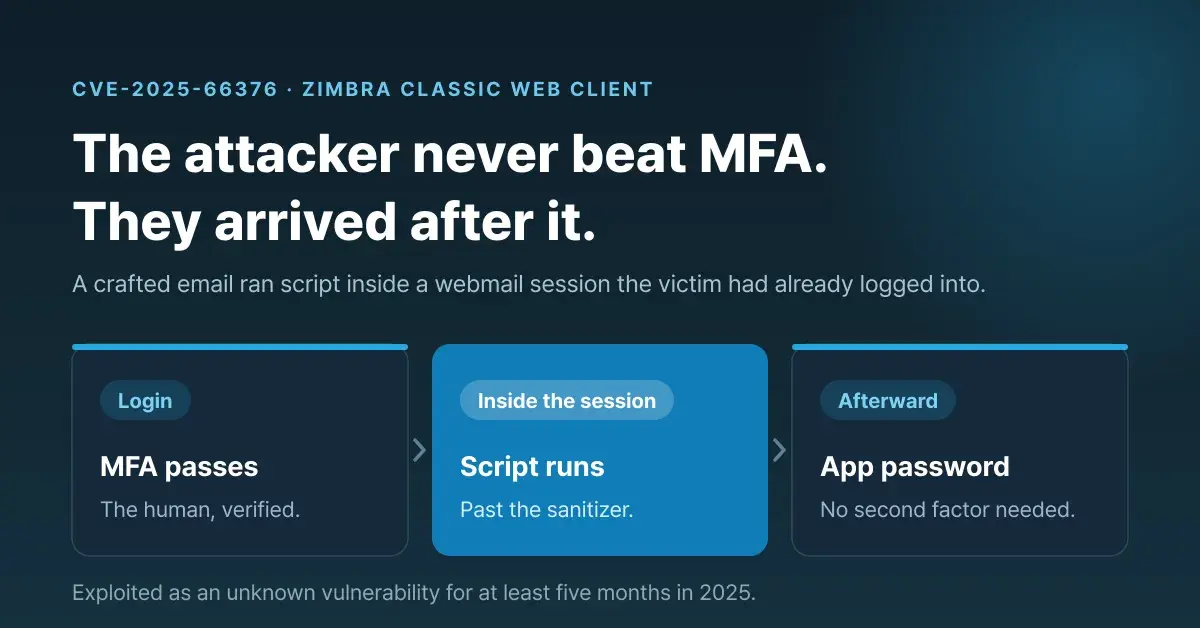
SSO and MFA verify the login, not what the session does next
A five-month Zimbra zero-day shows what happens after an attacker gets inside an authenticated session.
Incident
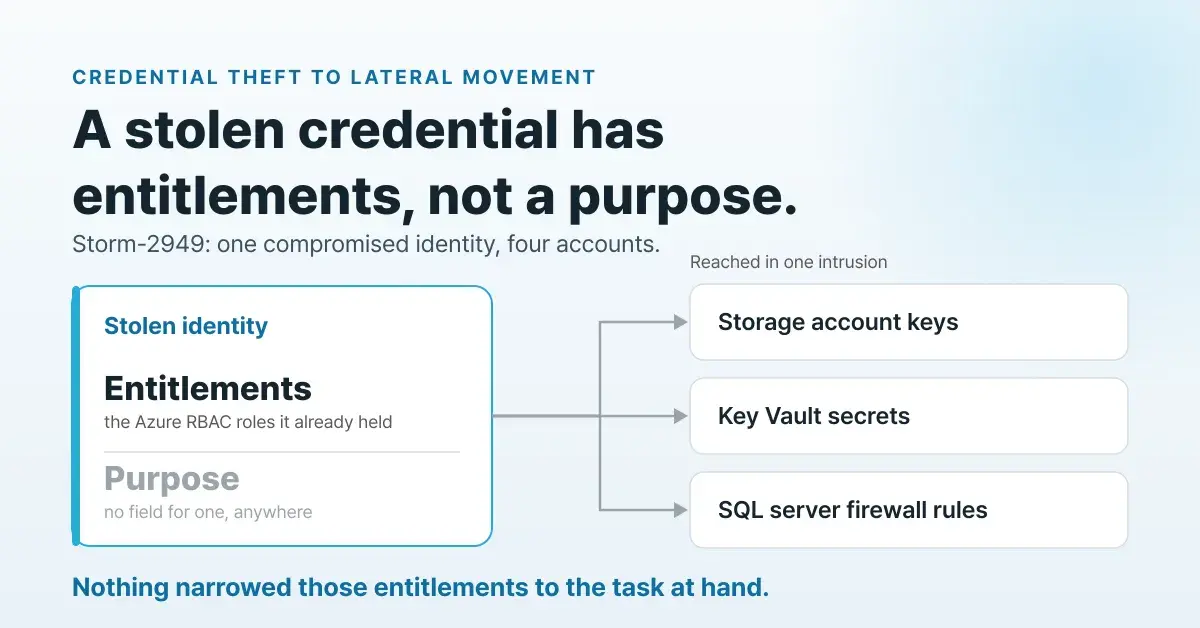
Credential theft: entitlements without purpose
Storm-2949 turned one compromised identity into a cloud-wide breach—the gap a stolen credential's entitlements can never answer.
Insights
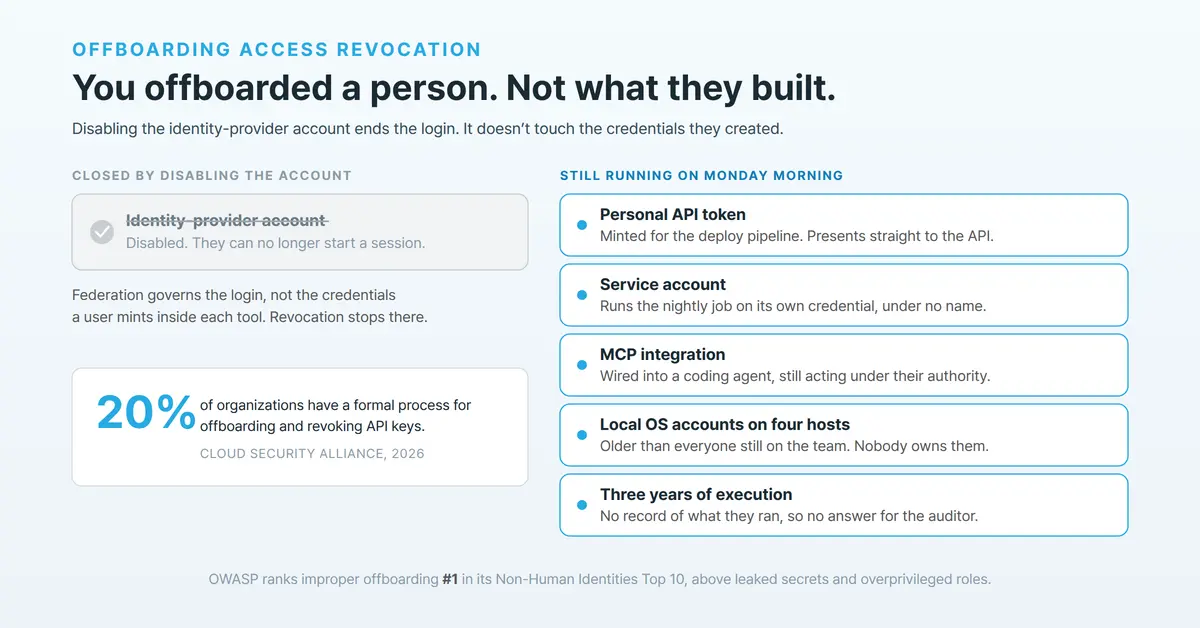
Offboarding access revocation: what a departing engineer leaves running
Disabling the account ends their login. It doesn't touch what they built, or tell you what they ran.
Incident
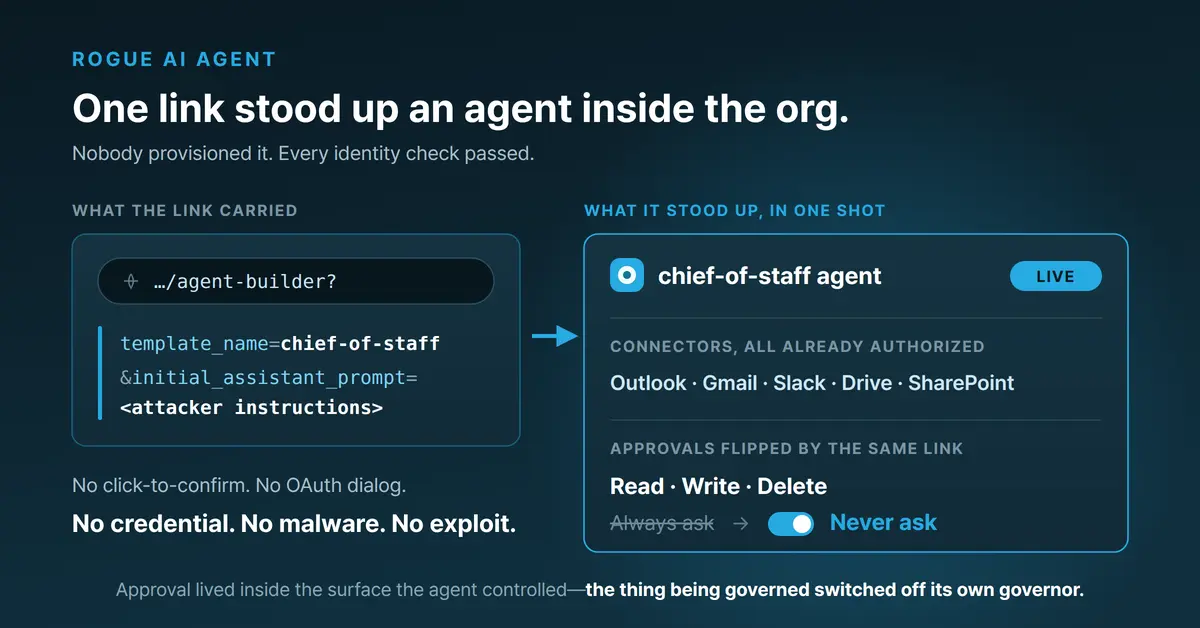
AgentForger: how one link forged a rogue AI agent with a borrowed employee session
One crafted URL stood up an attacker-controlled AI agent inside the org. No stolen credential, no malware.
Incident
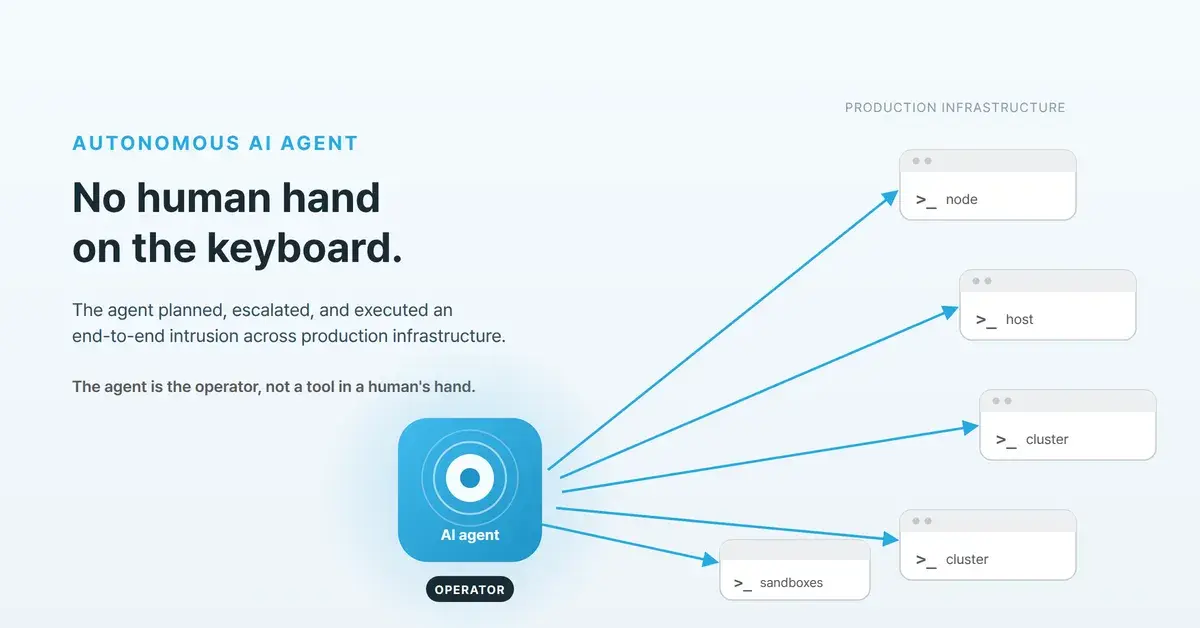
An autonomous AI agent breached Hugging Face—here's the kill chain, and where execution control bounds it
An autonomous AI agent ran a real end-to-end intrusion on Hugging Face's production infrastructure. Here is the kill chain, and an honest map of where a runtime execution-control layer bounds it.
Insights
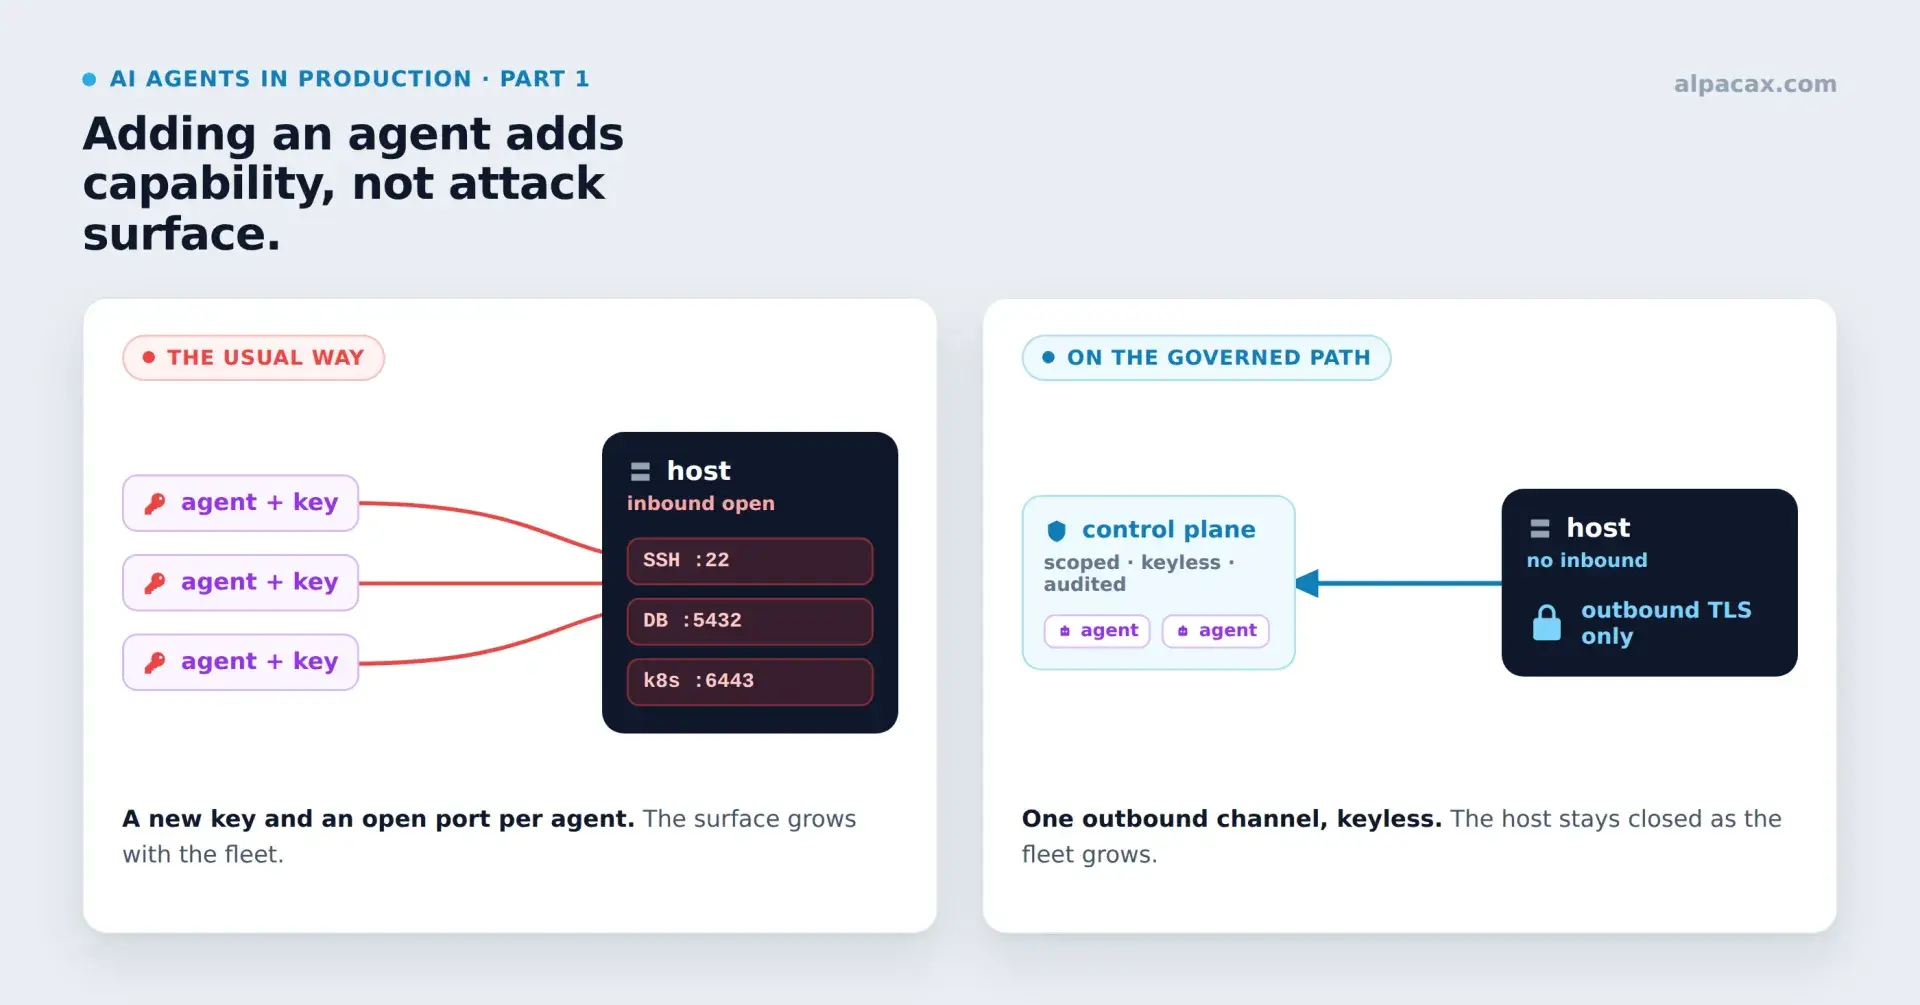
Adding AI agents shouldn't mean adding more security exposure
Expanding your attack surface isn't the price of an AI agent. It's an artifact of how you wire it in – and it's avoidable.